
- Home
- Cisco Certifications
- 300-730 Implementing Secure Solutions with Virtual Private Networks (SVPN 300-730) Dumps
Pass Cisco SVPN 300-730 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!

300-730 Premium Bundle
- Premium File 261 Questions & Answers. Last update: Oct 01, 2026
- Training Course 42 Video Lectures
- Study Guide 1007 Pages
Last Week Results!
 83% students found the test questions almost same
Includes question types found on the actual exam such as drag and drop, simulation, type-in and fill-in-the-blank.
Based on real-life scenarios similar to those encountered in the exam, allowing you to learn by working with real equipment.
Developed by IT experts who have passed the exam in the past. Covers in-depth knowledge required for exam preparation.
All Cisco SVPN 300-730 certification exam dumps, study guide, training courses are Prepared by industry experts. PrepAway's ETE files povide the 300-730 Implementing Secure Solutions with Virtual Private Networks (SVPN 300-730) practice test questions and answers & exam dumps, study guide and training courses help you study and pass hassle-free!
300-730 SVPN: Retired Cisco VPN Implementation Exam
Cisco retired the 300-730 SVPN exam on August 26, 2026. There is no direct replacement concentration exam, so this page should no longer be read as a current booking target. Historically, SVPN validated implementation and troubleshooting of site-to-site and remote-access VPN technologies and contributed to CCNP Security as the Network Security VPN Implementation concentration.
The subject itself remains important. Cisco explicitly kept VPN fundamentals in the current 350-701 security core and moved firewall-based VPN configuration into the firewall concentration. That is a better reflection of how VPN expertise is used today: as part of a broader security role rather than as a professional-level concentration centered almost entirely on manual VPN implementation.
For engineers who still operate ASA, Secure Firewall, IOS XE routers, DMVPN, IPsec, or remote-access VPNs, the old SVPN blueprint remains a strong skills map. The key is to preserve its historical certification status while continuing to learn the technologies that remain in production.
IPsec knowledge is the foundation for every SVPN-style design
Before comparing VPN products, understand the security services a tunnel must provide: peer authentication, confidentiality, integrity, replay protection, and key management. IKE negotiates security associations and establishes trust; IPsec protects the data plane. When a tunnel fails, knowing which phase is broken is more useful than memorizing a list of commands.
Practice reading proposal parameters, identities, certificates or pre-shared keys, traffic selectors, transform settings, lifetimes, and routing. A mismatch can prevent negotiation even when basic IP connectivity is fine. Likewise, a tunnel can come up while user traffic still fails because interesting traffic, NAT, routes, access control, or return paths are wrong.
Site-to-site VPNs differ in topology, control, and scalability
The former blueprint covered GETVPN, DMVPN, FlexVPN, and conventional IPsec approaches. These technologies solve related but different problems. DMVPN uses multipoint GRE, NHRP, and IPsec to scale dynamic spoke connectivity. FlexVPN uses IKEv2 and a more unified framework. GETVPN protects traffic while preserving the original IP header, which suits specific private WAN designs.
A useful study method is to compare each option by topology, routing behavior, peer discovery, encryption model, hub dependency, multicast needs, and operational scale. Do not choose a technology because it is “more modern†in the abstract. Choose it because its properties fit the business and network requirements presented.
Remote access combines identity, client behavior, and tunnel policy
Remote-access VPNs add user and endpoint context to the cryptographic problem. The legacy SVPN scope included AnyConnect IKEv2, SSL VPN, clientless SSL VPN, and FlexVPN-based remote access. Today the client branding has moved to Cisco Secure Client, but the engineering questions remain familiar: how is the user authenticated, which address is assigned, what traffic enters the tunnel, what routes and DNS settings are delivered, and what happens when posture or identity checks fail?
Split tunneling deserves special attention because it changes both security and performance. Sending all traffic through the corporate headend maximizes central inspection but increases bandwidth and latency demands. Selective tunneling can improve user experience but requires clear decisions about which destinations bypass the enterprise path and which controls protect that traffic elsewhere.
Certificates and AAA often decide whether a tunnel is operationally trustworthy
VPN security is not only about ciphers. Certificates provide scalable machine and gateway identity, while RADIUS, LDAP, local databases, or other AAA integrations can validate users and assign policy. A certificate problem can look like a negotiation failure; an AAA failure can allow the tunnel setup to progress further before access is denied.
Study trust chains, certificate identity, revocation, time validity, group policies, authorization attributes, and authentication order. The broader identity principles used in Cisco ISE and secure-access solutions matter here as well. Troubleshooting should identify whether failure occurs at peer trust, user authentication, authorization, address assignment, or data forwarding.
Routing deserves equal attention because encryption does not automatically create a usable path. Dynamic routing over tunnels, recursive next-hop problems, asymmetric return paths, and overlapping networks can all break application traffic while the cryptographic state appears healthy. In hub-and-spoke designs, understand how spoke-to-spoke routes are learned and how failure of a hub or underlay path affects reachability. A VPN design is a routing design with additional security state, not a separate layer that can be studied independently.
High availability is part of VPN design, not an afterthought
A secure tunnel is useful only if the service survives realistic failures. Site-to-site designs need resilient headends, routing convergence, consistent cryptographic policy, and failover behavior that does not create asymmetric paths. Remote access needs capacity planning, multiple termination points where appropriate, DNS and certificate continuity, and an understanding of what state is or is not preserved during failover.
Capacity also matters. Encryption consumes resources, remote users create bursty demand, and full-tunnel designs can drive significant internet and inspection traffic through the headend. A sound design considers throughput, session counts, authentication dependencies, and the effect of rekey or reconnection events during an outage.
NAT is another frequent source of confusion. Site-to-site protected traffic may require identity or exemption treatment so that the addresses used by the encryption policy match the intended selectors. Remote-access clients may need internet access through the headend, access to overlapping internal ranges, or translation for specific destinations. Always compare the pre-NAT and post-NAT packet with the crypto policy rather than assuming a tunnel failure when the real issue is address transformation.
Troubleshooting should follow the tunnel establishment sequence
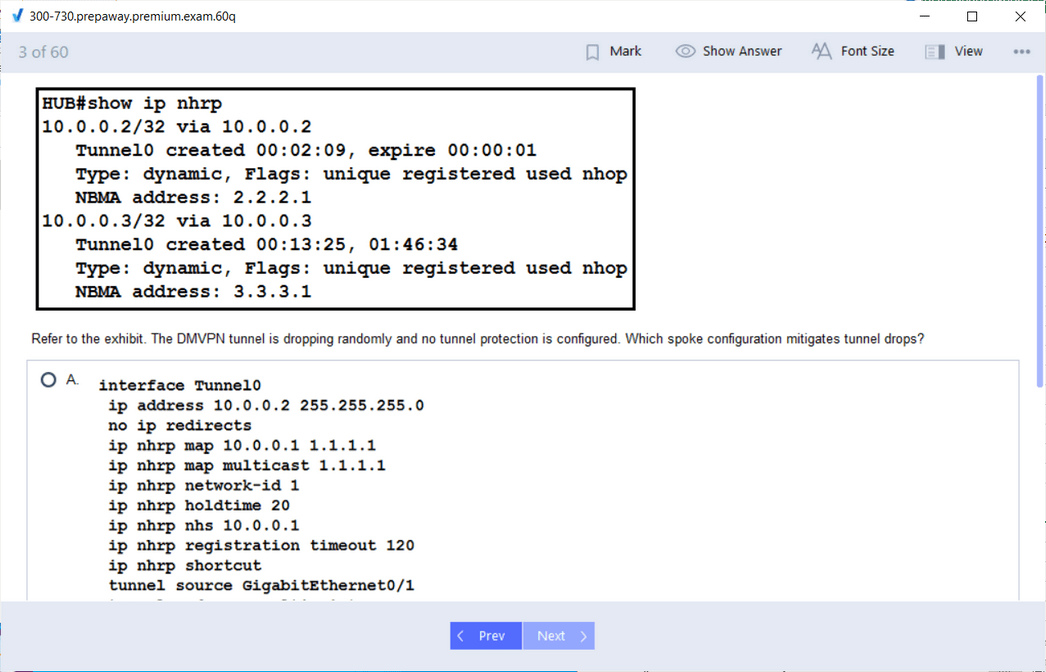
SVPN placed heavy weight on troubleshooting, and that emphasis remains valuable. Start with reachability. Then check IKE negotiation, peer identity, proposals, authentication, security associations, protected subnets, NAT behavior, routing, and policy. For DMVPN, add NHRP and tunnel-state checks. For remote access, add client logs, AAA, group policy, address pools, DNS, and split-tunnel rules.
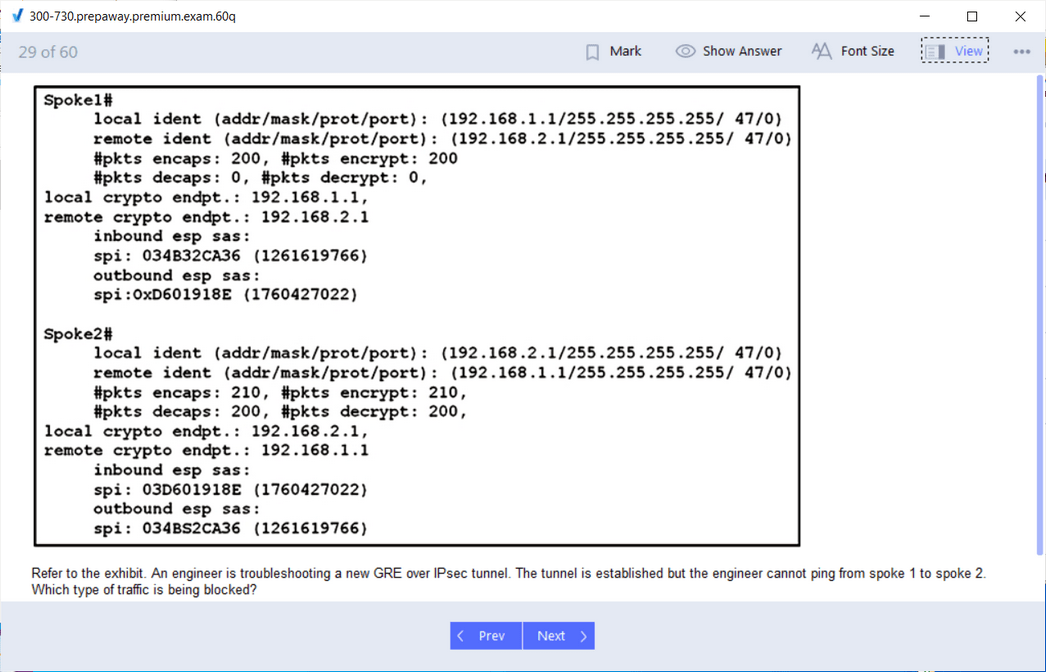
A common mistake is to jump directly to packet captures or change encryption settings without proving the failing stage. Use debugs and show commands carefully, correlate timestamps, and compare both peers. When a tunnel is established but data fails, treat the problem as forwarding and policy until evidence says otherwise.
VPN content now lives inside broader Security exams
Cisco’s current guidance is explicit: after retiring SVPN, VPN fundamentals remain in 350-701 SCOR, while firewall-based VPN configuration is represented in 300-710 SNCF. That is not a one-to-one replacement for the old concentration; it redistributes the knowledge into broader core and firewall roles.
The current 300-740 SSCA path also changes the remote-access conversation by emphasizing zero-trust private access, Secure Access, Secure Client, SSE, and cloud-delivered policy. Again, this is not “the new SVPN.†It reflects a different operating model in which users and applications may be connected through identity-aware cloud services instead of a traditional concentrator tunnel.
Logging strategy matters during intermittent failures. IKE and IPsec debugs can be verbose, so capture them around a reproducible event and correlate the output with packet counters, routing, and peer logs. For remote users, collect client-side diagnostics as well. A gateway may show a successful authentication while the client records a posture, DNS, or route-installation problem that explains why applications still fail.
Legacy product names should be translated into current operational language
Older SVPN material frequently uses ASA and AnyConnect terminology because those products were central when the blueprint was created. Current environments may use Cisco Secure Firewall and Cisco Secure Client while preserving many of the same IPsec, TLS, AAA, certificate, and routing fundamentals. Candidates and practitioners should recognize both names so they can read historical configurations without assuming the software stack is frozen in time.
The same rule applies to management interfaces. ASDM-era workflows may still exist, but modern operations often involve centralized firewall management, automation, and cloud-delivered controls. Treat old screenshots as implementation history; treat protocol behavior as the durable knowledge.
Security policy should also define what a tunnel is allowed to reach after it is established. A technically successful VPN that provides broad unnecessary access can undermine segmentation. Apply least privilege through group policy, firewall rules, route controls, and identity-aware authorization where appropriate. This is one reason Cisco’s current program distributes VPN knowledge across broader security exams: the tunnel is only one component of a secure-access architecture.
Migration planning is another useful exercise. When moving from a legacy remote-access concentrator to Secure Firewall or a cloud-delivered access model, inventory authentication methods, certificates, address pools, split-tunnel rules, DNS behavior, posture integrations, and application dependencies before changing the termination point. Users care about whether applications still work, not whether the new tunnel uses a newer product name. A phased migration with representative pilot users exposes policy gaps before they affect the entire remote workforce.
Document working-state outputs before an incident. Known-good IKE security associations, route tables, tunnel status, address pools, and firewall counters provide a baseline that makes later comparison much faster. This is especially useful for intermittent remote-access issues where the environment may recover before an engineer can reproduce the original failure.
Include IPv6 and dual-stack considerations where they exist in the environment. A VPN service may protect one address family correctly while routes or policies for the other are incomplete, creating selective application failures that are easy to misdiagnose.
Study SVPN as a practical troubleshooting discipline
The strongest way to use this retired blueprint is to build small scenarios: a site-to-site tunnel with mismatched selectors, a DMVPN spoke with an NHRP issue, a remote-access user with a certificate problem, a split-tunnel policy that sends the wrong prefix, or a firewall rule that blocks protected traffic after the tunnel forms. Diagnose each problem from evidence rather than from guesswork.
Then connect those skills to the current Cisco certifications path instead of searching for a successor code that does not exist. VPN engineering remains relevant, but 300-730 itself is historical. That distinction keeps both the technical guidance and the certification guidance accurate.
Cisco SVPN 300-730 practice test questions and answers, training course, study guide are uploaded in ETE Files format by real users. Study and Pass 300-730 Implementing Secure Solutions with Virtual Private Networks (SVPN 300-730) certification exam dumps & practice test questions and answers are to help students.
- 200-301 - Cisco Certified Network Associate (CCNA)
- 350-401 - Implementing Cisco Enterprise Network Core Technologies (ENCOR)
- 300-410 - Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- 350-701 - Implementing and Operating Cisco Security Core Technologies
- 300-415 - Implementing Cisco SD-WAN Solutions (ENSDWI)
- 300-420 - Designing Cisco Enterprise Networks (ENSLD)
- 350-601 - Implementing and Operating Cisco Data Center Core Technologies (DCCOR)
- 810-110 - Cisco AI Technical Practitioner (AITECH)
- 300-715 - Implementing and Configuring Cisco Identity Services Engine (300-715 SISE)
- 350-101 - Implementing and Operating Cisco Wireless Core Technologies (WLCOR)
- 350-801 - Implementing Cisco Collaboration Core Technologies (CLCOR)
- 350-501 - Implementing and Operating Cisco Service Provider Network Core Technologies (SPCOR)
- 350-201 - Performing Cybersecurity Using Cisco Security Technologies (CBRCOR)
- 400-007 - Cisco Certified Design Expert
- 200-901 - DevNet Associate (DEVASC)
- 500-220 - Cisco Meraki Solutions Specialist
- 200-201 - Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- 300-710 - Securing Networks with Cisco Firewalls
- 300-620 - Implementing Cisco Application Centric Infrastructure (DCACI)
- 100-150 - Cisco Certified Support Technician (CCST) Networking
- 300-730 - Implementing Secure Solutions with Virtual Private Networks (SVPN 300-730)
- 350-901 - Designing, Deploying, and Managing Network Automation Systems
- 820-605 - Cisco Customer Success Manager (CSM)
- 300-110 - Designing Cisco Wireless Networks (WLSD)
- 300-640 - Implementing Cisco Data Center AI Infrastructure (DCAI)
- 300-510 - Implementing Cisco Service Provider Advanced Routing Solutions (SPRI)
- 800-150 - Supporting Cisco Devices for Field Technicians
- 300-435 - Automating Cisco Enterprise Solutions (ENAUTO)
- 300-745 - Designing Cisco Security Infrastructure
- 300-815 - Implementing Cisco Advanced Call Control and Mobility Services (CLASSM)
- 700-805 - Cisco Renewals Manager (CRM)
- 500-442 - Administering Cisco Contact Center Enterprise
- 300-720 - Securing Email with Cisco Email Security Appliance (300-720 SESA)
- 300-610 - Designing Cisco Data Center Infrastructure for Traditional and AI Workloads
- 300-440 - Designing and Implementing Cloud Connectivity (ENCC)
- 300-425 - Designing Cisco Enterprise Wireless Networks (300-425 ENWLSD)
- 100-160 - Cisco Certified Support Technician (CCST) Cybersecurity
- 100-140 - Cisco Certified Support Technician (CCST) IT Support
- 300-515 - Implementing Cisco Service Provider VPN Services (SPVI)
- 300-220 - Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
- 300-215 - Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR)
- 500-560 - Cisco Networking: On-Premise and Cloud Solutions (OCSE)
- 300-830 - Implementing Cisco Collaboration Cloud Customer Experience (CLCCE)
- 700-750 - Cisco Small and Medium Business Engineer
- 700-246 - Cisco Environmental Sustainability Practice-Building - Stage 2 (CESPB)
- 700-242 - Cisco Environmental Sustainability Fundamentals - Stage 1 (CESF)
- 500-470 - Cisco Enterprise Networks SDA, SDWAN and ISE Exam for System Engineers (ENSDENG)
- 500-443 - Advanced Administration and Reporting of Contact Center Enterprise
- 300-445 - Designing and Implementing Enterprise Network Assurance
- 300-430 - Implementing Cisco Enterprise Wireless Networks (300-430 ENWLSI)
- 300-615 - Troubleshooting Cisco Data Center Infrastructure (DCIT)
- 300-725 - Securing the Web with Cisco Web Security Appliance (300-725 SWSA)
- 300-820 - Implementing Cisco Collaboration Cloud and Edge Solutions
- 010-151 - Supporting Cisco Data Center System Devices (DCTECH)
Purchase Cisco 300-730 Exam Training Products Individually
Why customers love us?
What do our customers say?
The resources provided for the Cisco certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the 300-730 test and passed with ease.
Studying for the Cisco certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the 300-730 exam on my first try!
I was impressed with the quality of the 300-730 preparation materials for the Cisco certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The 300-730 materials for the Cisco certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the 300-730 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my Cisco certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for 300-730. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the 300-730 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my 300-730 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my Cisco certification without these amazing tools!
The materials provided for the 300-730 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed 300-730 successfully. It was a game-changer for my career in IT!


