200-201 CCNA Cybersecurity: Current Cisco Security Operations Exam
200-201 is Cisco's current associate-level cybersecurity operations exam. In February 2026, Cisco aligned the former Cybersecurity Associate branding with the CCNA family, and the exam is now identified as 200-201 CCNACBR. The underlying focus remains security monitoring, analysis and response in operational environments.
Passing 200-201 earns CCNA Cybersecurity. The exam sits above entry-level 100-160 CCST Cybersecurity and within the broader Cisco certification portfolio. The approved CyberOps Associate lineage is still useful historical context, but current candidates should use Cisco's CCNA Cybersecurity name and current blueprint.
The 2026 rename is more than a cosmetic detail for readers using older resources. Cisco's previous CBROPS and Cybersecurity Associate terminology can still appear in course notes, internal learning plans and PrepAway destinations, but the live credential is CCNA Cybersecurity and the exam identifier is CCNACBR. Translate the old names rather than assuming they represent a different current exam.
Security concepts provide the vocabulary for operational analysis
The current blueprint begins with security concepts such as confidentiality, integrity and availability, threat intelligence, risk, vulnerability, exploit, access-control models and defense in depth. These ideas matter because analysts need a common way to describe what is at risk and why a control or response action is appropriate.
Do not study the terms as isolated definitions. Take a compromised user account and map the threat actor, weakness, possible exploit, affected assets and controls. Then ask how the incident changes confidentiality, integrity or availability. That exercise turns terminology into a framework for analysis.
Defense in depth also helps analysts interpret failures. One control may miss an event while another detects or limits it. A phishing message can bypass an email filter yet still be stopped by endpoint protection or restricted by identity controls. Candidates should be able to describe how layered controls reduce dependence on any single technology.
Security monitoring depends on knowing which data source answers which question
Analysts work with logs and telemetry from endpoints, network devices, applications, identity systems and security platforms. A useful skill is knowing what evidence each source can provide. DNS logs may show name-resolution activity, firewall records can show allowed or denied connections, and endpoint telemetry can reveal process or file behavior.
Monitoring is not the same as collecting everything. The analyst should understand what normal activity looks like, which events deserve priority and how timestamps and identities line up across systems. Good preparation uses small scenarios where several data sources tell different parts of the same story.
Time normalization is essential when multiple systems contribute evidence. If one log uses UTC and another uses local time, events can appear out of sequence. Analysts should confirm timestamps, time zones and clock accuracy before building a timeline. This is a small operational detail that can completely change the interpretation of an incident.
Host-based analysis requires an operating-system mindset
Windows and Linux systems create processes, files, services, user sessions and logs that can reveal malicious activity. Candidates should be comfortable distinguishing normal administrative behavior from suspicious changes. A new process by itself proves little; its parent process, command line, user context, network connection and persistence behavior add meaning.
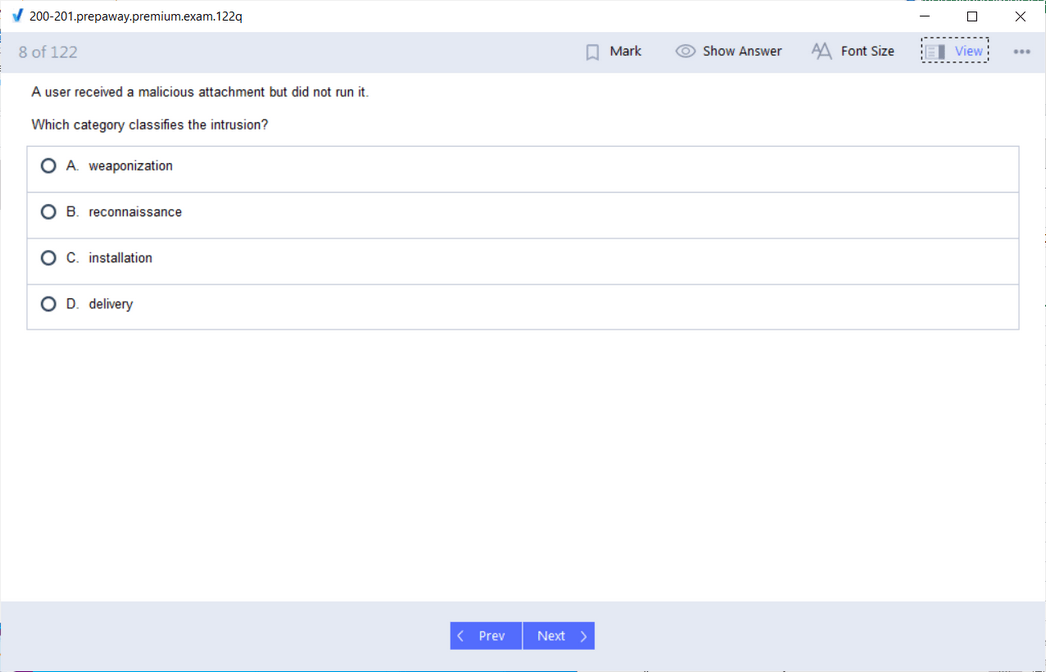
Practice following an event sequence. A phishing attachment may start a process, create a file, establish an outbound connection and add persistence. Host analysis connects those steps. The goal is to explain the evidence rather than simply recognize a malware label.
File hashes, process identifiers, user accounts and network destinations become useful when they are connected. A suspicious executable may be linked to a parent process, a downloaded file and an outbound connection. Practice building short timelines that show cause and effect. This turns host artifacts into an investigation rather than a checklist of isolated indicators.
Network intrusion analysis uses protocol behavior as evidence
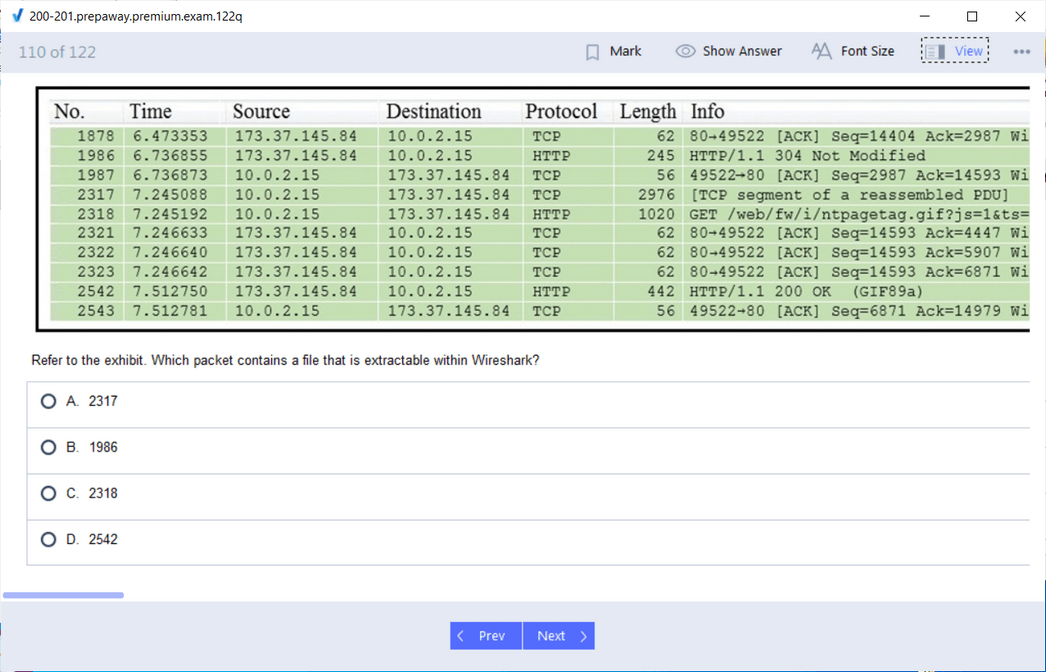
Analysts need to understand TCP/IP well enough to interpret sessions, ports, flags, addresses and common application protocols. Packet captures and network alerts are much easier to analyze when the candidate can distinguish normal connection setup from scanning, failed connections or suspicious data movement.
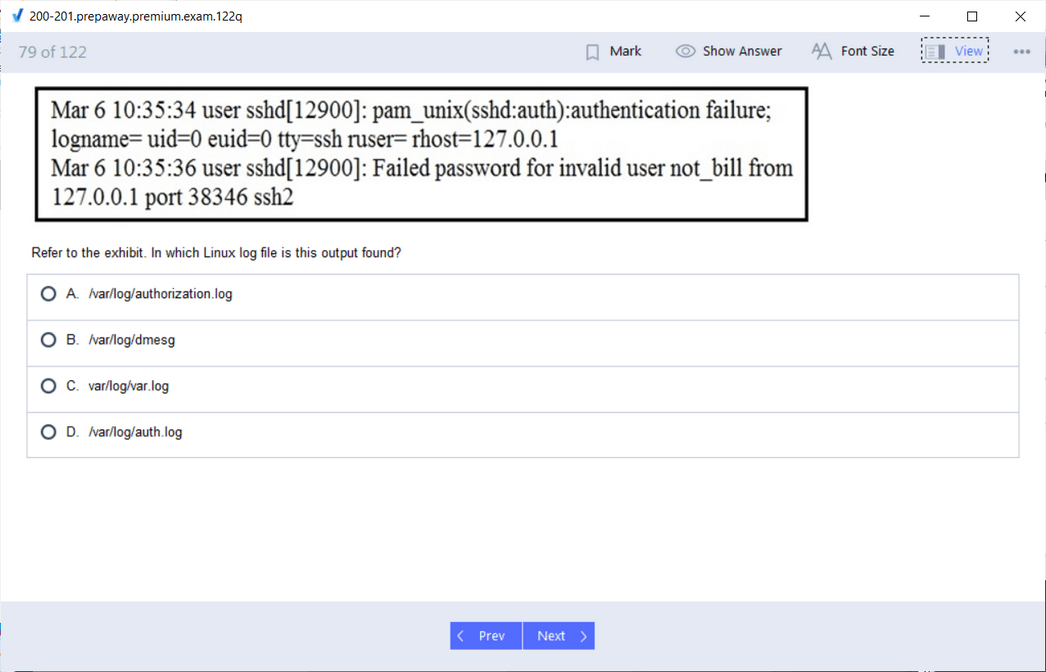
Build a small lab and observe DNS queries, HTTP or HTTPS sessions, SSH connections and failed port attempts. Look at source and destination, timing and direction. Even without advanced packet forensics, this practice develops the ability to ask whether traffic is expected for the host and role involved.
Network evidence should also be interpreted relative to architecture. A connection from a workstation to an internal management port may be more suspicious than the same port between approved administrative hosts. Segmentation, proxying and NAT can change what source or destination information means. Analysts need enough network context to avoid treating addresses as self-explanatory facts.
SIEM and SOAR concepts organize detection and response workflows
The current blueprint includes SIEM, SOAR and log-management concepts because security operations rely on centralized visibility and repeatable response. A SIEM helps collect and correlate events, while automation can enrich alerts or execute approved actions. Neither system eliminates the need for analyst judgment.
Candidates should understand why a detection rule may create false positives and why automated response needs boundaries. Blocking an address may be safe in one scenario and disruptive in another. The analyst's job is to validate context, follow the runbook and know when the situation requires escalation.
Threat intelligence is most useful when it changes a decision. An indicator may justify searching the environment, increasing the priority of an alert or blocking known malicious infrastructure. It should not replace local evidence. Candidates should understand the difference between external context and proof that a specific host in their environment is compromised.
Incident response is a controlled process, not improvised troubleshooting
Security incidents can affect evidence, legal obligations and business continuity. Analysts should understand preparation, identification, containment, eradication, recovery and lessons learned at a practical level. The exact framework may vary, but the discipline is consistent: preserve useful information and make actions traceable.
During triage, separate confirmed facts from assumptions. Record the time, affected host, user, alert source and relevant indicators. Containment should reduce harm without destroying evidence or creating a larger outage. The personal account of preparing for the 200-201 security operations exam can provide supplementary study context, but Cisco's current blueprint remains the authority.
Automation can reduce repetitive analyst work by enriching indicators, creating tickets or collecting context. It can also amplify mistakes. A playbook that automatically isolates hosts needs clear conditions and approval boundaries. The exam's inclusion of runbook automation reflects modern SOC practice: analysts must understand both the efficiency and the operational risk.
Security policies and procedures shape analyst decisions
Operational security is governed by rules about access, data handling, escalation, retention and incident communication. An analyst may technically be able to take an action yet still need authorization. Understanding policy prevents well-intentioned response from creating compliance or business problems.
Policies also make handoffs more reliable. Severity definitions, evidence-handling requirements and escalation thresholds tell analysts how to treat similar events consistently. Candidates should practice reading a scenario and identifying the policy question as well as the technical question.
Post-incident learning matters because recurring alerts often reveal control gaps. After recovery, teams should ask how the event was detected, which evidence was missing, whether escalation was timely and which safeguards should change. Candidates do not need to run a formal enterprise review, but they should understand that response is incomplete if the organization learns nothing from the event.
Case management is another operational skill worth practicing. An alert should have an owner, status, severity, evidence and next action. Even a small home lab can mimic this discipline with a simple incident template. Structured case notes make it easier to transfer work between analysts and demonstrate why the response decision was reasonable at the time.
CCNA Cybersecurity now has a clearer professional progression
Cisco's 2026 naming change places the associate credential under the CCNA brand and the professional track under CCNP Cybersecurity. Candidates who want to continue can move toward the professional core 350-201 CBRCOR and concentration areas such as incident response or threat hunting after building real analyst experience.
The progression should follow skill depth, not title collecting. At associate level, become comfortable with monitoring, host and network evidence, common attack behavior and incident workflow. Professional study becomes more useful when those foundations are already connected to operational experience.
The best progression signal is not simply passing the exam; it is being able to write a concise analyst note that another person can act on. State what triggered the investigation, what evidence supports the conclusion, what action was taken and what remains unresolved. That communication skill becomes even more important at the professional level, where incidents involve more systems and stakeholders.
Use detection rules as study prompts. Take one condition—multiple failed logins, suspicious PowerShell, unexpected DNS traffic—and list the data needed to validate it. Then identify likely benign explanations. This habit teaches candidates to challenge their first conclusion and to seek corroborating evidence, which is essential in a SOC where false positives compete with genuine incidents for attention.
Preparation should revolve around evidence and explanation
Use Cisco's current 200-201 blueprint as the final checklist. Build labs that generate normal and suspicious-looking events, inspect host logs, review packet data and write short incident notes. For each alert, explain what the evidence proves, what remains uncertain and what additional data would reduce that uncertainty.
A strong candidate can move from a security concept to an observable event and then to an appropriate response. That is the core of security operations. Memorizing tool names may help with vocabulary, but the durable skill is connecting telemetry, context and procedure into a defensible analytical conclusion.







 83% students found the test questions almost same





