
- Home
- Cisco Certifications
- 300-715 Implementing and Configuring Cisco Identity Services Engine (300-715 SISE) Dumps
Pass Cisco SISE 300-715 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!

300-715 Premium Bundle
- Premium File 407 Questions & Answers. Last update: Oct 08, 2026
- Training Course 73 Video Lectures
- Study Guide 1897 Pages
Last Week Results!
 83% students found the test questions almost same
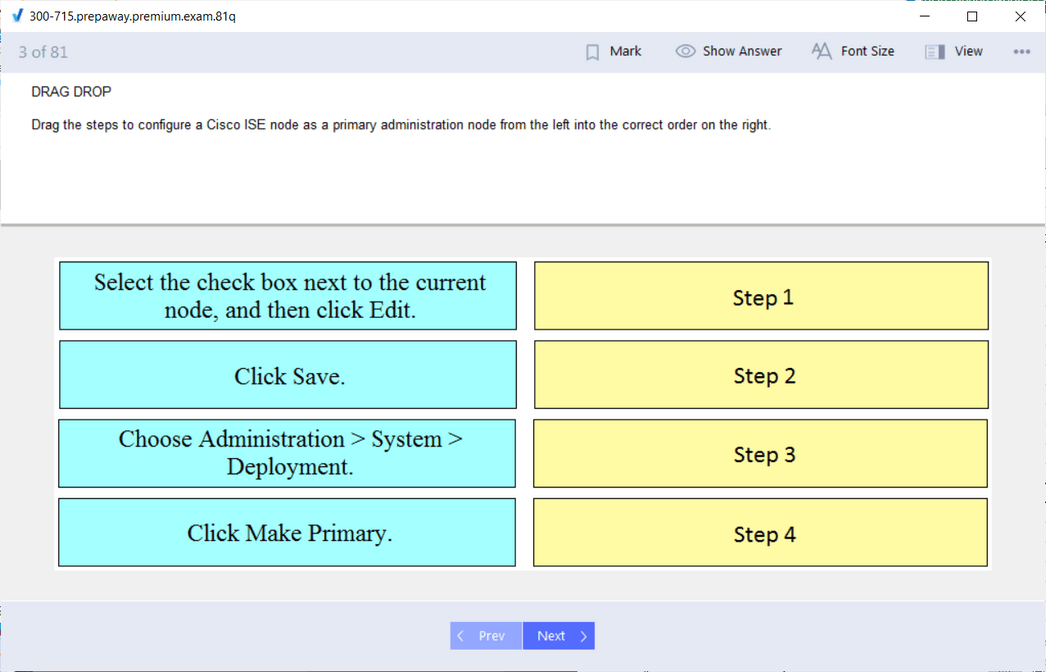
Includes question types found on the actual exam such as drag and drop, simulation, type-in and fill-in-the-blank.
Based on real-life scenarios similar to those encountered in the exam, allowing you to learn by working with real equipment.
Developed by IT experts who have passed the exam in the past. Covers in-depth knowledge required for exam preparation.
All Cisco SISE 300-715 certification exam dumps, study guide, training courses are Prepared by industry experts. PrepAway's ETE files povide the 300-715 Implementing and Configuring Cisco Identity Services Engine (300-715 SISE) practice test questions and answers & exam dumps, study guide and training courses help you study and pass hassle-free!
300-715 SISE: Implementing and Configuring Cisco Identity Services Engine
Cisco’s 300-715 SISE exam is the identity-and-access-control concentration in the current CCNP Security track. The live v1.2 blueprint went into effect on August 27, 2026, and it keeps the exam centered on Cisco Identity Services Engine rather than turning SISE into a broad identity-theory test. Candidates are expected to understand how ISE is deployed, how it makes authentication and authorization decisions, and how those decisions are enforced across wired, wireless, guest, BYOD, posture, and device-administration use cases.
The current revision reflects modern ISE operations. Cisco’s updated training covers ISE 3.4 and 3.5, while the blueprint adds items such as zero-touch provisioning, multifactor identity-store options, IBNS 2.0 access modes, and current policy workflows. That matters because an older study plan can still teach the fundamentals correctly yet miss the way a present-day deployment is built and operated.
SISE is therefore best approached as a policy-system exam. Memorizing menus is not enough. A strong candidate can explain what identity is being presented, which protocol carries it, which policy condition matches, what authorization result is returned, how the network device applies that result, and how ISE proves what happened afterward.
ISE turns network access into an identity-driven decision
Traditional network access often starts with a simple question: is this endpoint connected to the correct port or SSID? ISE adds a richer question: who or what is connecting, what do we know about it, and what access should it receive right now? That model connects identity stores, device context, certificates, posture, profiling, policy sets, downloadable access control lists, security group tags, VLAN assignments, and other enforcement results.
This identity-first perspective also explains why SISE belongs beside the broader 350-701 SCOR security core. SCOR supplies the surrounding security architecture; SISE goes deeper into the mechanics of admission and policy enforcement. Candidates should be able to move from a business requirement such as “managed laptops get internal access, unknown devices get restricted access†to the exact authentication, authorization, and enforcement flow that makes the requirement real.
Personas and deployment design determine scale and resilience
ISE is not a single-purpose appliance. Policy Administration, Policy Service, and Monitoring functions can be combined or separated depending on scale, resiliency, geography, and operational requirements. The v1.2 blueprint expects candidates to understand personas, deployment options, performance considerations, and zero-touch provisioning. The important skill is not memorizing a diagram; it is understanding why a design places services where it does.
A distributed deployment, for example, can keep policy decisions close to users while centralizing administration and reporting. Redundancy also has to be considered at the service level. A candidate should know what happens if a policy service node becomes unavailable, how network access devices select RADIUS servers, and why logging or administrative continuity may require a different recovery strategy than authentication continuity.
Identity stores, certificates, and MFA shape the authentication path
ISE can use Active Directory, LDAP, public key infrastructure, local identities, and multifactor authentication as parts of an access decision. The correct choice depends on the subject being authenticated and the assurance required. A user logging in with enterprise credentials presents a different problem from a certificate-authenticated managed endpoint or a headless device that cannot perform interactive authentication.
Study identity stores together with EAP behavior, certificates, certificate trust, and supplicant capabilities. TEAP and EAP chaining matter because a policy may need confidence in both the user and the managed device. Certificate validity, trust chains, identity mapping, and revocation behavior can become the difference between a clean 802.1X exchange and an authentication failure that looks like a network problem. Broader identity and access management concepts are useful here, but SISE expects you to translate them into ISE policy and RADIUS behavior.
802.1X, MAB, and IBNS 2.0 are enforcement building blocks
Wired and wireless 802.1X are core SISE skills. Candidates should understand the roles of supplicant, authenticator, and authentication server, then connect those roles to real switch and wireless-controller behavior. On wired networks, IBNS 2.0 modes such as monitor, low-impact, and closed access reflect different migration and enforcement strategies. A brownfield rollout rarely jumps from open access to maximum enforcement without an observation phase.
MAC Authentication Bypass is equally important because many printers, cameras, phones, sensors, and other devices cannot participate in 802.1X. MAB is not “secure authentication†in the same sense as a certificate-based exchange; it is a practical identity signal that must be strengthened with profiling, network location, policy conditions, and least-privilege authorization. Exam preparation should include recognizing when 802.1X is preferable, when MAB is unavoidable, and how the two methods coexist on real access ports.
Policy sets connect authentication conditions to authorization results
ISE policy becomes manageable when candidates think in stages. First identify the traffic and choose the policy set. Then determine the authentication method and identity source. After the identity is established, evaluate authorization conditions such as group membership, endpoint profile, posture state, network device type, location, or certificate attributes. The authorization profile then returns the practical result to the switch, wireless controller, VPN headend, or other network access device.
This is also where Cisco TrustSec becomes operationally relevant. Security group tags can express access intent independently of IP addressing, allowing policy to follow identity more naturally across the network. The important exam skill is to reason from policy intent to enforcement rather than treating each ISE screen as an isolated configuration task. When a result is wrong, trace the policy match, identity data, endpoint data, and authorization attributes in order.
Guest access and Web Auth require both user experience and security controls
Guest workflows combine portals, credentials, sponsors, expiration, redirection, certificates, DNS, and authorization. A working portal is not enough; the onboarding process has to send the user to the right place, establish the intended level of identity, and return the endpoint to the correct network state after authentication. Web authentication also introduces browser behavior and certificate trust into what otherwise looks like a RADIUS problem.
Practice self-registration, sponsor-approved access, hotspot-style access, and fully sponsored workflows as distinct use cases. Understand which users create accounts, how long those accounts live, and which authorization profile is applied before and after authentication. A useful troubleshooting method is to separate the redirect path, portal reachability, credential validation, and final authorization instead of treating “guest access failed†as one undifferentiated event.
Profiling improves decisions about devices that cannot identify themselves well
Profiler services collect attributes from probes and other telemetry to infer endpoint type. DHCP, RADIUS, SNMP, HTTP, DNS, and related observations can strengthen confidence that a device is a printer, IP phone, camera, workstation, or another class of endpoint. Profiling is especially valuable when MAB is used because the MAC address alone provides little assurance about what is actually connected.
The blueprint also includes Change of Authorization and endpoint identity management. CoA lets ISE change the network treatment of an endpoint after new information becomes available, such as a successful guest login or a posture transition. Study profiling as a confidence-building process rather than a magic classification engine: poor probes, incomplete telemetry, or overly broad profiling rules can produce policies that are operationally fragile.
BYOD and posture use certificates and compliance to raise assurance
BYOD onboarding is a lifecycle, not a one-time portal visit. The user authenticates, the device is enrolled, a certificate may be provisioned, the network recognizes the device on later connections, and lost or retired devices eventually need to be revoked or removed. SISE candidates should understand internal certificate authority use, certificate provisioning, wired and wireless onboarding, and the policy changes that happen as the endpoint moves through the process.
Posture adds another dimension: is an authenticated endpoint compliant with required security conditions? Client provisioning, posture conditions, policy, and the Posture Work Center all contribute to the answer. This is closely related to the modern secure-access direction represented by 300-740 SSCA, where identity, endpoint posture, and zero-trust access extend beyond the local network. The exams are different, but the operational idea is consistent: identity alone may not be sufficient when device trust matters.
Operational reporting is another reason to learn the policy flow in detail. Authentication reports can reveal repeated supplicant failures, MAB fallbacks, certificate problems, or unexpected authorization matches across many endpoints, while endpoint and posture views can expose patterns that one user ticket would never show. Use those views to distinguish an isolated client issue from a policy-design or infrastructure problem. ISE becomes more valuable when administrators use its telemetry to improve policy quality rather than only to react after access has already failed.
Certificate operations should be part of routine administration rather than an emergency task. Track expiration dates for ISE system and portal certificates, understand which services use each certificate, and test renewal procedures before a production certificate is close to expiry. Because EAP, guest portals, pxGrid-style integrations, and administrative interfaces can depend on different trust relationships, replacing a certificate without mapping its consumers can create several apparently unrelated outages at once.
Device administration and troubleshooting complete the SISE skill set
ISE is also used for network device administration through TACACS+. Candidates should know AAA roles, command authorization, accounting, and the difference between administering a network device and authenticating a user who wants network access. A strong policy can give an operations team role-appropriate command rights while creating an audit trail of what privileged users actually did.
Preparation should finish with deliberate troubleshooting. Build or simulate failures involving certificates, identity stores, RADIUS shared secrets, authorization conditions, profiling data, CoA, guest redirection, posture, and TACACS+ command sets. Then use ISE live logs and reports to identify the failing stage. The wider Cisco certifications ecosystem supplies the switching, wireless, and security background, but 300-715 rewards candidates who can make identity policy work across those technologies and explain precisely why an access decision succeeded or failed.
Cisco SISE 300-715 practice test questions and answers, training course, study guide are uploaded in ETE Files format by real users. Study and Pass 300-715 Implementing and Configuring Cisco Identity Services Engine (300-715 SISE) certification exam dumps & practice test questions and answers are to help students.
- 200-301 - Cisco Certified Network Associate (CCNA)
- 350-401 - Implementing Cisco Enterprise Network Core Technologies (ENCOR)
- 300-410 - Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- 350-701 - Implementing and Operating Cisco Security Core Technologies
- 300-415 - Implementing Cisco SD-WAN Solutions (ENSDWI)
- 300-420 - Designing Cisco Enterprise Networks (ENSLD)
- 350-601 - Implementing and Operating Cisco Data Center Core Technologies (DCCOR)
- 300-715 - Implementing and Configuring Cisco Identity Services Engine (300-715 SISE)
- 810-110 - Cisco AI Technical Practitioner (AITECH)
- 350-801 - Implementing Cisco Collaboration Core Technologies (CLCOR)
- 350-101 - Implementing and Operating Cisco Wireless Core Technologies (WLCOR)
- 350-501 - Implementing and Operating Cisco Service Provider Network Core Technologies (SPCOR)
- 350-201 - Performing Cybersecurity Using Cisco Security Technologies (CBRCOR)
- 200-901 - DevNet Associate (DEVASC)
- 500-220 - Cisco Meraki Solutions Specialist
- 400-007 - Cisco Certified Design Expert
- 200-201 - Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- 300-710 - Securing Networks with Cisco Firewalls
- 300-620 - Implementing Cisco Application Centric Infrastructure (DCACI)
- 100-150 - Cisco Certified Support Technician (CCST) Networking
- 300-730 - Implementing Secure Solutions with Virtual Private Networks (SVPN 300-730)
- 350-901 - Designing, Deploying, and Managing Network Automation Systems
- 820-605 - Cisco Customer Success Manager (CSM)
- 300-110 - Designing Cisco Wireless Networks (WLSD)
- 300-640 - Implementing Cisco Data Center AI Infrastructure (DCAI)
- 300-510 - Implementing Cisco Service Provider Advanced Routing Solutions (SPRI)
- 300-435 - Automating Cisco Enterprise Solutions (ENAUTO)
- 300-745 - Designing Cisco Security Infrastructure
- 800-150 - Supporting Cisco Devices for Field Technicians
- 300-815 - Implementing Cisco Advanced Call Control and Mobility Services (CLASSM)
- 100-140 - Cisco Certified Support Technician (CCST) IT Support
- 500-442 - Administering Cisco Contact Center Enterprise
- 300-720 - Securing Email with Cisco Email Security Appliance (300-720 SESA)
- 300-610 - Designing Cisco Data Center Infrastructure for Traditional and AI Workloads
- 300-440 - Designing and Implementing Cloud Connectivity (ENCC)
- 300-425 - Designing Cisco Enterprise Wireless Networks (300-425 ENWLSD)
- 100-160 - Cisco Certified Support Technician (CCST) Cybersecurity
- 700-805 - Cisco Renewals Manager (CRM)
- 300-515 - Implementing Cisco Service Provider VPN Services (SPVI)
- 300-220 - Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
- 300-215 - Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR)
- 300-830 - Implementing Cisco Collaboration Cloud Customer Experience (CLCCE)
- 700-750 - Cisco Small and Medium Business Engineer
- 700-246 - Cisco Environmental Sustainability Practice-Building - Stage 2 (CESPB)
- 700-242 - Cisco Environmental Sustainability Fundamentals - Stage 1 (CESF)
- 500-560 - Cisco Networking: On-Premise and Cloud Solutions (OCSE)
- 500-470 - Cisco Enterprise Networks SDA, SDWAN and ISE Exam for System Engineers (ENSDENG)
- 500-443 - Advanced Administration and Reporting of Contact Center Enterprise
- 300-445 - Designing and Implementing Enterprise Network Assurance
- 300-430 - Implementing Cisco Enterprise Wireless Networks (300-430 ENWLSI)
- 300-615 - Troubleshooting Cisco Data Center Infrastructure (DCIT)
- 300-725 - Securing the Web with Cisco Web Security Appliance (300-725 SWSA)
- 300-820 - Implementing Cisco Collaboration Cloud and Edge Solutions
- 010-151 - Supporting Cisco Data Center System Devices (DCTECH)
Purchase Cisco 300-715 Exam Training Products Individually
Why customers love us?
What do our customers say?
The resources provided for the Cisco certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the 300-715 test and passed with ease.
Studying for the Cisco certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the 300-715 exam on my first try!
I was impressed with the quality of the 300-715 preparation materials for the Cisco certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The 300-715 materials for the Cisco certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the 300-715 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my Cisco certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for 300-715. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the 300-715 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my 300-715 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my Cisco certification without these amazing tools!
The materials provided for the 300-715 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed 300-715 successfully. It was a game-changer for my career in IT!


