
- Home
- Cisco Certifications
- 300-710 Securing Networks with Cisco Firewalls Dumps
Pass Cisco SNCF 300-710 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!

300-710 Premium Bundle
- Premium File 466 Questions & Answers. Last update: Oct 01, 2026
- Training Course 51 Video Lectures
- Study Guide 588 Pages
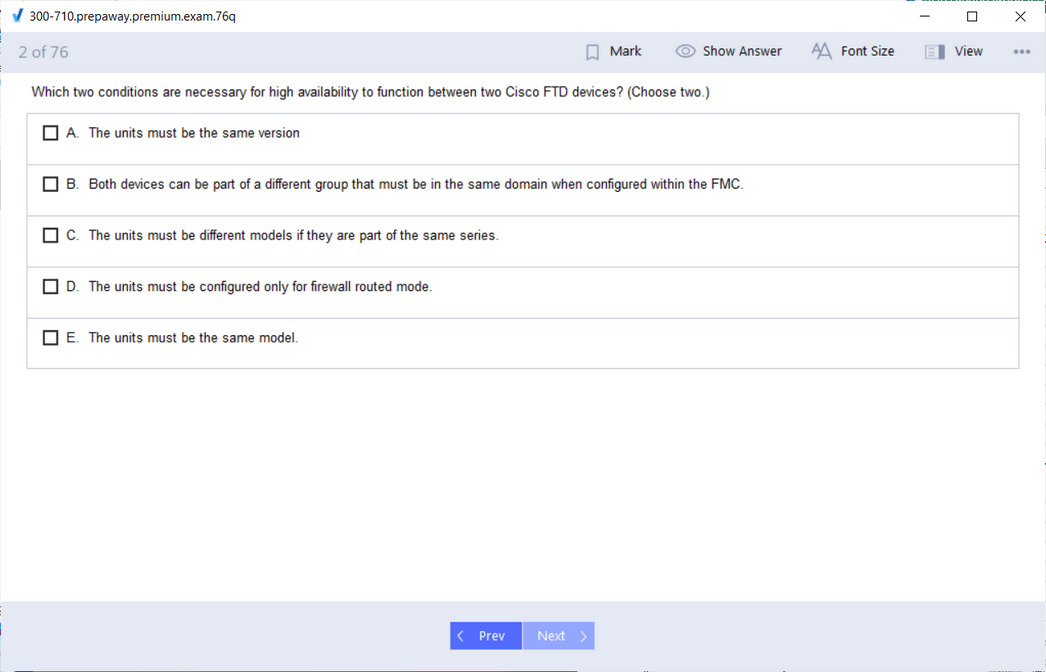
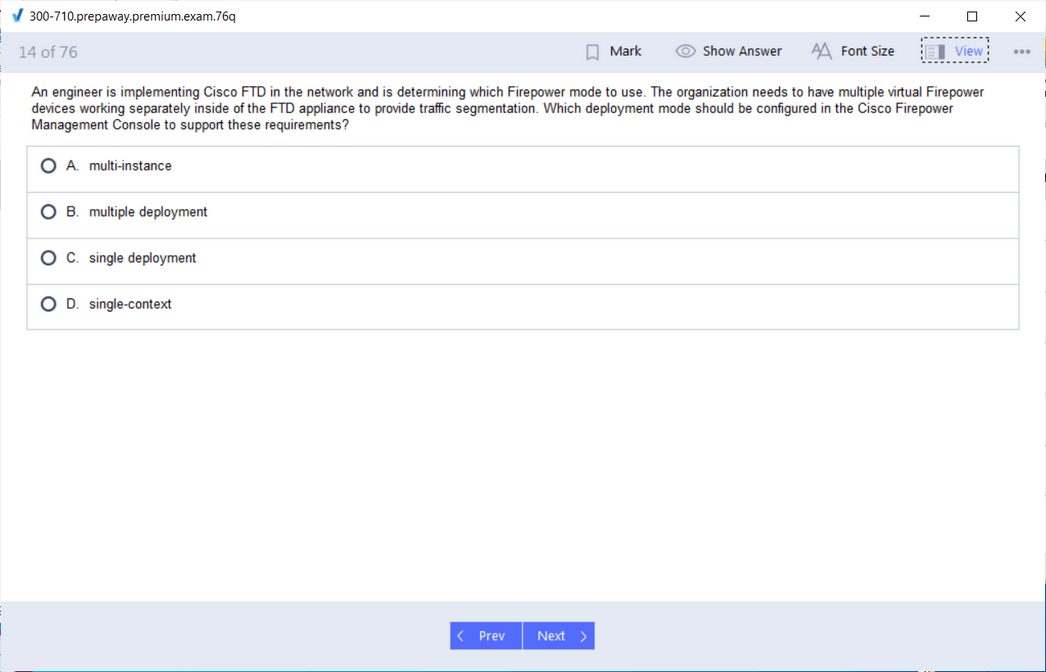
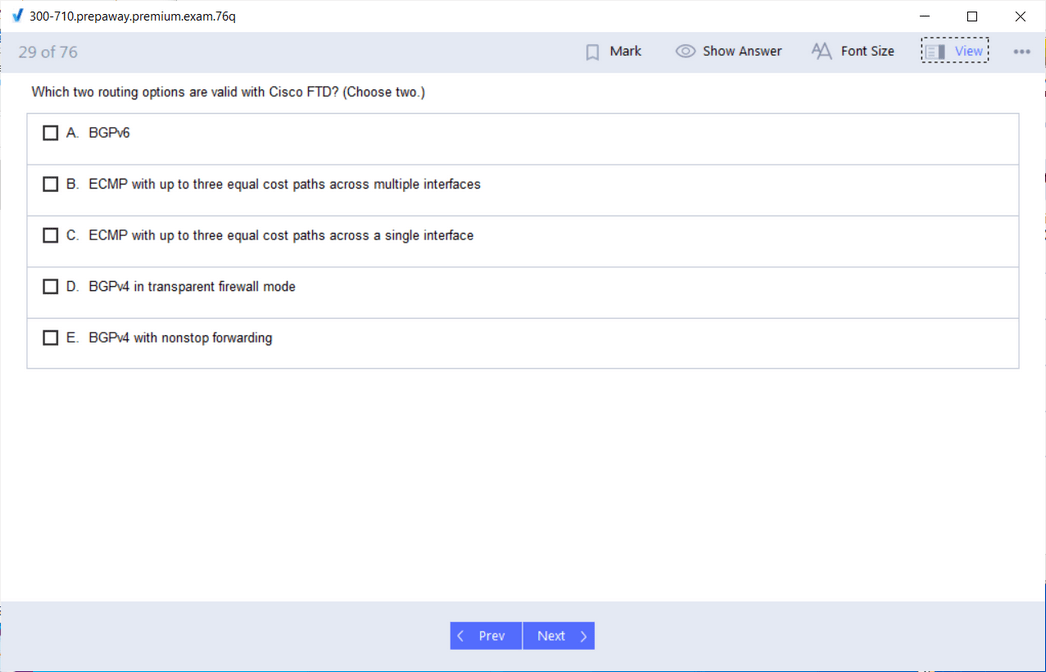
Last Week Results!
 83% students found the test questions almost same
Includes question types found on the actual exam such as drag and drop, simulation, type-in and fill-in-the-blank.
Based on real-life scenarios similar to those encountered in the exam, allowing you to learn by working with real equipment.
Developed by IT experts who have passed the exam in the past. Covers in-depth knowledge required for exam preparation.
All Cisco SNCF 300-710 certification exam dumps, study guide, training courses are Prepared by industry experts. PrepAway's ETE files povide the 300-710 Securing Networks with Cisco Firewalls practice test questions and answers & exam dumps, study guide and training courses help you study and pass hassle-free!
300-710 SNCF: Securing Networks with Cisco Firewalls
Cisco’s 300-710 SNCF exam is the firewall-focused concentration in the current CCNP Security program. The live v1.2 blueprint uses the title Securing Networks with Cisco Firewalls and tests Cisco Secure Firewall and Cisco Secure Firewall Management Center across deployment, configuration, integration, management, and troubleshooting. Older study resources may still use the Firepower name, so candidates should learn the current terminology without losing sight of the same core security functions.
SNCF is an operational exam. It is not enough to know what an access-control policy or intrusion rule is supposed to do; candidates need to understand where it is enforced, how traffic is processed, how identity or decryption changes inspection, how high availability affects deployment, and which evidence proves that a blocked or allowed connection took the expected path.
The most effective preparation uses a repeatable packet-flow model. Start with the interface and deployment mode, follow routing and NAT, determine which policy sees the traffic, account for identity, encryption, application detection, intrusion inspection, or VPN processing, and then confirm the resulting event and connection state in the management system.
Deployment mode determines how the firewall participates in the network
The current blueprint includes routed and transparent firewall modes as well as passive and inline next-generation intrusion-prevention modes. These choices change whether the appliance participates directly in Layer 3 forwarding, bridges traffic transparently, observes traffic without enforcing it, or sits inline to inspect and block. Candidates should understand the operational implications of each model.
Draw the traffic path for every deployment type. Identify which interfaces see the connection, where routing decisions occur, how management reaches the device, and what failure would do to traffic. A mode should be selected because it fits the network design and security requirement, not because one option seems more “advanced.†Troubleshooting begins by knowing what the appliance is supposed to be doing in the path.
High availability must protect traffic and state, not just hardware
Firewall resilience can involve failover, clustering, port channels, equal-cost multipath routing, and static-route tracking. The blueprint expects candidates to understand these mechanisms because security devices often sit on critical paths. A redundant chassis pair is not useful if sessions fail unnecessarily, upstream routing does not converge, or a monitored path remains black-holed.
Test failure behavior rather than only configuration. What state is synchronized? Which interfaces or routes determine health? How does traffic select a member or path? What happens to established sessions during failover? When using clustering or ECMP, consider asymmetry and inspection state. The goal is a security service that remains predictable during failure, not simply a topology with two boxes.
Secure Firewall Management Center organizes policy and operational control
Secure Firewall Management Center centralizes device management, objects, policies, events, health information, and operational workflows. Candidates should be comfortable with system settings and object management because consistent policy depends on reusable network, port, URL, application, identity, and other objects. Poor object design can make a technically valid rule base difficult to audit and maintain.
Think in terms of policy lifecycle: define objects, build the policy, deploy the change, verify the device received it, observe traffic, and confirm the intended security result. A management-plane success message is not enough if traffic behaves differently. This mindset is useful beyond the exam and aligns with the practical responsibilities described in a firewall administrator role.
Access control is the decision point for ordinary traffic
Access-control policy is central because it determines how connections are matched and what security processing follows. Rules can use source and destination, networks, zones, users, applications, URLs, and other conditions. Candidates should understand order of operations and rule specificity well enough to explain why a connection matched one rule instead of another.
When troubleshooting, begin with connection events and the actual attributes of the flow. Verify zones, addresses, ports, detected application, identity, and any object group used by the rule. Then check the action and downstream inspection. Avoid changing policy merely because traffic is blocked; first prove which rule made the decision and whether the classification itself was expected.
Intrusion, file, DNS, identity, and decryption policies add inspection depth
A next-generation firewall does more than permit or deny ports. The v1.2 blueprint includes policies and features that inspect content, identity, DNS behavior, network characteristics, encrypted traffic, and application behavior. Candidates should understand where these controls add value and what prerequisites they need. For example, identity policy cannot help if the user cannot be mapped, and encrypted traffic cannot be deeply inspected if the firewall cannot decrypt it.
Study interactions rather than separate checklists. A connection may be allowed by access policy, decrypted, associated with a user, inspected by intrusion policy, and then logged with application and file details. Any stage can change the final outcome. Build simple traffic examples and predict the sequence before checking events. This turns a large feature set into one coherent inspection pipeline.
Address translation and encrypted traffic make policy behavior more complex than a simple source-and-destination rule. Candidates should be able to reason about NAT order, original and translated addresses, and which address form is visible at each stage of connection processing. TLS decryption adds certificate trust, policy exceptions, privacy constraints, and performance cost. A decryption policy that is technically enabled but operationally inappropriate can break applications or expose the organization to compliance problems.
Intrusion prevention also requires more than selecting a policy name. Snort rules, network analysis, file controls, malware inspection, and application identification contribute different evidence and enforcement. Tuning should reduce false positives without creating broad blind spots. A good lab starts with a blocked or alerted connection, traces the event fields back to the rule or policy decision, and then tests whether a proposed exception is narrow enough to preserve the intended protection.
Network discovery and application intelligence improve policy context
Secure Firewall can learn about hosts, applications, and traffic patterns through discovery and detection features. The current blueprint includes network discovery, application detectors, correlation, and Encrypted Visibility Engine. These capabilities provide context that can improve policy decisions and help analysts understand what is operating in the environment.
Context must still be validated. An application detector can be wrong or incomplete, encrypted traffic can hide details, and discovery data can become stale. When a rule depends on application or host intelligence, confirm that the classification is accurate before changing enforcement. Security policy is strongest when its context is both rich and trustworthy.
VPNs and integrations extend the firewall beyond perimeter filtering
Secure Firewall often participates in site-to-site or remote-access VPN designs and can integrate with identity, malware, logging, orchestration, or other security systems. These integrations add value but also create dependencies. A VPN failure may be caused by routing, certificates, identity, encryption parameters, access policy, or upstream reachability rather than the tunnel configuration alone.
Trace integrated workflows end to end. For VPN, verify peer reachability, negotiation, identity or certificate state, route installation, NAT exemptions where required, and final policy. For external integrations, confirm authentication, data flow, permissions, and event timing. Additional 300-710 SNCF material can provide exam-focused context, but the live Cisco blueprint should control current feature scope.
Resiliency features can affect both traffic flow and troubleshooting. Failover, clustering, ECMP, port channels, and static route tracking change which node or path handles a connection. During an incident, operators need to know whether state replicated correctly, whether a monitored route caused path movement, and whether return traffic still follows a path compatible with the firewall state. Testing only device reachability can miss these session-level failures.
Management and lifecycle work matter as much as initial policy creation. Secure Firewall deployments rely on consistent object management, policy deployment, health monitoring, event retention, upgrades, and backups. APIs can help standardize repetitive work, but automation should verify deployment status and resulting policy state rather than assume an accepted API call means the change is active. Candidates should also practice correlating connection events, intrusion events, health alerts, packet captures, and routing information into one timeline.
Troubleshooting should follow connection processing and observable evidence
Firewall troubleshooting becomes manageable when the engineer follows the connection through the system. Confirm interface state, routing, NAT, access-control match, inspection policy, identity, decryption, VPN state, and final forwarding. Then correlate connection events, intrusion events, health alerts, packet captures, and counters. Each piece of evidence should answer a specific question.
Resist the temptation to disable security controls until traffic works. That may restore connectivity while hiding the real classification or policy problem. Instead, make the smallest testable change after identifying the failing stage. Capture before-and-after evidence and verify that the corrected rule or object applies only to the intended traffic. This method is slower than guessing for the first minute and much faster over an entire incident.
Policy cleanup is part of security engineering too. Objects and rules accumulate as applications change, mergers occur, and temporary exceptions outlive their original purpose. Candidates should be comfortable reviewing hit counts, event evidence, ownership, and dependencies before removing or consolidating policy. A smaller, well-understood rule base is easier to troubleshoot and less likely to hide an unintended permit than a large collection of stale exceptions.
Use SCOR to supply the wider security architecture around SNCF
The 350-701 SCOR core provides the broader security context for network security, cloud, content, endpoint, secure access, and automation. SNCF narrows the focus to Secure Firewall implementation and operations. Candidates who understand the role of segmentation, identity, intrusion prevention, encryption, and threat visibility in the larger architecture can make better firewall decisions than candidates who study only menus.
Build final labs around realistic policies: internet edge filtering, server protection, identity-based access, decrypted web traffic, intrusion inspection, high availability, and a VPN. For each scenario, document the expected packet path and event trail, then introduce one fault. The current Cisco certifications path rewards exactly that combination of conceptual security design and operational verification.
Cisco SNCF 300-710 practice test questions and answers, training course, study guide are uploaded in ETE Files format by real users. Study and Pass 300-710 Securing Networks with Cisco Firewalls certification exam dumps & practice test questions and answers are to help students.
Exam Comments * The most recent comment are on top
- 200-301 - Cisco Certified Network Associate (CCNA)
- 350-401 - Implementing Cisco Enterprise Network Core Technologies (ENCOR)
- 300-410 - Implementing Cisco Enterprise Advanced Routing and Services (ENARSI)
- 350-701 - Implementing and Operating Cisco Security Core Technologies
- 300-415 - Implementing Cisco SD-WAN Solutions (ENSDWI)
- 350-601 - Implementing and Operating Cisco Data Center Core Technologies (DCCOR)
- 300-420 - Designing Cisco Enterprise Networks (ENSLD)
- 810-110 - Cisco AI Technical Practitioner (AITECH)
- 300-715 - Implementing and Configuring Cisco Identity Services Engine (300-715 SISE)
- 350-801 - Implementing Cisco Collaboration Core Technologies (CLCOR)
- 350-101 - Implementing and Operating Cisco Wireless Core Technologies (WLCOR)
- 350-501 - Implementing and Operating Cisco Service Provider Network Core Technologies (SPCOR)
- 350-201 - Performing Cybersecurity Using Cisco Security Technologies (CBRCOR)
- 200-901 - DevNet Associate (DEVASC)
- 500-220 - Cisco Meraki Solutions Specialist
- 400-007 - Cisco Certified Design Expert
- 300-710 - Securing Networks with Cisco Firewalls
- 300-620 - Implementing Cisco Application Centric Infrastructure (DCACI)
- 200-201 - Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
- 100-150 - Cisco Certified Support Technician (CCST) Networking
- 300-730 - Implementing Secure Solutions with Virtual Private Networks (SVPN 300-730)
- 350-901 - Designing, Deploying, and Managing Network Automation Systems
- 820-605 - Cisco Customer Success Manager (CSM)
- 300-110 - Designing Cisco Wireless Networks (WLSD)
- 300-640 - Implementing Cisco Data Center AI Infrastructure (DCAI)
- 300-510 - Implementing Cisco Service Provider Advanced Routing Solutions (SPRI)
- 300-435 - Automating Cisco Enterprise Solutions (ENAUTO)
- 300-745 - Designing Cisco Security Infrastructure
- 800-150 - Supporting Cisco Devices for Field Technicians
- 300-815 - Implementing Cisco Advanced Call Control and Mobility Services (CLASSM)
- 300-720 - Securing Email with Cisco Email Security Appliance (300-720 SESA)
- 300-610 - Designing Cisco Data Center Infrastructure for Traditional and AI Workloads
- 500-442 - Administering Cisco Contact Center Enterprise
- 300-440 - Designing and Implementing Cloud Connectivity (ENCC)
- 300-425 - Designing Cisco Enterprise Wireless Networks (300-425 ENWLSD)
- 100-160 - Cisco Certified Support Technician (CCST) Cybersecurity
- 100-140 - Cisco Certified Support Technician (CCST) IT Support
- 700-805 - Cisco Renewals Manager (CRM)
- 300-515 - Implementing Cisco Service Provider VPN Services (SPVI)
- 300-220 - Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity
- 300-215 - Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR)
- 300-830 - Implementing Cisco Collaboration Cloud Customer Experience (CLCCE)
- 700-750 - Cisco Small and Medium Business Engineer
- 700-246 - Cisco Environmental Sustainability Practice-Building - Stage 2 (CESPB)
- 700-242 - Cisco Environmental Sustainability Fundamentals - Stage 1 (CESF)
- 500-560 - Cisco Networking: On-Premise and Cloud Solutions (OCSE)
- 500-470 - Cisco Enterprise Networks SDA, SDWAN and ISE Exam for System Engineers (ENSDENG)
- 500-443 - Advanced Administration and Reporting of Contact Center Enterprise
- 300-445 - Designing and Implementing Enterprise Network Assurance
- 300-430 - Implementing Cisco Enterprise Wireless Networks (300-430 ENWLSI)
- 300-615 - Troubleshooting Cisco Data Center Infrastructure (DCIT)
- 300-725 - Securing the Web with Cisco Web Security Appliance (300-725 SWSA)
- 300-820 - Implementing Cisco Collaboration Cloud and Edge Solutions
- 010-151 - Supporting Cisco Data Center System Devices (DCTECH)
Purchase Cisco 300-710 Exam Training Products Individually
Why customers love us?
What do our customers say?
The resources provided for the Cisco certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the 300-710 test and passed with ease.
Studying for the Cisco certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the 300-710 exam on my first try!
I was impressed with the quality of the 300-710 preparation materials for the Cisco certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The 300-710 materials for the Cisco certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the 300-710 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my Cisco certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for 300-710. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the 300-710 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my 300-710 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my Cisco certification without these amazing tools!
The materials provided for the 300-710 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed 300-710 successfully. It was a game-changer for my career in IT!


