
- Home
- Splunk Certifications
- SPLK-3001 Splunk Enterprise Security Certified Admin Dumps
Pass Splunk SPLK-3001 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!


SPLK-3001 Premium File
- Premium File 102 Questions & Answers. Last Update: Oct 23, 2026
Whats Included:
- Latest Questions
- 100% Accurate Answers
- Fast Exam Updates
Last Week Results!
 83% students found the test questions almost same
SPLK-3001: Splunk Enterprise Security Certified Admin — Legacy SIEM Administration
SPLK-3001 is associated with Splunk Enterprise Security Certified Admin. Splunk reclassified this certification as Legacy on January 1, 2026. The exam remains available, but Splunk states that legacy certification content will no longer be actively maintained for future product releases. The current certification listing shows a 60-minute exam with 48 multiple-choice questions and no formal prerequisite certification, although practical Splunk administration experience is expected.
Enterprise Security administration combines platform knowledge with security-domain configuration. Candidates need to understand event processing, normalization, technology add-ons, correlation searches, risk analysis, threat intelligence, identity and asset information, and the controls that shape analyst workflows. Legacy status does not make those concepts irrelevant; it means current deployments may contain product behavior beyond the frozen exam blueprint.
Security teams should therefore use SPLK-3001 as a bounded legacy objective while relying on current Splunk documentation for live systems. The related legacy Splunk SOAR Certified Automation Developer track covers the orchestration layer that can act on Enterprise Security findings. The broader Splunk certification program now recommends newer cybersecurity defense credentials, but Enterprise Security remains important in environments that depend on it for SIEM operations.
Normalization makes different data sources comparable
A SIEM receives authentication, endpoint, network, cloud, identity, and application telemetry with inconsistent field names and formats. Enterprise Security relies heavily on normalized fields and data models so correlation searches can reason about concepts such as user, source, destination, action, and severity across technologies. Add-ons and Common Information Model mappings are therefore part of security-content quality.
Normalization should be tested against real events rather than assumed from an add-on installation. Missing fields, incorrect sourcetypes, timestamp problems, and unexpected vendor formats can make a detection silently incomplete. The lesson in reading SIEM alerts in context begins before the alert exists: the underlying data must preserve the context the analyst will need.
Administrators should verify normalization coverage quantitatively. It is possible for a data model to exist while only a fraction of expected events populate required fields. Coverage reports, representative searches, and sampling by source can reveal blind spots before a detection rule depends on fields that are absent for part of the environment.
Correlation searches turn security hypotheses into scheduled detection logic
Correlation searches identify patterns that deserve analyst attention. Good logic defines the population, conditions, time window, grouping, and severity clearly enough that responders understand what the detection represents. Administrators need to manage scheduling, suppression, notable-event settings, and performance so detections run reliably without overwhelming the search tier.
Detection quality is more important than raw alert volume. A noisy correlation search consumes search resources and analyst time while lowering trust. SIEM tuning should use evidence such as false-positive cause, missing enrichment, threshold behavior, and entity context. Suppression should reduce known duplication without hiding genuinely new risk.
Correlation-search ownership should be explicit. A detection needs a business or security owner who can explain the threat hypothesis, data requirements, expected false positives, and response path. Without ownership, outdated searches accumulate and nobody can confidently decide whether to tune, disable, or replace them.
Risk-based approaches accumulate context instead of treating events equally
Risk analysis allows security events to contribute risk to users, systems, or other entities. Rather than firing a high-severity alert for every low-confidence signal, teams can combine evidence over time and respond when an entity’s behavior crosses a meaningful threshold. Candidates should understand risk objects, scores, modifiers, and how risk-based alerting changes investigation flow.
Risk scores are only useful when they express a defensible model. Inflating every detection creates a different form of alert noise. Teams should decide which behaviors increase concern, which assets deserve more weight, and how risk decays or is interpreted operationally. The goal is better prioritization, not a complicated number that analysts cannot explain.
Risk-based alerting benefits from entity hygiene. If the same person appears under several usernames or the same server under multiple identifiers, risk can fragment across objects and fail to reach meaningful thresholds. Identity and asset normalization therefore directly influence the quality of risk accumulation.
Assets and identities connect technical events to business importance
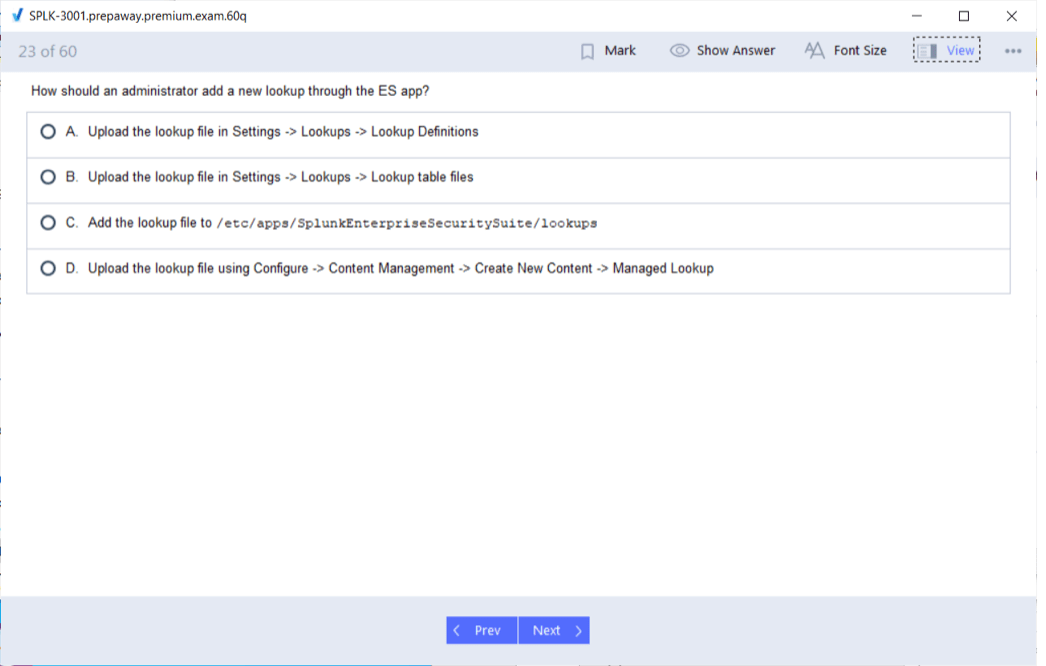
Enterprise Security can enrich events with information about systems and people. Asset criticality, category, owner, identity role, and other context help analysts distinguish a failed login on a lab account from suspicious activity involving a privileged production administrator. Administrators need to maintain the lookups or integrations that supply this context.
Stale enrichment can be worse than missing enrichment because it looks authoritative. Identity changes, decommissioned hosts, and ownership transfers need lifecycle processes. This is especially important because identity attacks leave evidence across multiple sources; enrichment is what helps those events converge on the same user or asset.
Threat-intelligence expiration rules should reflect indicator type. A malware hash may remain useful longer than a cloud IP address that changes ownership frequently. Applying one retention policy to every feed can either preserve stale noise or discard valuable evidence. Curation is part of intelligence administration.
Threat intelligence needs curation, matching, and expiry
Threat intelligence feeds can add malicious indicators such as IP addresses, domains, or hashes, but more indicators do not automatically improve security. Administrators should understand how intelligence is ingested, normalized, matched, and expired. Old or low-quality indicators can create unnecessary matches and distract analysts from higher-confidence evidence.
Context matters because an indicator match is not the same as compromise. A public resolver, shared hosting address, or recycled cloud IP can appear in intelligence without proving malicious activity in a specific event. Good workflows attach source, confidence, age, and surrounding behavior so analysts can evaluate the match.
Analyst workflow configuration should support escalation and closure quality. Status values should distinguish investigation states that change what happens next, and closure reasons should help detection engineers learn why events were false positives or benign. Workflow metadata can become feedback for content improvement rather than mere ticket bookkeeping.
Notable events and analyst workflows need operational governance
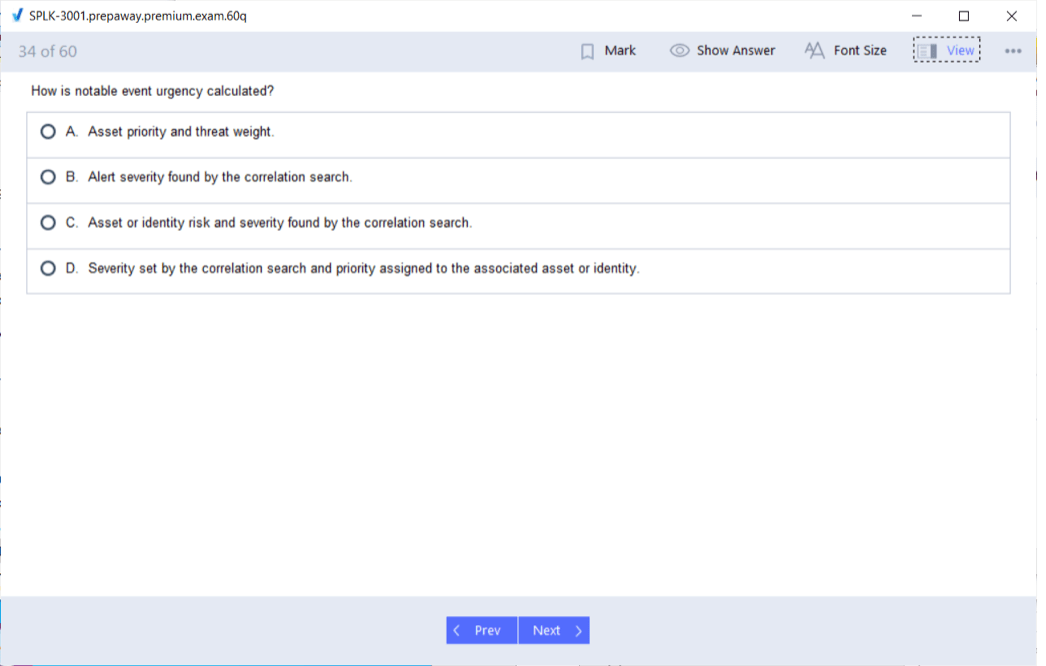
Enterprise Security presents detections through analyst-oriented interfaces and workflows. Administrators need to configure statuses, ownership, severity, investigation fields, and supporting actions so analysts can move from alert to evidence efficiently. A detection that lacks useful drilldowns or entity context forces responders to rebuild the investigation manually.
Workflow design should preserve accountability. Status changes, assignments, and investigation actions should make it possible to understand what happened and why. Reconstructing an incident timeline becomes easier when the SIEM retains both machine evidence and analyst handling context.
Enterprise Security upgrades should include content validation because app, add-on, and platform changes can affect searches or field mappings. A technically successful software upgrade is not enough if critical detections stop returning expected data. Regression tests for important security use cases reduce that risk.
Performance and content maintenance are part of SIEM administration
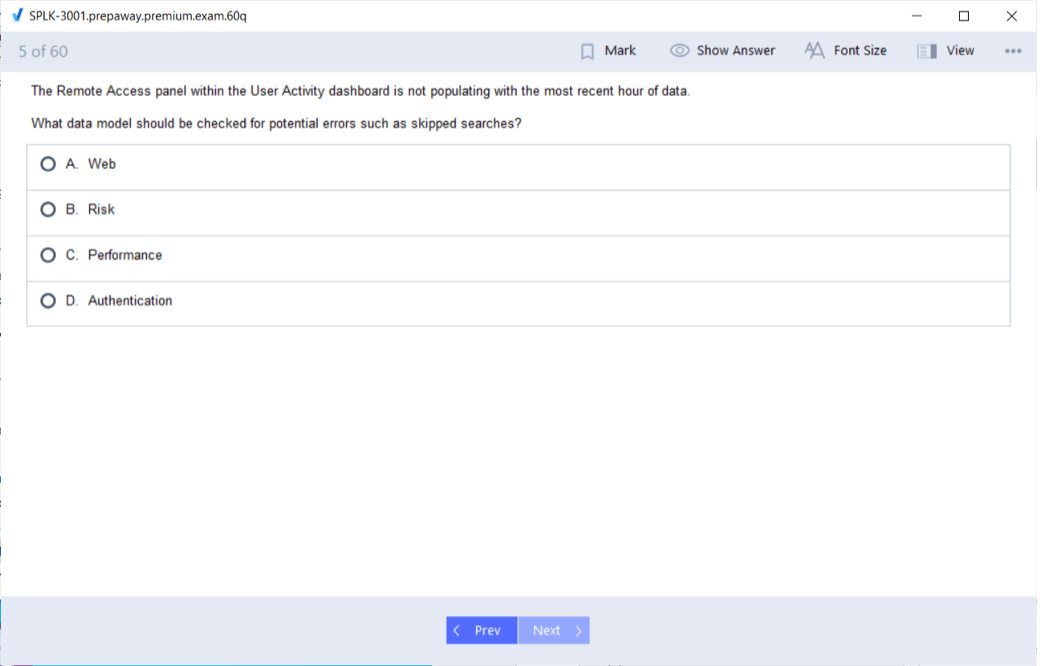
Security content can be computationally expensive because it often spans large time ranges, data models, and many sources. Administrators should monitor skipped searches, acceleration health, data-model completeness, lookup freshness, and search concurrency. Adding a detection is not complete until the team knows it can run within the required schedule.
Content also needs lifecycle management. Threat techniques evolve, products change fields, and detection assumptions become stale. Legacy certification content will not track those future changes, which makes current product documentation and local validation even more important for live environments. The frozen blueprint should never be treated as a substitute for maintaining SIEM content.
Security administrators should maintain a small set of known test events or simulations that exercise important detections. Replaying or regenerating them after configuration changes helps verify that ingestion, normalization, correlation, enrichment, and notable-event creation still work as an end-to-end chain.
Preparation should pair blueprint objectives with real detection evidence
A practical lab can ingest a few representative security sources, map fields into a normalized model, create or inspect a correlation search, tune its conditions, enrich entities, and follow the resulting notable event through investigation. Then break one assumption—remove a field mapping or age a lookup—and observe how the detection changes.
SPLK-3001 remains valuable for organizations running Enterprise Security, but candidates should understand exactly what Legacy means. Use the exam to validate established ES administration concepts, then continue learning current security capabilities and newer Splunk defense tracks. The durable skill is not memorizing menus; it is turning heterogeneous telemetry into reliable, explainable detection and investigation workflows.
A useful study method is to take one notable event and trace it backward to raw events, normalization, lookup enrichment, correlation logic, and scheduling, then forward through analyst actions and closure. That full path connects many blueprint domains and teaches where a missing field or stale lookup can change the final security outcome.
Administrative review should also include data-source health as a security control. A correlation search can appear healthy because it runs on schedule even while one required source stopped arriving. Teams should track expected source freshness and volume so detection coverage failures become visible. This matters most for high-value telemetry such as identity, endpoint, and network records whose absence can create a false sense of security.
A practical governance pattern is to maintain a detection inventory with owner, required data, purpose, severity logic, and last validation date. That inventory makes it easier to identify searches that depend on retired sources, duplicated use cases, or assumptions nobody has checked recently. It also gives security leadership a clearer picture of what the SIEM is actually expected to detect.
Why customers love us?
What do our customers say?
The resources provided for the Splunk certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the SPLK-3001 test and passed with ease.
Studying for the Splunk certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the SPLK-3001 exam on my first try!
I was impressed with the quality of the SPLK-3001 preparation materials for the Splunk certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The SPLK-3001 materials for the Splunk certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the SPLK-3001 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my Splunk certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for SPLK-3001. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the SPLK-3001 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my SPLK-3001 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my Splunk certification without these amazing tools!
The materials provided for the SPLK-3001 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed SPLK-3001 successfully. It was a game-changer for my career in IT!


