All Splunk SPLK-1002 certification exam dumps, study guide, training courses are Prepared by industry experts. PrepAway's ETE files povide the SPLK-1002 Splunk Core Certified Power User practice test questions and answers & exam dumps, study guide and training courses help you study and pass hassle-free!
SPLK-1002: Splunk Core Certified Power User Search and Knowledge Skills
SPLK-1002 is the current exam code for Splunk Core Certified Power User. Splunk describes the certification as an entry-level credential for users who want stronger searching and reporting capability plus practical competence with workflow actions, event types, knowledge objects, data models, field aliases, calculated fields, macros, and data normalization. The current exam is 65 multiple-choice questions in 60 minutes, has no formal prerequisites, costs US$130 per attempt, and is delivered through Pearson VUE.
Power User sits above basic navigation and search. The candidate is expected to shape data into reusable analytical knowledge so other users can answer questions consistently. That means understanding not only how to write a one-time query, but how to create fields, event classifications, macros, lookups, models, and visualizations that improve repeated analysis.
The strongest prerequisite is genuine comfort with the skills validated by Splunk Core Certified User. Power User preparation moves faster when time ranges, fields, basic searches, reports, dashboards, and alerts already feel natural. The broader Splunk certifications family then provides several paths into administration, advanced analysis, observability, and security.
Transforming commands turn event streams into analytical tables
Commands such as chart, timechart, stats, and related transforming operations change raw event results into summarized datasets. Candidates need to understand how grouping fields, aggregation functions, time bins, and chart dimensions affect the shape of the result. A command can run successfully while still answering the wrong question if the grouping logic is wrong.
Timechart is especially important because operational data is frequently interpreted as a trend. Users should understand what is being counted or calculated in each interval, what happens when series are split by another field, and how time range influences the conclusion. A short spike can disappear in a large bucket, while overly fine resolution can create noise.
Visualization should come after the analytical question. The candidate should be able to explain why a time series, category comparison, table, or single value is the appropriate representation rather than choosing a chart because it looks impressive.
eval, where, and filtering commands create analytical logic
The eval command creates or transforms fields using expressions and functions. It can calculate durations, normalize categories, conditionally label events, combine strings, or convert units. Power users should understand that calculated fields are not just presentation tricks; they can make repeated business logic explicit and reusable.
Filtering with search and where requires attention to syntax and data type. Numeric comparisons, string matching, null behavior, and boolean logic can produce very different results from superficially similar expressions. Candidates should test assumptions with small result sets and inspect fields before relying on a complex condition.
A good search is auditable. Another analyst should be able to read the pipeline and understand how the result was derived. Clever expressions that save a few characters but hide intent can make operational troubleshooting harder.
Correlation is about relationships across events, fields, and time
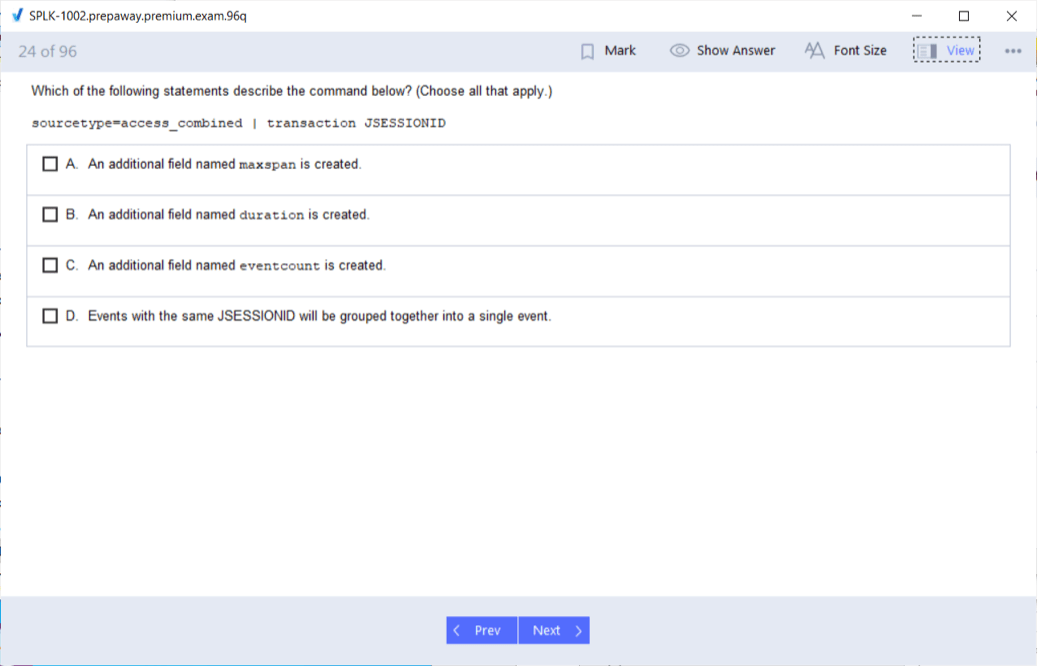
Power users often need to group events that belong to the same activity even when the data arrives as separate records. The transaction command can correlate events by fields and time constraints, while stats-based approaches may provide more efficient alternatives depending on the question. Candidates should understand the concept rather than assuming one correlation command fits every case.
Correlation needs a stable key or defensible relationship. User ID, session ID, request ID, source and destination, or another field may define what belongs together. If the key is missing or reused, results can blend unrelated events. Time constraints help, but they do not repair bad identifiers.
This is directly relevant to investigations. Incident timelines depend on connecting evidence from multiple events in a reliable order. Splunk can support that reconstruction only when analysts understand the fields and clocks behind the data.
Knowledge objects make analytical logic reusable
Event types, tags, aliases, calculated fields, lookups, and macros reduce repetition and give shared meaning to data. An event type can classify a useful search pattern; a tag can group related field values; an alias can normalize naming; a calculated field can encode derived logic; and a macro can package repeated search syntax.
Reuse creates governance responsibilities. If a macro changes, many saved searches may change behavior. If an alias hides the original field meaning, users can misinterpret data. Knowledge objects need clear names, ownership, permissions, and enough documentation that users understand what they represent.
The goal is semantic consistency. Different data sources may describe the same concept with different field names or values. A disciplined knowledge layer helps analysts ask one question across those sources without rewriting every search from scratch.
Permissions are part of that governance. A useful macro or calculated field may need to be shared across an app, while experimental logic may belong in a private scope until it is stable. Power users should understand that making knowledge objects reusable also makes their naming, ownership, and access choices consequential.
Field extraction and aliases require precision about when fields exist
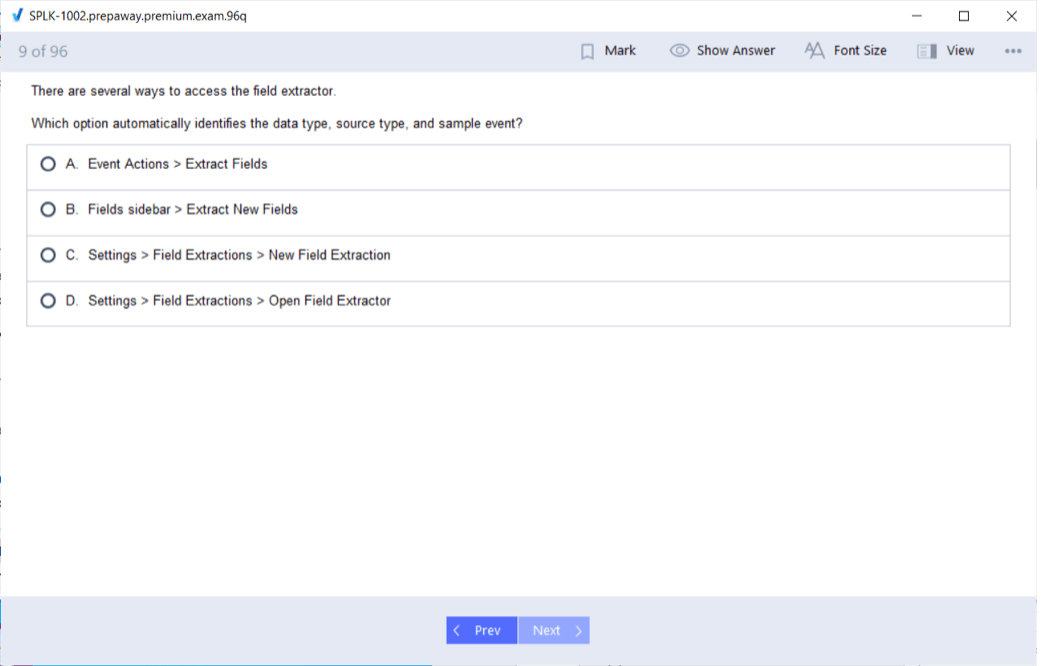
Splunk can extract fields from structured or unstructured events, and power users need to understand how search-time fields become available for later commands. Regular expressions can be powerful, but a fragile extraction can silently break when log formats change. Candidates should validate extractions against varied samples rather than one ideal event.
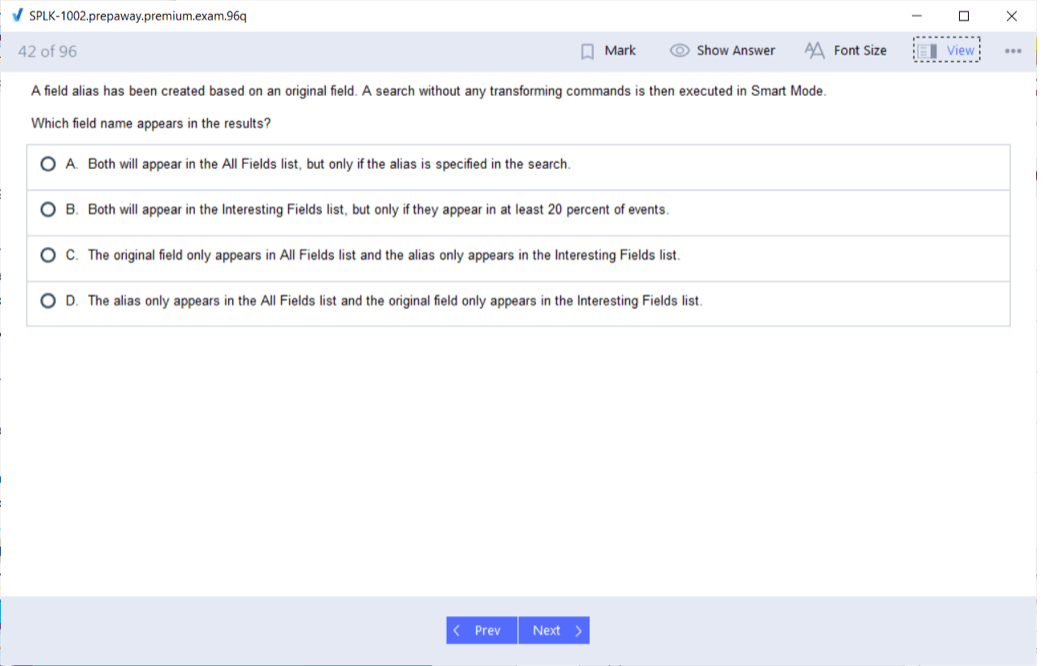
Field aliases are useful when one dataset uses a different name for the same semantic concept. The original field remains available while the alias exposes a normalized name. This supports common searches without forcing every source to be rewritten at ingestion.
Calculated fields add another layer by deriving new values. The important design question is whether the calculation belongs in a shared knowledge object, a specific report, or a one-off investigation. Reuse is valuable when the logic is stable and broadly understood.
Data models support structured analysis and normalization
Data models organize datasets and fields so users can work with a consistent analytical structure. They become especially valuable when many sources need to support the same kinds of questions. Candidates should understand the relationship between root datasets, child datasets, constraints, fields, and how the model can support Pivot or accelerated analysis where appropriate.
Normalization reduces the cost of heterogeneity. Security and operations data frequently arrive with different names for user, source, destination, action, or severity. Common field conventions allow dashboards and searches to work across sources rather than being rebuilt for every technology.
The concept is similar to any governed data model: shared definitions create leverage, but only if the definitions remain accurate. When a source changes, model owners need to verify that mappings and constraints still represent reality.
Workflow actions connect search results to an operational next step
A search result often identifies an entity that needs further investigation: a host, IP address, user, ticket, or external record. Workflow actions can turn field values into links or requests that open another system or perform a defined action. They reduce manual copy-and-paste and keep investigation context attached to the result.
Power users should understand that convenience must be controlled. An action that sends data externally or triggers a change should respect permissions, encoding, validation, and security. A poorly designed workflow action can expose sensitive values or encourage users to execute an action without sufficient context.
The best workflow action shortens a legitimate investigative path. It should make the next step clearer, not simply add another clickable element to a dashboard.
Power User skills improve both security and operations investigations
Advanced search, field normalization, event types, and data models are especially useful when analysts investigate noisy operational data. A security team might use them to classify authentication events and normalize identities; an operations team might correlate service errors with hosts and deployments; a business team might standardize transaction categories.
The habit described in question-driven threat hunting is a useful model even outside security. Start with a testable question, identify the required fields and time range, build the smallest search that answers it, then add context. Dashboards and reusable knowledge should emerge from repeated useful questions rather than replace them.
Similarly, SIEM alert context depends on normalized fields and reliable enrichment. Splunk Power User skills provide the mechanisms that make that context searchable and repeatable.
Preparation should build reusable searches, not memorize isolated commands
Splunk’s current blueprint remains the best checklist. For each objective, create a small dataset or use training data, perform the task, and explain the result. Build a timechart, use eval and where, correlate events, create an event type, tag a value, define a macro, add a lookup, create a field alias, and work with a data model. Then change the data and see whether the solution still behaves correctly.
Candidates should also practice reading unfamiliar searches. Certification questions may test whether a pipeline produces the intended grouping or transformation, and real work frequently begins with somebody else’s saved search. Trace the pipeline left to right, inspect intermediate results, and identify where a field is created or filtered.
SPLK-1002 validates the transition from basic Splunk user to reusable analytical practitioner. The strongest Power User does not merely know more commands; that person can turn raw events into consistent, understandable, governed analytical knowledge that other people can trust.
Splunk SPLK-1002 practice test questions and answers, training course, study guide are uploaded in ETE Files format by real users. Study and Pass SPLK-1002 Splunk Core Certified Power User certification exam dumps & practice test questions and answers are to help students.


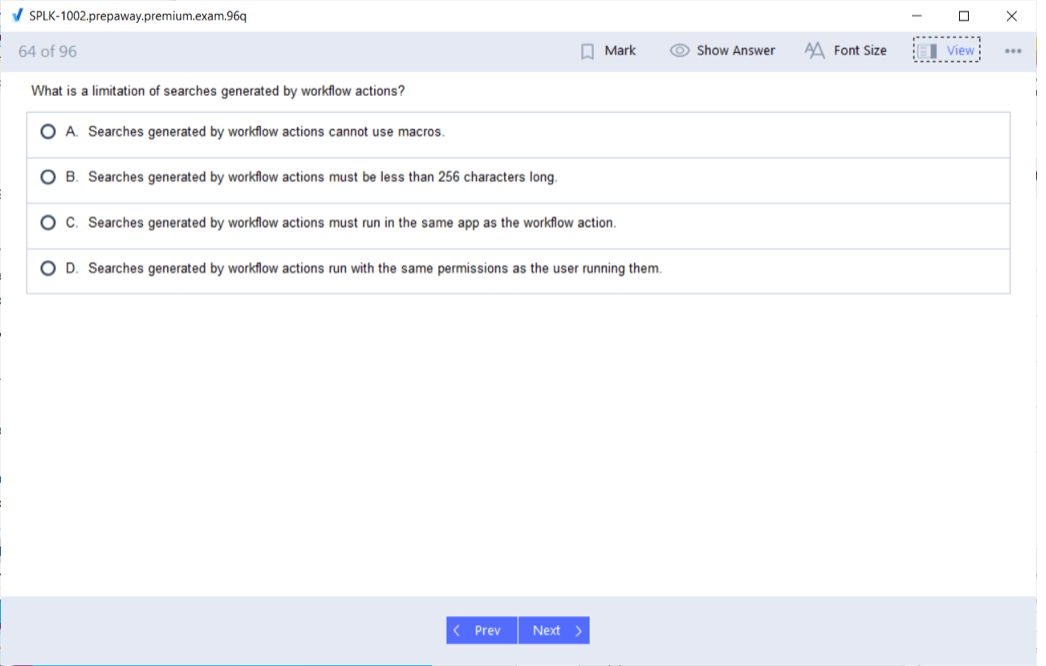
 83% students found the test questions almost same



However, you should not try to memorize the practice questions and expect to pass the exam. It is plain stupidity. Question are there only for you to get an idea about the exam and check your level of competence so that you can know beforehand if you have a good chance of passing. So while doing questions you also have to study hard. That's the best way to pass the exam. Good luck!!!!!
-regards