All IIA IIA-CIA-Part2 certification exam dumps, study guide, training courses are Prepared by industry experts. PrepAway's ETE files povide the IIA-CIA-Part2 Certified Internal Auditor - Part 2, Practice of Internal Auditing practice test questions and answers & exam dumps, study guide and training courses help you study and pass hassle-free!
CIA Part 2 (2019): Practice of Internal Auditing
CIA Part 2 under the 2019 syllabus is titled Practice of Internal Auditing. It reflects the version of the Certified Internal Auditor exam that organized engagement work across four domains: managing the internal audit activity, planning the engagement, performing the engagement, and communicating results while monitoring progress. The content remains useful for understanding the older program and for limited language transitions, but new candidates should first confirm which syllabus their scheduled exam uses.
The 2019 Part 2 format is 100 multiple-choice questions in 120 minutes. Its weighting places 20 percent on managing the activity, 20 percent on engagement planning, 40 percent on performing the engagement, and 20 percent on communication and follow-up. The 2025 redesign moved management-of-the-function topics largely into Part 3 and concentrated current Part 2 on the engagement lifecycle.
For current preparation, CIA Part 2: Internal Audit Engagement is the more relevant destination. Candidates reviewing how the three-part program fits together can also use the IIA certifications family as context. The important editorial distinction is that an older exam can still teach sound audit practice without being the current blueprint.
Managing the internal audit activity was a full domain in the 2019 Part 2
The first domain asks how an internal audit activity is planned, organized, staffed, directed, and monitored. That includes policies and procedures, budgeting, resource decisions, performance indicators, coordination, and communication with senior management and the board. Candidates need to recognize that the chief audit executive manages a function, not just a queue of individual engagements. Coverage choices should reflect organizational objectives and risk, available competencies, and the assurance responsibilities expected from internal audit.
Administrative efficiency is not the same as audit effectiveness. A function can finish every engagement on schedule and still fail if it avoids major risks or produces conclusions that do not help governance. The exam can therefore present metrics that look positive but measure activity rather than value. Good management balances coverage, quality, timeliness, staff development, stakeholder expectations, and the need to preserve independence.
A risk-based audit plan connects limited resources to the organization’s priorities
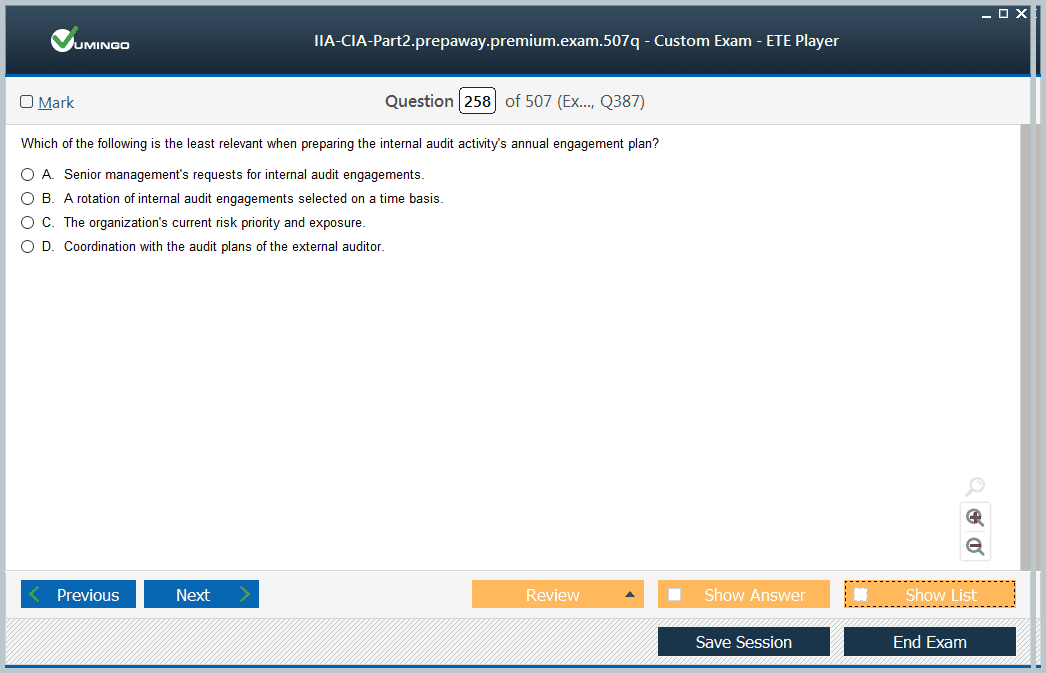
The 2019 syllabus expects candidates to understand how the CAE develops a risk-based plan and communicates it for approval. The plan should be informed by the organization’s strategies, objectives, significant risks, changes, previous assurance work, and management or board concerns. It is not simply last year’s schedule moved forward by twelve months. New acquisitions, technology, regulation, business models, incidents, or emerging risks can all justify changes in coverage.
Resource constraints must be communicated rather than hidden. If the internal audit activity lacks the skills or capacity to cover a material risk, the board should understand the consequence. That may lead to reprioritization, co-sourcing, specialized support, or a conscious acceptance of less assurance. This is one place where risk-management principles help candidates reason about likelihood, impact, treatment, monitoring, and changing context.
Engagement planning turns broad risk into testable objectives
Planning starts by understanding why the engagement matters. Auditors identify objectives, scope, criteria, stakeholders, relevant processes, and significant risks and controls. A strong engagement objective is specific enough to guide work and broad enough to address the reason the engagement was included in the plan. Copying a standard work program without understanding the process can cause teams to test controls that no longer address the organization’s actual exposure.
The preliminary risk assessment determines where detailed work should concentrate. Interviews, process walkthroughs, prior reports, policies, data, performance measures, and external requirements can all help the team build a model of the area. Scope decisions should then follow the risk assessment. A scenario that reveals a major unaddressed risk may justify revising the planned scope rather than continuing mechanically with the original checklist.
Work programs should translate audit objectives into evidence needs
An engagement work program sets out the procedures required to achieve the objectives. The important reasoning chain is objective to risk to control to procedure to evidence. If one link is missing, the procedure may generate data without supporting a conclusion. Candidates should be able to identify whether inquiry, observation, inspection, reperformance, confirmation, analytical procedures, or data analysis is appropriate for the assertion being tested.
Sampling also belongs inside this evidence design. A sample should reflect the purpose of the test, the population, expected error, tolerable error, and the level of assurance sought. Statistical and nonstatistical approaches can both be legitimate, but neither excuses poor population definition. Selecting convenient transactions or ignoring excluded records can bias the result even when the arithmetic looks sophisticated.
Evidence must be sufficient, reliable, relevant, and useful
The performing-engagement domain carries 40 percent of the 2019 exam because conclusions depend on evidence quality. Sufficiency concerns quantity, while reliability and relevance concern the strength and connection of the evidence to the engagement objective. Directly observed or independently confirmed information can be stronger than unsupported explanation, but context matters. A candidate should ask what the evidence actually proves rather than treating any document as conclusive.
Contradictory evidence deserves attention. If interviews describe a control that system logs do not show, the auditor should not simply select the source that supports the expected answer. Further work may be required to understand exceptions, timing, data quality, or control design. This disciplined reconciliation is one of the clearest differences between audit judgment and checklist completion.
Analysis converts raw findings into defensible observations
A strong audit observation normally connects condition, criteria, cause, effect or risk, and an appropriate recommendation or agreed action. The labels can vary, but the logic matters. A fact without criteria may not establish a deficiency; criteria without evidence may be theoretical; and a recommendation that ignores the root cause can create work without reducing risk. Candidates should learn to diagnose why the condition occurred before proposing a response.
Data analytics and computer-assisted techniques can extend coverage, identify anomalies, or test entire populations, but they do not eliminate judgment. A query can reveal duplicate payments, unusual access patterns, or outliers; the auditor still needs to determine whether the pattern represents error, fraud, expected business behavior, or a data-quality problem. Analytical power is most useful when it is connected to a clear audit question.
Supervision protects quality while developing the audit team
Engagement supervision ensures that objectives are achieved, work is properly documented, evidence supports conclusions, and less experienced staff receive guidance. Review should occur throughout the engagement rather than only after fieldwork ends. Early review can identify an ineffective procedure or a misunderstood risk before the team spends days collecting evidence that will not support the final conclusion.
Supervision also includes resolving review notes and documenting significant professional judgments. The reviewer should be able to understand what was tested, what evidence was obtained, what exceptions were found, and why the team reached its conclusion. This is a quality function, but it is also a learning mechanism: good review improves how auditors frame risks, design procedures, and communicate issues on future work.
Communication should be clear about significance, not just technically correct
The 2019 syllabus tests the quality of engagement communications: accurate, objective, clear, concise, constructive, complete, and timely. Good reporting explains why the issue matters and what risk remains, not merely what policy was violated. An overly technical finding can be correct yet ineffective if decision-makers cannot see the consequence or the action needed.
Preliminary discussions give management a chance to clarify facts and provide additional evidence, but they do not transfer ownership of the audit conclusion. Disagreement should be resolved through evidence and criteria. The final communication should reflect the engagement objectives and scope and should distinguish observations, conclusions, recommendations, management responses, and unresolved risk appropriately. The broader quality-auditor responsibilities discussion is useful where audit evidence, findings, and corrective action overlap.
Follow-up asks whether agreed action actually changed the risk
Monitoring progress is more than checking whether a due date passed. Internal audit needs a process for determining whether management implemented agreed actions or otherwise addressed the underlying risk. A closed ticket is not persuasive if the root cause persists. The depth of validation should reflect the significance of the issue and the nature of the action.
If management accepts a level of residual risk that the CAE believes may be unacceptable to the organization, escalation becomes a governance matter. The auditor should first discuss the issue with senior management and, if unresolved, communicate it to the board as required by the professional framework. This preserves management’s right to make risk decisions while ensuring that significant risk acceptance is visible to those responsible for oversight.
Documentation supports this chain of reasoning. Workpapers should allow an experienced reviewer to understand the engagement objective, procedures performed, evidence obtained, exceptions identified, and basis for the conclusion. More documentation is not automatically better; the record must be relevant and sufficient to demonstrate the work. Candidates should be wary of options that treat documentation as an administrative task to complete after the conclusion has already been decided.
Treat the 2019 map as historical architecture, not the current study blueprint
Many principles in the older Part 2 remain central to internal audit: risk-based planning, good evidence, documentation, supervision, communication, and follow-up. What changed in 2025 is the way those principles are distributed across the three CIA parts and aligned to the Global Internal Audit Standards. Current candidates should therefore avoid studying by old domain percentages even when the underlying explanation remains professionally sound.
The older syllabus also emphasizes coordination with other assurance providers. Internal audit may rely on or coordinate with compliance, risk, external audit, quality, security, or specialist functions when doing so improves coverage and avoids duplication. Before relying on another provider, the CAE considers competence, objectivity, scope, and quality of work. Coordination is therefore a governance decision about assurance coverage, not simply a way to reduce internal audit effort.
A practical transition check is to compare every resource with the syllabus tied to the candidate’s exam language and date. If the material speaks heavily about “Managing the Internal Audit Activity” as a Part 2 domain, it is describing the 2019 structure. Use it for durable engagement concepts, then reorganize the study plan around the current Part 2 blueprint before test day.
IIA IIA-CIA-Part2 practice test questions and answers, training course, study guide are uploaded in ETE Files format by real users. Study and Pass IIA-CIA-Part2 Certified Internal Auditor - Part 2, Practice of Internal Auditing certification exam dumps & practice test questions and answers are to help students.


 83% students found the test questions almost same