
- Home
- IIA Certifications
- IIA-CIA-Part1 CIA Part 1 - Essentials of Internal Auditing Dumps
Pass IIA IIA-CIA-Part1 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!

IIA-CIA-Part1 Premium Bundle
- Premium File 1175 Questions & Answers. Last update: Oct 23, 2026
- Training Course 10 Video Lectures
- Study Guide 372 Pages
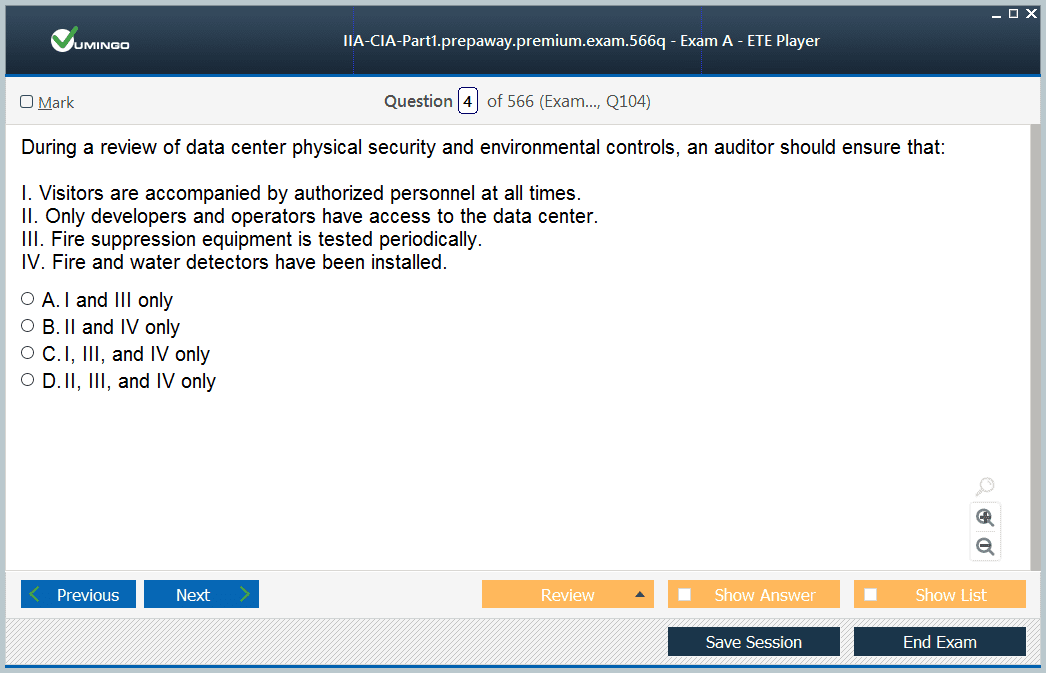
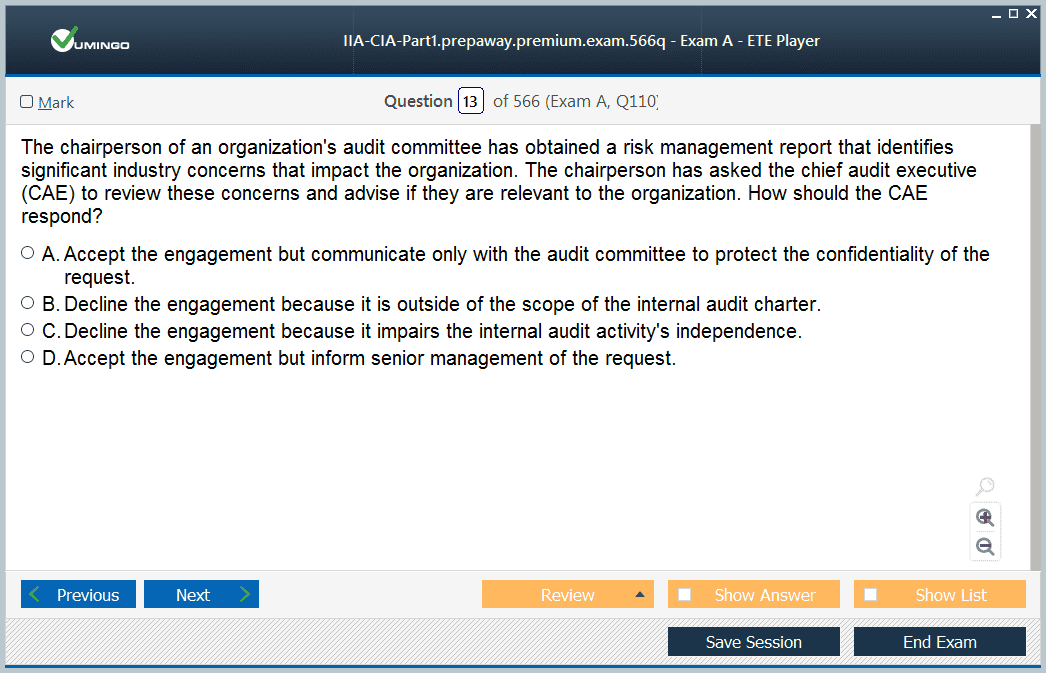
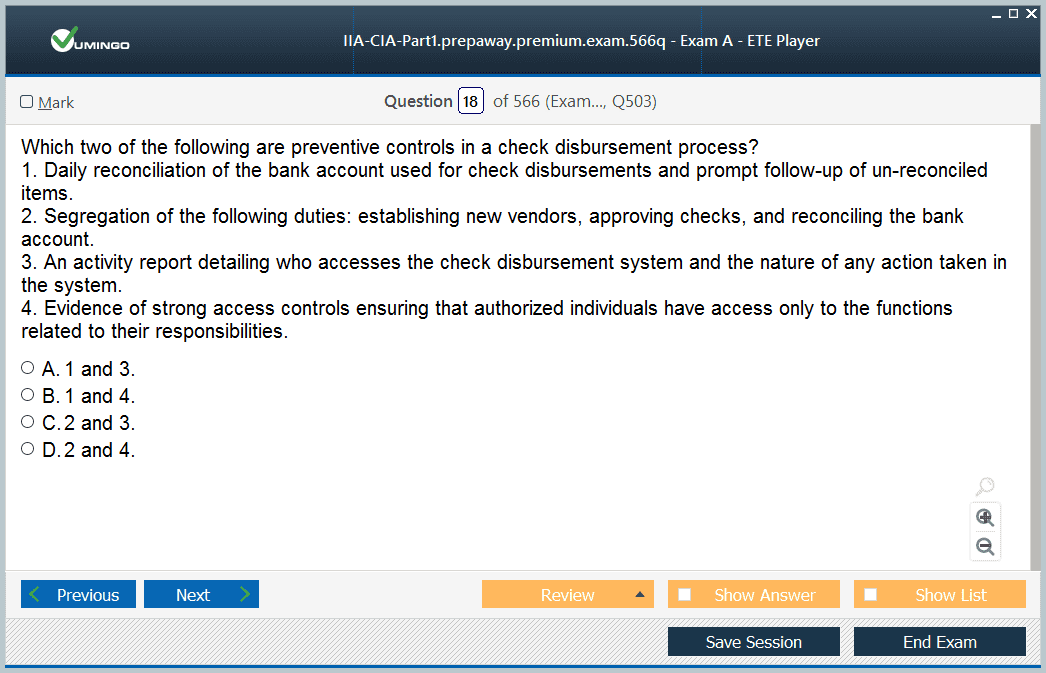
Last Week Results!
 83% students found the test questions almost same

Includes question types found on the actual exam such as drag and drop, simulation, type-in and fill-in-the-blank.
Based on real-life scenarios similar to those encountered in the exam, allowing you to learn by working with real equipment.
Developed by IT experts who have passed the exam in the past. Covers in-depth knowledge required for exam preparation.
All IIA IIA-CIA-Part1 certification exam dumps, study guide, training courses are Prepared by industry experts. PrepAway's ETE files povide the IIA-CIA-Part1 CIA Part 1 - Essentials of Internal Auditing practice test questions and answers & exam dumps, study guide and training courses help you study and pass hassle-free!
CIA Part 1 (2019): Essentials of Internal Auditing
The IIA CIA Part 1 page represents the 2019 Certified Internal Auditor syllabus for Essentials of Internal Auditing. It remains useful for candidates working with older study plans, historical course material, or one of the limited language versions that had not yet completed the 2025 transition by October 2026. It should not, however, be treated as the default syllabus for a new English-language candidate. The revised English CIA exams launched on May 28, 2025 and reorganized Part 1 around the Global Internal Audit Standards.
Under the 2019 structure, Part 1 contains 125 multiple-choice questions and allows 150 minutes. Its six domains are Foundations of Internal Auditing, Independence and Objectivity, Proficiency and Due Professional Care, Quality Assurance and Improvement Program, Governance/Risk Management/Control, and Fraud Risks. The exam format remained stable through the syllabus transition, but the topic organization and standards context changed substantially.
Candidates beginning a current preparation plan should orient themselves to CIA Part 1: Internal Audit Fundamentals. The broader IIA certifications context is also useful when deciding whether the CIA, IAP, CRMA, or a challenge pathway matches the professional goal. This page therefore explains the older Part 1 accurately while making the transition boundary explicit.
The 2019 syllabus begins with the purpose and authority of internal audit
The first domain asks candidates to understand what internal audit is authorized to do and why the function exists. That requires more than memorizing a definition. An internal audit activity needs a recognized purpose, a charter, access to information and people, and a reporting position that allows it to evaluate significant risks without being directed away from uncomfortable areas. In practical questions, the issue is often whether the function has enough authority to perform objective work rather than whether a policy document contains the correct phrase.
The 2019 framework also distinguishes assurance from consulting services. Assurance involves an objective assessment of evidence against criteria, while consulting can include advice, facilitation, training, and other agreed support. The boundary matters because management still owns decisions, risks, and controls. An auditor can advise on a proposed process, but taking responsibility for operating that process can create later objectivity problems when the same area is audited.
Independence is organizational while objectivity is personal
The second domain separates two ideas that candidates frequently blur. Organizational independence concerns the internal audit activity’s status, reporting relationships, access, and freedom from interference. Objectivity concerns an individual auditor’s ability to make impartial judgments. A strong reporting line to the board may protect the function, yet a particular auditor can still have a conflict because of a recent operational role, financial interest, family relationship, or other bias.
Exam scenarios often test the response to an impairment rather than the definition alone. Disclosure, reassignment, additional supervision, or another safeguard may be required depending on the circumstances. The goal is not to avoid all interaction with management. Internal auditors need relationships and business understanding to work effectively. The professional skill lies in remaining collaborative without allowing familiarity, incentives, or pressure to distort conclusions.
Proficiency and due professional care set the standard for competent work
The 2019 Part 1 gives 18 percent of its weight to proficiency and due professional care. Proficiency refers to the knowledge, skills, and competencies needed to carry out responsibilities. The internal audit activity does not need every specialty in one person, but it must obtain suitable expertise when the scope requires it. Cybersecurity, taxation, actuarial work, complex valuation, engineering, or legal interpretation can all create situations where specialized assistance is more responsible than pretending a generalist can resolve every issue.
Due professional care is a reasonableness standard, not a promise of perfection. Auditors consider the significance of the matter, probability of error or fraud, complexity, cost of assurance, and potential benefit of additional procedures. A common exam trap is to assume that professional care requires exhaustive testing. In reality, good audit work is risk-based: the auditor designs enough work to support a sound conclusion while recognizing the limits of time, evidence, and engagement objectives.
Quality assurance evaluates the function, not only the final report
The Quality Assurance and Improvement Program domain covers how the internal audit activity evaluates conformance, performance, and opportunities to improve. Quality begins with policies, supervision, engagement practices, competency, and monitoring; it does not begin at the proofreading stage. Internal assessments and periodic external assessments provide different forms of evidence about whether the activity is operating as intended and conforming with the applicable professional framework.
Candidates should connect quality to the chief audit executive and the board. The CAE is responsible for establishing and maintaining the program, while the board needs meaningful information about the activity’s quality and independence. A useful measure is tied to outcomes and risk coverage, not merely the number of audits completed. High output can coexist with weak assurance if scopes are superficial, evidence is poor, or important risks are repeatedly avoided.
Governance, risk management, and control dominate the older Part 1
At 35 percent, governance, risk management, and control form the largest domain in the 2019 syllabus. Governance determines how objectives are set, responsibilities are allocated, conduct is overseen, and accountability is exercised. Risk management identifies uncertainty around objectives and selects responses. Controls translate those responses into actions, checks, approvals, system rules, reconciliations, monitoring, and other mechanisms that keep exposure within acceptable limits.
The relationship among these elements is more important than any one framework. A candidate should be able to recognize when governance is weak because accountability is unclear, when risk management is weak because it is disconnected from objectives, or when controls are weak because they address symptoms rather than the underlying risk. Broader governance, risk, and compliance thinking helps connect the components without turning them into separate checklists.
Risk assessment should begin with objectives and context
A risk statement only becomes useful when it explains uncertainty in relation to an objective. Internal auditors therefore need to understand the organization’s strategy, processes, stakeholders, risk appetite, and external environment before judging whether a response is adequate. The same event can be insignificant in one business unit and critical in another because impact, likelihood, regulatory exposure, and tolerance are different.
Frameworks can provide structure, but the exam expects judgment rather than brand recognition. Risk-management principles are useful for thinking about context, identification, analysis, treatment, communication, and monitoring. The auditor’s role is to evaluate whether the organization’s approach is appropriate and functioning, not to assume that one named methodology automatically produces effective risk management.
Control design and operating effectiveness answer different questions
Control evaluation requires candidates to distinguish design from operation. A control is well designed when, if performed as intended, it would reasonably reduce the relevant risk. It is operating effectively when the right people or systems actually perform it consistently and exceptions are handled appropriately. Testing one dimension does not prove the other. A flawless approval log cannot rescue a control that approves the wrong thing, and an excellent design provides little protection if it is routinely bypassed.
Controls can be preventive, detective, corrective, directive, or compensating, and they can be manual or automated. Candidates should focus on the control objective and the risk addressed rather than memorizing labels in isolation. Culture, incentives, segregation of duties, information quality, and management override can also determine whether a control environment works. Transaction-level procedures operate inside that larger organizational context.
Fraud risk calls for skepticism, role clarity, and disciplined escalation
The fraud domain asks internal auditors to understand fraud risks, common indicators, prevention and detection controls, and the audit function’s responsibilities. Management remains responsible for establishing controls to prevent and detect misconduct. Internal audit evaluates whether fraud risk is recognized and managed, remains alert to red flags, and expands work when evidence suggests that the original explanation may be incomplete.
Professional skepticism is not the same as assuming guilt. It means questioning unusual patterns, inconsistent evidence, unexplained overrides, conflicts of interest, or transactions that do not fit the business rationale. When suspicion becomes significant, preserving evidence and following established escalation and investigation protocols are often more appropriate than confronting an individual directly. The exam rewards role-aware judgment rather than dramatic action.
One subtle point in the older blueprint is that the International Professional Practices Framework in force at the time used the former Standards structure and Code of Ethics. A candidate reviewing a 2019 manual in 2026 should not assume every named standard number or framework label is still current. The professional themes—independence, competence, quality, risk, control, and integrity—remain durable, but official terminology should be checked against the syllabus actually being tested. This matters especially for transition-language candidates who may be using a 2019 exam while working in organizations that have already adopted the Global Internal Audit Standards.
Use legacy material for history, but prepare from the syllabus you will actually test on
The 2019 Part 1 remains valuable for understanding how the CIA previously organized independence, quality, risk, control, and fraud. It also appears in older employer training plans, textbooks, review systems, and language-specific transition schedules. That makes it important to identify the exact language and testing date before discarding or relying on an older resource.
Exam practice is stronger when each older domain is translated into a decision. For independence, decide whether an impairment exists and what safeguard is appropriate. For quality, decide what evidence would show the function is effective. For control, distinguish a design gap from a failure of operation. For fraud, decide when additional work or escalation is justified. That approach prevents legacy preparation from becoming an exercise in remembering old headings without understanding the professional behavior they were designed to assess.
For most candidates in 2026, the practical study decision is straightforward: use the current syllabus and current standards terminology, and treat this page as a map of the prior version. The revised exam absorbs and reorganizes many durable concepts rather than making them irrelevant. Knowing what changed prevents a candidate from spending disproportionate time on an old domain structure while still preserving the professional principles that carry forward.
IIA IIA-CIA-Part1 practice test questions and answers, training course, study guide are uploaded in ETE Files format by real users. Study and Pass IIA-CIA-Part1 CIA Part 1 - Essentials of Internal Auditing certification exam dumps & practice test questions and answers are to help students.
Exam Comments * The most recent comment are on top
- IIA-CIA-Part1 - CIA Part 1 - Essentials of Internal Auditing
- IIA-CIA-Part2 - Certified Internal Auditor - Part 2, Practice of Internal Auditing
- CIA-Part2-2025 - CIA Part 2 - Internal Audit Engagement
- IIA-CIA-Part3 - Certified Internal Auditor - Part 3, Business Analysis and Information Technology
- IIA-CHAL-QISA - Qualified Info Systems Auditor CIA Challenge
- CIA-Part1-2025 - CIA Part 1 - Internal Audit Fundamentals
Purchase IIA IIA-CIA-Part1 Exam Training Products Individually
Why customers love us?
What do our customers say?
The resources provided for the IIA certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the IIA-CIA-Part1 test and passed with ease.
Studying for the IIA certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the IIA-CIA-Part1 exam on my first try!
I was impressed with the quality of the IIA-CIA-Part1 preparation materials for the IIA certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The IIA-CIA-Part1 materials for the IIA certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the IIA-CIA-Part1 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my IIA certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for IIA-CIA-Part1. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the IIA-CIA-Part1 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my IIA-CIA-Part1 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my IIA certification without these amazing tools!
The materials provided for the IIA-CIA-Part1 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed IIA-CIA-Part1 successfully. It was a game-changer for my career in IT!


