ITIL OSA: What the Legacy Operational Support and Analysis Exam Covered
ITIL Operational Support and Analysis, commonly shortened to OSA, was an ITIL v3 Intermediate Capability module focused on the work needed to run and support live services. The exam is now legacy. PeopleCert no longer offers the English-language ITIL v3 Intermediate pathway as a current route, and current certification planning has moved through ITIL 4 and now toward ITIL (Version 5).
OSA still appears in training records, résumés, archived exam pages, and older organizational learning plans, so understanding what it represented remains useful. PeopleCert continues to recognize ITIL v3 certifications as historical credentials and explicitly notes that the current three-year renewal rule does not apply to v3 products such as OSA.
The module sat between Foundation and the higher ITIL Expert pathway. It concentrated on operational practices such as event, incident, request, problem, and access management, along with the service desk and technical operating functions. That makes it historically related to several topics now distributed across modern ITIL certifications.
OSA was designed around the reality of live service operation
Service operation is where customers and users experience the consequences of design and transition decisions. A service may look complete on paper but fail operationally because alerts are noisy, incidents are poorly coordinated, requests are inconsistent, knowledge is weak, or technical teams do not share ownership.
OSA addressed that operating reality by bringing together capabilities used every day in support environments. The candidate needed to understand not only each process or function but also how they combined to restore service, fulfill normal demand, control access, detect significant events, and reduce recurring disruption.
Because the module belonged to ITIL v3, its language was more process-centric than modern ITIL 4 practice guidance. Readers using OSA material today should preserve that historical context rather than silently replacing every term with a newer one.
Event Management created awareness of important service conditions
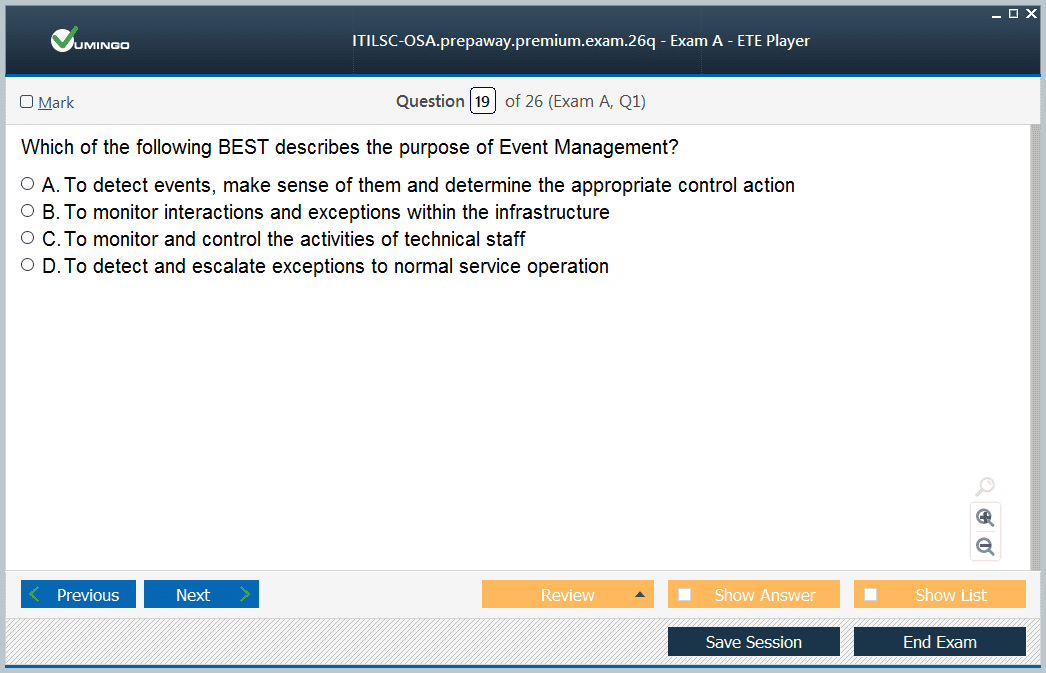
Event Management dealt with detectable occurrences that had significance for managing services and infrastructure. The aim was to make operational state visible so teams could decide whether to record, filter, correlate, escalate, automate, or otherwise respond to an event.
Normal, warning, and exception conditions helped determine response. Not every event was an incident, and not every alert needed human action. Effective operations depended on filtering and correlation so operators could identify the signal that mattered without being overwhelmed by repetitive technical noise.
The modern ITIL 4 Monitoring and Event Management module covers related ground with updated practice language, value-stream thinking, capability concepts, and contemporary technology context. It is not a renamed OSA exam, but the operational lineage is easy to see.
Incident Management prioritized restoration of normal service
Incident Management focused on returning service to users as quickly as practical after an interruption or reduction in quality. Diagnosis was important, but the immediate priority was restoration. A workaround could therefore be a successful incident response even if the deeper cause remained unresolved.
Priority depended on impact and urgency rather than emotion or ticket order alone. Major incidents required stronger coordination, communication, escalation, and decision authority because the cost of delay was higher. Models for common incidents helped teams respond consistently without redesigning the workflow each time.
This distinction between restoration and root cause remains relevant. Modern operational teams can lose valuable time when they insist on completing deep technical analysis before restoring a service that has a safe workaround available.
Request Fulfilment separated normal user demand from incidents
ITIL v3 used the term Request Fulfilment for handling standard user requests, such as information, access to a standard service, or routine service actions. These requests were expected demand rather than failures and could therefore be standardized, approved, measured, and automated differently from incidents.
Clear request models reduce unnecessary decisions. When eligibility, approval, fulfillment steps, target times, and closure conditions are known, work can flow more predictably. The modern ITIL 4 Service Request Management practice develops the same broad operational need using current practice terminology.
For historical OSA study, candidates needed to understand why combining incidents and service requests into one undifferentiated queue created poor control. The two types of demand can share tools and support channels while still requiring different objectives and workflows.
Problem Management aimed to reduce future incidents and their impact
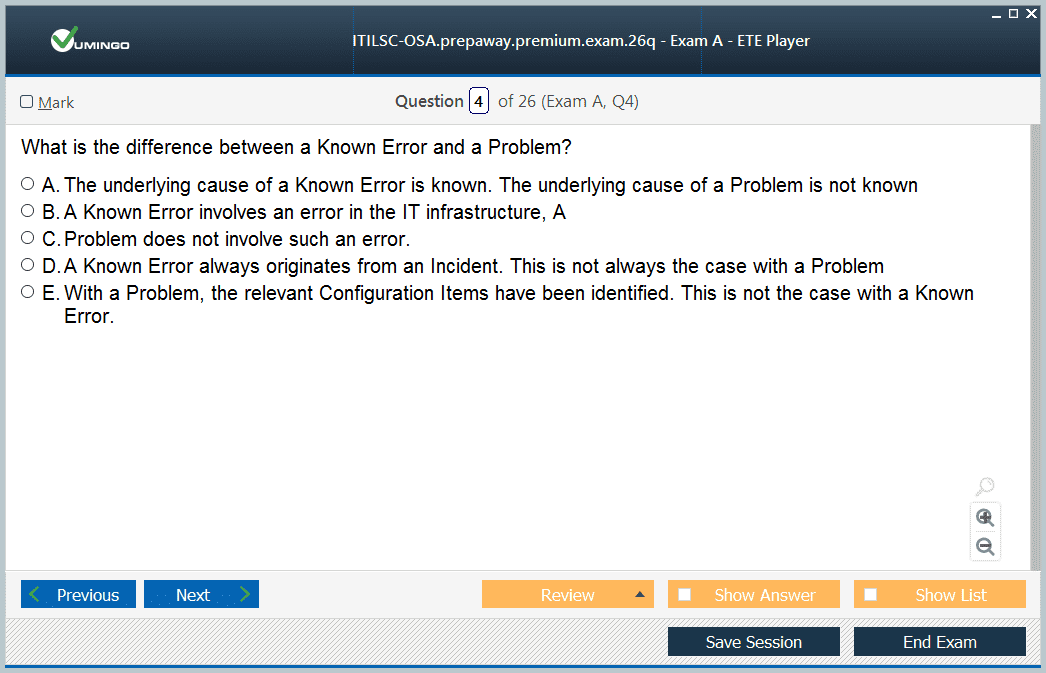
Problem Management investigated causes and managed the lifecycle of problems and known errors. Reactive work followed incidents that had already occurred, while proactive work used trends and analysis to identify risks before they produced major disruption.
Known errors and workarounds were important because permanent fixes are not always immediate. A technical correction may require a major release, supplier action, architecture change, or budget decision. Recording the diagnosis and workaround allows the organization to reduce impact while the long-term response is planned.
The current ITIL 4 Problem Management module retains the operational objective while placing the practice in a newer management system. Candidates comparing versions should look for continuity in purpose and difference in framework structure.
Access Management controlled authorized use of services
Access Management was concerned with granting authorized users the right to use services while preventing unauthorized access. That required accurate identity information, approved policies, request and revocation workflows, and coordination with security management.
Access work often looks routine until an exception appears. A role change, emergency privilege request, terminated employee, shared account, or conflicting entitlement can create significant risk. Good control therefore depends on both efficient fulfillment and reliable authorization evidence.
Modern organizations may implement these controls through identity and access management platforms, automated provisioning, role models, and privileged access systems. The tooling has evolved, but the management question remains: who should have access to what, under whose authority, for how long, and with what evidence?
The service desk and technical functions gave the processes an operating home
OSA also addressed the Service Desk plus Technical Management, IT Operations Management, and Application Management. These were functions in the ITIL v3 model rather than simply additional processes. Their roles helped explain who performed work and where expertise sat within the service organization.
The service desk provided a primary point of contact for users and coordinated communication around incidents and requests. Technical and application teams supplied specialist knowledge, while IT operations executed routine operational activities. The model highlighted the need to connect user-facing support with the teams that understood infrastructure and applications.
Current ITIL language is less dependent on fixed functional structures because organizations may use product teams, platform teams, managed providers, cloud services, or other operating models. The underlying need for clear responsibility and communication has not disappeared.
Current ITIL modules redistribute OSA's subject matter
A professional looking for a modern equivalent should not search for one exam with the OSA name. Its subject matter now appears across multiple ITIL 4 practice modules and bundled certifications. Monitor, Support and Fulfil is the closest broad operational grouping because it combines monitoring, incident, service desk, request, and problem practices.
Create, Deliver and Support adds wider value-stream, team, technology, supplier, and support context. ITIL Foundation in both ITIL 4 and Version 5 provides the modern entry-level framework for candidates who are no longer operating inside the v3 credit system.
This is why archived OSA material should preserve continuity without claiming direct equivalence. The operational problems remain recognizable, but the certification architecture and management language have changed.
Legacy credentials remain evidence of prior achievement
PeopleCert states that the three-year certification renewal rule does not apply to ITIL v3 certifications such as OSA. That is different from saying the old exam can still be booked. Existing holders retain evidence of the qualification they earned under the historical scheme, while new candidates use current pathways.
The discontinuation of ITIL v3 explains why OSA belongs to a retired qualification structure even though many of its operational ideas remain recognizable. Candidates should nevertheless use current PeopleCert information when deciding what certification to pursue now.
For someone reviewing old OSA material, the best use is conceptual and historical: understand how mature service organizations handled operational demand, then compare those ideas with the current framework. Trying to prepare for a retired exam as though a live voucher still exists wastes effort.
One reason OSA remains useful as historical study is that it shows how operational processes depend on consistent prioritization. An incident can be urgent without being high impact, a service request can be time-sensitive without representing a failure, and a problem can deserve investigation even when no major incident is open. Teams therefore needed agreed criteria for impact, urgency, categorization, escalation, ownership, and closure. Those rules made operational records comparable and helped managers decide where scarce support capacity should go. The terminology and organizational design have evolved in later ITIL versions, but the underlying management problem has not disappeared. Modern support organizations still need to distinguish restoration from root-cause work, normal fulfilment from disruption, and access authorization from general service-desk interaction. Reading OSA through those enduring operational decisions makes the legacy material more useful than treating it as a list of retired process names.
A useful review follows one incident across the entire operating model
Take a realistic outage and trace it through Event Management, Incident Management, the Service Desk, Technical Management, and Problem Management. Add a related user request and an access requirement. Ask which information is created at each point, who owns the decision, and what evidence should be retained.
Then translate the same scenario into current ITIL practice language. This exercise shows which management needs have persisted and which structures changed. It also prevents the common mistake of assuming that a newer framework invalidates every operational lesson from its predecessor.
OSA is best understood as a legacy operational capability module with continuing historical value. It is not the current exam route, but the disciplines it brought together—awareness, restoration, fulfillment, prevention, access control, and user communication—remain fundamental to reliable digital service operation.







 83% students found the test questions almost same




