
- Home
- CIW Certifications
- 1D0-571 CIW v5 Security Essentials Dumps
Pass CIW 1D0-571 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!


1D0-571 Premium File
- Premium File 62 Questions & Answers. Last Update: Oct 23, 2026
Whats Included:
- Latest Questions
- 100% Accurate Answers
- Fast Exam Updates
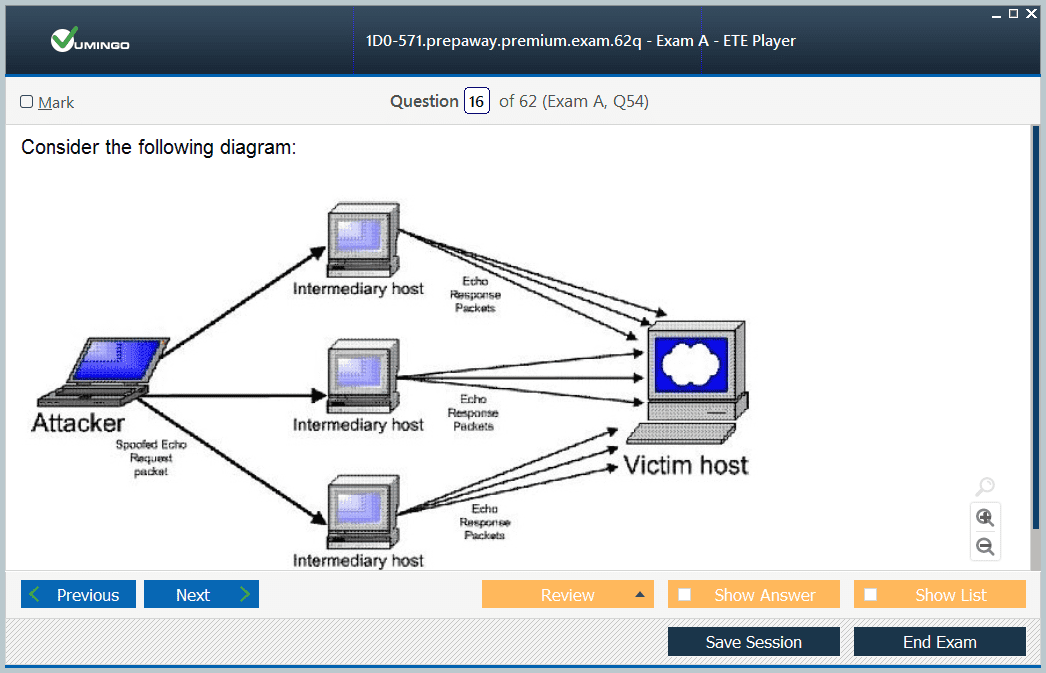
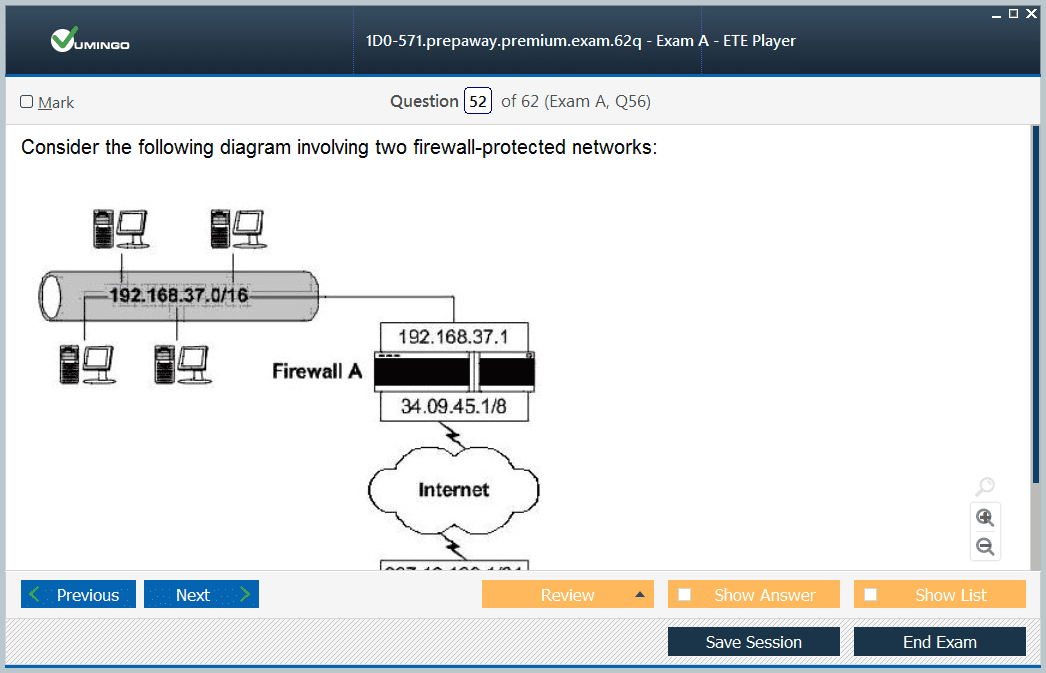
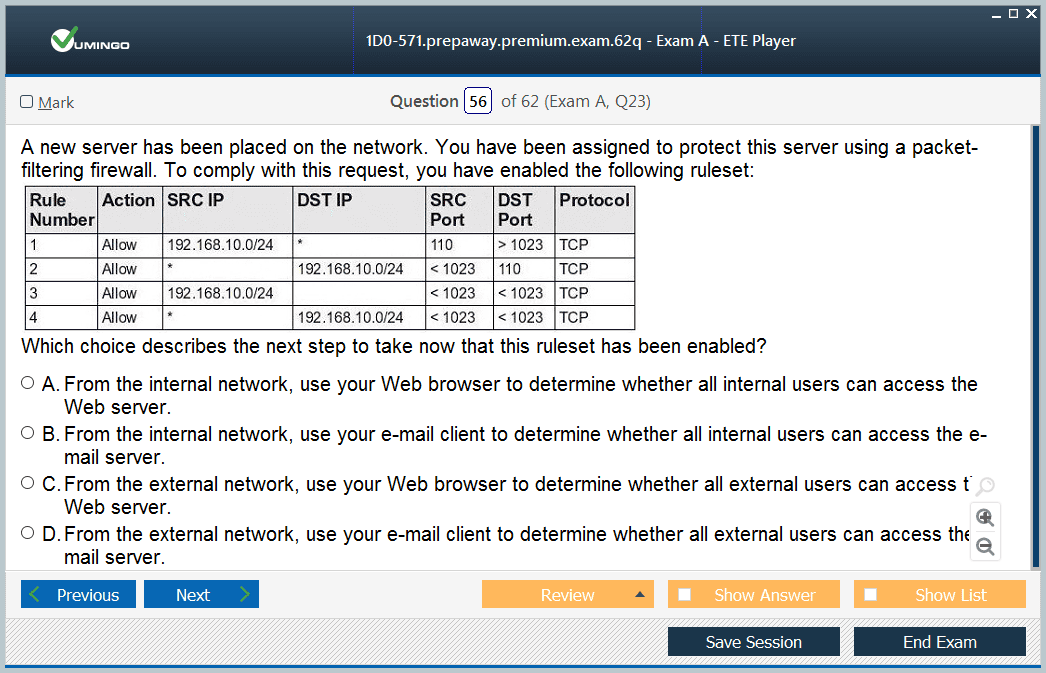
Last Week Results!
 83% students found the test questions almost same
All CIW 1D0-571 certification exam dumps, study guide, training courses are Prepared by industry experts. PrepAway's ETE files povide the 1D0-571 CIW v5 Security Essentials practice test questions and answers & exam dumps, study guide and training courses help you study and pass hassle-free!
1D0-571: CIW Web Security Associate (Retired)
CIW 1D0-571 is a retired Web Security Associate exam. Certification Partners lists it among the CIW exams retired on December 31, 2021, so candidates should not expect the code to be schedulable today. CIW continues to offer a Web Security Associate credential under a newer exam generation; its current course and voucher material identifies 1D0-671. Because 1D0-571 is historical and CIW can update program identifiers, candidates should confirm the live security exam and its current requirements directly before registering.
The older 1D0-571 scope remains useful because the fundamentals it addressed are durable: security policy, risk, authentication, access control, cryptography, common attacks, secure protocols, firewalls, VPNs, detection, incident response, and layered defense. What has changed is the threat landscape, technology stack, and terminology around those principles. Historical study material should therefore be used to learn concepts, not as evidence of current tools or exam availability.
Current CIW certifications place security on a newer exam generation, but the networking foundation remains essential. 1D0-61C Network Technology Associate develops the addressing, protocol, and connectivity knowledge that security controls depend on, while 1D0-610 Web Foundations Associate supplies the broader Internet-technology base. In practice, firewall administration turns policy into rule review, logging, change control, and incident evidence—the operational side of controls that the security path expects candidates to understand.
Security policy translates organizational risk into enforceable rules
A security policy defines what an organization is protecting, which behavior is permitted, who owns decisions, how exceptions are approved, and what happens when controls fail. Useful policies are specific enough to guide configuration and response but flexible enough to survive product changes. Candidates should understand acceptable-use policies, password and authentication standards, data-handling requirements, incident reporting, remote access, and device rules as parts of one governance system.
Risk assessment connects those rules to threats and business impact. Identify assets, vulnerabilities, threat actors, likelihood, impact, and existing controls. A small public website and a payment system may face similar technical attacks but have different consequences. Prioritization should follow business risk rather than the novelty of a threat. Practice describing which control reduces which risk and what residual exposure remains after the control is applied.
Authentication and access control should minimize unnecessary privilege
Authentication establishes identity; authorization determines what that identity can do. Passwords, certificates, tokens, multifactor authentication, biometrics, and federated identity provide different assurance properties. Access control models and ACLs then restrict resources based on users, groups, roles, attributes, or policy. The security objective is not simply to make login difficult; it is to make unauthorized access difficult while preserving legitimate work.
Least privilege applies to administrators, applications, service accounts, and normal users. Shared administrator accounts weaken accountability, while broad service permissions increase the blast radius of compromise. Review privileges periodically and remove access when roles change. Strong access control also includes session timeout, account lockout, recovery procedures, and protection of the systems that issue credentials.
Cryptography protects confidentiality, integrity, and identity when used correctly
Symmetric encryption is efficient for bulk data, asymmetric cryptography supports key exchange and digital signatures, and hashing creates one-way integrity values. Public Key Infrastructure combines certificates, certificate authorities, trust chains, revocation, and private-key protection so systems can authenticate peers and establish encrypted sessions. Candidates should understand the purpose of each mechanism instead of treating “encryption†as one interchangeable feature.
Cryptography can fail through weak keys, obsolete algorithms, exposed private keys, poor random-number generation, certificate expiration, trust misconfiguration, or protocols that negotiate insecure options. Operational discipline therefore matters as much as algorithm choice. Inventory certificates and keys, define renewal ownership, disable deprecated protocols, and monitor failures. Encryption also has performance cost, so capacity tests should represent the secure configuration used in production.
Attack methods reveal where preventive controls are insufficient
Malware, phishing, credential attacks, denial of service, spoofing, session attacks, injection, privilege escalation, social engineering, and insider misuse target different weaknesses. Effective study focuses on attacker goals and preconditions. For example, credential stuffing depends on reused credentials, while injection exploits unsafe handling of untrusted input. The defensive response should address the enabling condition rather than only the visible symptom.
Defense in depth assumes that individual controls can fail. Endpoint protection, network segmentation, secure configuration, authentication, application validation, monitoring, backups, and user education overlap so one failure does not automatically become a breach. Map an attack path and identify which controls would prevent, detect, or contain each stage. That exercise is more valuable than memorizing lists of attack names.
Protocol security depends on understanding the network path
Web security sits on networking foundations. DNS, DHCP, ARP, IP routing, TCP sessions, HTTP, TLS, email protocols, and remote administration each have security implications. A service can be securely configured at the application layer and still be exposed through an unintended management port or flat network segment. Candidates should be able to identify what traffic is required and what traffic should be blocked.
Secure protocols replace or encapsulate insecure equivalents, but they also require certificate and key management. Segmentation limits lateral movement, while network access controls reduce exposure between trust zones. Capture traffic in a lab and identify which parts are visible, encrypted, authenticated, or unauthenticated. This connects abstract protocol knowledge to evidence an analyst or administrator can actually observe.
Firewalls and VPNs enforce boundaries but do not define the entire security posture
Packet-filtering, stateful, proxy, application-aware, and host-based firewalls operate with different context. Rules should express required flows explicitly and be reviewed for shadowed, duplicated, expired, or overly broad entries. A rule that permits “any to any†for convenience can erase the benefit of network segmentation. Change control should record why a rule exists and when it can be removed.
VPNs protect traffic across untrusted networks and extend access to remote users or sites. Full-tunnel, split-tunnel, clientless, and site-to-site designs create different exposure and routing behavior. Authentication strength, endpoint posture, DNS behavior, address assignment, and route control all matter. Test remote access from realistic networks and define what happens when the VPN is connected but an internal service is unreachable.
Detection and incident response turn security events into controlled action
Logs from endpoints, applications, firewalls, authentication systems, servers, and network devices can reveal suspicious behavior, but collection alone is not detection. Organizations need time synchronization, retention, parsing, baselines, alert logic, ownership, and escalation. Alerts should connect to specific response actions so teams are not overwhelmed by signals nobody has time or authority to investigate.
Incident response normally includes preparation, identification, containment, eradication, recovery, and lessons learned. Evidence must be preserved carefully when legal or disciplinary consequences are possible. Containment decisions depend on business impact: isolating a server may stop an attacker but also stop a critical service. Practice building a timeline from logs and deciding which action reduces risk without destroying the evidence needed to understand the incident.
Move from retired 1D0-571 material to the current CIW security generation
Certification Partners’ retirement notice establishes that 1D0-571 is historical, while the current CIW Web Security Associate page uses a newer exam code and updated objectives. Candidates seeking certification should use the live CIW page, current exam requirements, and current curriculum. Third-party pages that continue to sell 1D0-571 material cannot make the retired code active again.
The best preparation is to retain the old exam’s core security model while updating examples. Learn policy, CIA objectives, access control, cryptography, protocol security, firewalls, VPNs, detection, and incident response through current tools and threats. Build small labs that produce observable logs, enforce least privilege, use modern TLS, segment traffic, and test response procedures. That approach turns historical certification content into practical security skill rather than obsolete exam trivia.
Vulnerability management belongs between prevention and incident response. Organizations need a process to discover assets, identify weaknesses, prioritize remediation, test patches or configuration changes, and verify closure. Severity scores are useful inputs but not complete risk decisions; an exposed critical server and an isolated lab system may require different urgency. Track exceptions with owners and expiry dates so temporary risk acceptance does not become permanent neglect.
Secure configuration baselines reduce preventable exposure. Disable unused services, change default credentials, restrict management interfaces, remove unnecessary software, apply supported updates, and compare systems against approved standards. Configuration drift should be detectable. A server that was hardened at deployment can become vulnerable months later as emergency changes accumulate, so security is a lifecycle process rather than a one-time build step.
Backups are a security control when they are protected from the same compromise that affects production. Ransomware and destructive attacks can target connected backup repositories, so recovery copies need appropriate isolation, access control, retention, and restore testing. A backup that has never been restored is only an assumption. Incident plans should specify which systems are restored first and how teams confirm that recovered data is clean.
Security awareness should be tied to realistic behavior. Users need to recognize suspicious requests, protect credentials, report incidents quickly, and understand why bypassing controls creates risk. Training is more effective when it explains the business consequence of an action and gives a clear reporting path. Blaming users after an incident does not improve the control environment; designing systems that make the safe action easier does.
For hands-on study, create a small segmented lab and deliberately generate evidence. Fail a login repeatedly, trigger a firewall block, inspect a TLS certificate, capture a benign scan, change a file permission, and review the resulting logs. Then write a short incident timeline and containment plan. This turns security vocabulary into observable behavior and makes it easier to distinguish prevention, detection, response, and recovery controls.
Change management completes the control cycle. Firewall rules, authentication settings, certificates, endpoint policies, and server configurations should be reviewed and tested before release, with rollback steps for changes that cause unexpected impact. Security teams need enough documentation to distinguish an authorized change from suspicious activity. This reduces false alarms and prevents emergency fixes from silently weakening protections.
CIW 1D0-571 practice test questions and answers, training course, study guide are uploaded in ETE Files format by real users. Study and Pass 1D0-571 CIW v5 Security Essentials certification exam dumps & practice test questions and answers are to help students.
Exam Comments * The most recent comment are on top
Why customers love us?
What do our customers say?
The resources provided for the CIW certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the 1D0-571 test and passed with ease.
Studying for the CIW certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the 1D0-571 exam on my first try!
I was impressed with the quality of the 1D0-571 preparation materials for the CIW certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The 1D0-571 materials for the CIW certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the 1D0-571 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my CIW certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for 1D0-571. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the 1D0-571 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my 1D0-571 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my CIW certification without these amazing tools!
The materials provided for the 1D0-571 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed 1D0-571 successfully. It was a game-changer for my career in IT!


