
- Home
- McAfee Certifications
- MA0-100 Certified McAfee Security Specialist - ePO Dumps
Pass McAfee MA0-100 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!


MA0-100 Premium File
- Premium File 157 Questions & Answers. Last Update: Oct 30, 2026
Whats Included:
- Latest Questions
- 100% Accurate Answers
- Fast Exam Updates
Last Week Results!
 83% students found the test questions almost same
MA0-100 McAfee ePO: Legacy Product Specialist Skills and Current Trellix ePolicy Orchestrator
MA0-100 was associated with the McAfee Certified Product Specialist credential for ePolicy Orchestrator, commonly shortened to ePO. The exam code and McAfee credential belong to an earlier certification period, while the ePolicy Orchestrator platform continues under Trellix branding. Candidates should therefore treat MA0-100 as a legacy product-specialist reference rather than assume the old exam identifier represents a current Trellix certification.
The enduring subject is centralized security management. ePO brings systems, policies, endpoint products, tasks, software deployment, reporting, permissions, and operational monitoring into a common management plane. Historical McAfee certifications included several product-specific credentials, and MA0-100 is best understood in that practical administrative tradition.
ePO architecture connects the server, database, repositories, and managed systems
An ePO deployment depends on more than the web console. The management server coordinates policy and task configuration, a database stores operational and configuration data, repositories distribute product content, and agents on managed systems communicate with the server. Depending on deployment design, agent handlers or other components can distribute communication load and extend reach across network boundaries.
Administrators need to understand what each component owns. A console page that fails to load may indicate an application or database issue, while endpoints that stop receiving policy may point to agent-server communication, certificates, DNS, firewall rules, handlers, or repository access. Treating all symptoms as “the ePO server is down” prevents efficient isolation.
Scale changes design decisions. An environment with a few hundred endpoints can tolerate patterns that become problematic across many sites or tens of thousands of systems. Repository placement, wake-up traffic, deployment windows, database maintenance, and communication intervals should reflect network topology and operational constraints.
The System Tree turns organizational structure into management scope
The System Tree groups managed systems and provides a basis for policy assignment, tasks, permissions, and reporting. Groups can reflect geography, business units, server roles, endpoint types, or another stable management model. The most useful hierarchy is not necessarily the company's org chart; it is the structure that makes security policy and operational ownership predictable.
Sorting criteria and tags can automate placement and classification. That automation should be designed so administrators can explain why a system belongs to a group and what happens when its attributes change. Overlapping sorting rules or poorly scoped tags can move systems unexpectedly and apply the wrong policy.
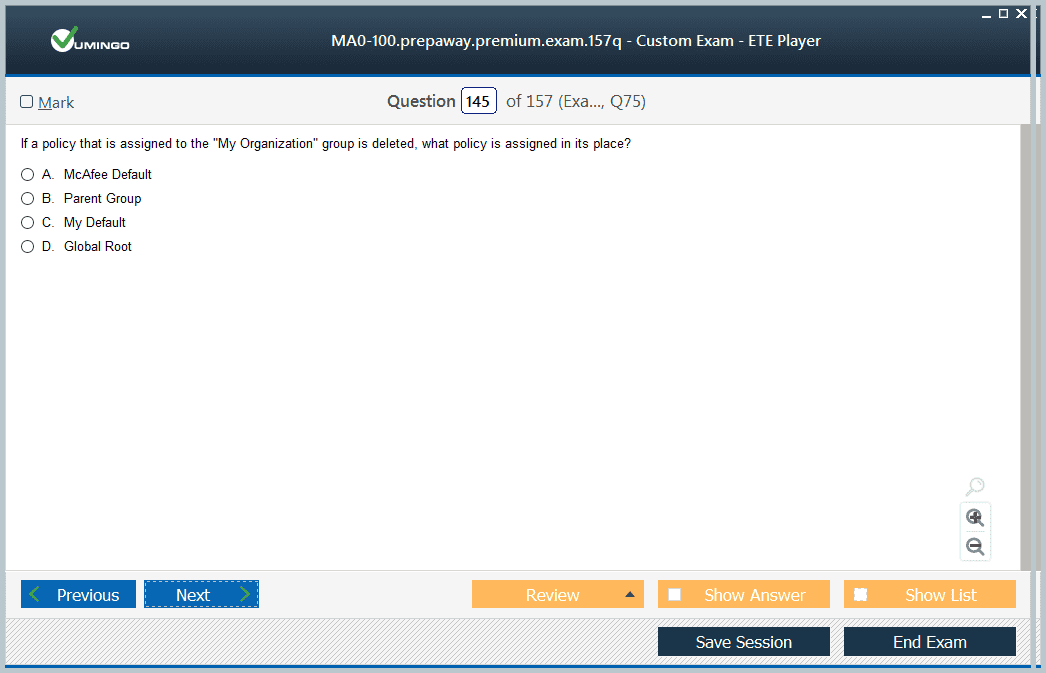
Inheritance is a major concept. Child groups can inherit policies or tasks from parents, while exceptions can break inheritance where necessary. Excessive exceptions create a tree that looks organized but behaves unpredictably. A strong administrator keeps the default path simple and documents the reasons for deviations.
Policies and client tasks solve different management problems
Policies define persistent configuration for managed products, while client tasks instruct systems to perform actions such as updating, scanning, or deploying software. Confusing the two leads to fragile administration. A desired configuration belongs in policy; a one-time or scheduled action belongs in an appropriate task.
Policy assignment rules can add context beyond simple System Tree location. A server, laptop, sensitive workstation, or device with a particular tag may need different settings. Rules should remain understandable because multiple overlapping assignments can make it difficult to determine which policy is effective.
Task scheduling also needs operational judgment. Deploying an agent or endpoint product to every system at once can saturate repositories or network links. Security work frequently competes with business availability, so phased deployments, maintenance windows, pilot groups, and clear success criteria are part of competent ePO administration.
Agent-server communication is the heartbeat of centralized management
The management agent collects policy, sends properties and events, runs tasks, and maintains communication with ePO. If that loop breaks, a system may remain visible in the console while gradually becoming stale. Administrators should know how to distinguish a missing system from one that has stopped communicating and how to inspect last-communication times and agent state.
Wake-up calls can request near-immediate communication, but they are not a substitute for healthy regular intervals. Network address translation, remote work, firewalls, DNS, proxy behavior, and handler placement can all affect reachability. Troubleshooting begins by identifying the direction and protocol of the failed communication rather than repeatedly forcing wake-ups.
Duplicate or stale system records also require care. Reimaging, hostname reuse, virtual machine cloning, and agent identity can create confusing entries. Deleting records without understanding identity behavior can hide the symptom while allowing duplicates to return.
Repositories and software management determine how content reaches endpoints
Security products depend on engines, signatures, modules, and application packages that must reach managed systems. ePO repositories and software management features provide controlled distribution, but administrators must understand source repositories, distributed repositories, replication, package check-in, and client update behavior.
Content freshness has to be balanced with network design. A remote site should not necessarily download the same large package independently to every endpoint across a constrained WAN link. Distributed repositories can localize transfer, but they add replication and health considerations of their own.
Software deployment should be treated like a release. Validate prerequisites, pilot a representative group, monitor success and failure states, and plan rollback or remediation. An endpoint product upgrade can affect drivers, network traffic, reboot requirements, and application compatibility, so “task completed” is not the only success metric.
Server tasks and extensions control work that happens inside the management platform
Not every automated action runs on an endpoint. ePO server tasks can perform scheduled imports, synchronization, cleanup, query-driven actions, repository work, and other platform-side operations. Administrators should know whether an automation is a client task, a server task, or an external integration because each has different timing, permissions, failure evidence, and load characteristics.
Product extensions add console pages, policy definitions, events, reports, and management logic for the security products controlled by ePO. Extension compatibility is therefore part of platform maintenance. Upgrading the ePO server without checking installed product extensions can leave administrators with a healthy core console but broken product management. A controlled change process inventories extensions, verifies supported combinations, backs up the platform, and validates the management functions that matter after an upgrade.
Queries, reports, dashboards, and events turn management data into decisions
ePO collects system properties, product state, threat events, deployment results, and other management data. Queries filter and aggregate that data; reports and dashboards make the results accessible to operations teams. The practical skill is framing a question precisely enough that the report leads to an action.
For example, “systems without the newest content” is more useful when it distinguishes devices that are online but failing updates from devices that have not communicated for weeks. The remediation paths differ. Similarly, a dashboard showing malware events should separate a single noisy endpoint from a broad outbreak.
Reporting also depends on data retention and database health. Keeping every event forever increases storage and query cost, while purging too aggressively removes evidence needed for investigation or compliance. Retention should follow operational and legal requirements rather than arbitrary defaults.
Roles and permission sets should match administrative responsibilities
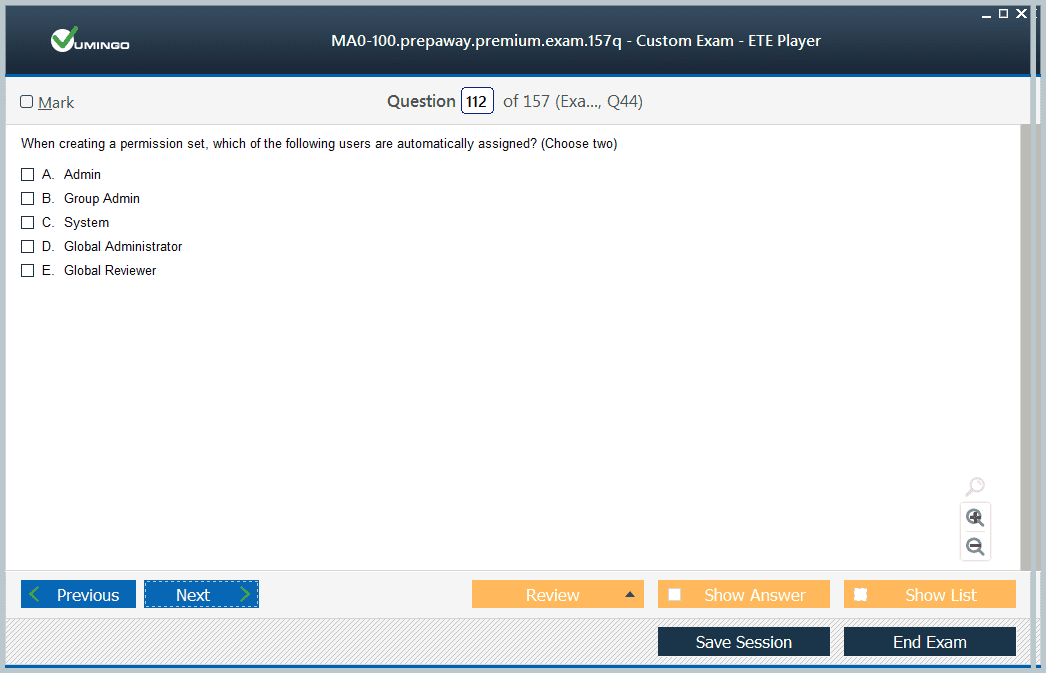
A centralized console can control many endpoints, so administrative access needs careful scoping. Permission sets, System Tree access, product-specific rights, and account roles should provide enough capability for a job without granting unrestricted authority. Help-desk staff may need visibility and limited actions, while platform administrators need broader configuration access.
Shared accounts weaken accountability. Individual authentication, strong credential practices, and audit logging make it possible to determine who changed a policy or initiated a deployment. Integration and service accounts should be separated from human administrators and protected according to their privilege.
Permissions also interact with organizational structure. A regional administrator may need control over one System Tree branch but not another. Designing the tree and roles together produces cleaner delegation than building a complex hierarchy first and trying to retrofit permissions later.
Backup, maintenance, and troubleshooting keep the management plane reliable
Because ePO coordinates security operations, its own resilience matters. Administrators should know the platform's backup and recovery requirements for database content, server configuration, keys or certificates, and any files needed to restore communication with existing agents. A database-only backup may not represent a complete recovery plan.
Routine maintenance includes database health, repository cleanup, log review, expired or stale systems, failed tasks, certificate health, software extensions, and platform updates. Changes should be tested and documented because an ePO upgrade can affect managed-product extensions and integrations.
Troubleshooting should proceed layer by layer: browser and console behavior, application services, database connectivity, server logs, handler status, network communication, agent logs, repository access, and product-specific state. That structured approach reduces the temptation to restart components until the symptom disappears.
Integration points also deserve operational attention. Directory synchronization, ticketing systems, reporting exports, APIs, and product connectors can extend ePO beyond the console, but they introduce credentials, schedules, and dependencies that may fail independently. An administrator should know which external process created or changed an object and should monitor integrations for silent failure rather than assuming a successful server status means the wider management workflow is healthy.
Current Trellix ePO work carries forward the management principles
The old MA0-100 credential is historical, but ePolicy Orchestrator remains a current Trellix platform with both modern deployment options and continuing on-premises use. That makes the core administrative ideas—system organization, policy, task automation, software distribution, reporting, access control, and platform health—still valuable to practitioners.
The related MA0-101 Network Security Platform and MA0-104 SIEM pages show why the historical McAfee certification program was product-oriented: each tool solved a different part of enterprise security operations. ePO was the central management problem, not a general cybersecurity theory exam.
For present-day learning, use a supported Trellix environment and current product documentation for exact interfaces and capabilities. Use MA0-100 as a skills map for the management discipline behind ePO, not as evidence that a legacy McAfee exam is still available under the same code.
Why customers love us?
What do our customers say?
The resources provided for the McAfee certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the MA0-100 test and passed with ease.
Studying for the McAfee certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the MA0-100 exam on my first try!
I was impressed with the quality of the MA0-100 preparation materials for the McAfee certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The MA0-100 materials for the McAfee certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the MA0-100 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my McAfee certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for MA0-100. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the MA0-100 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my MA0-100 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my McAfee certification without these amazing tools!
The materials provided for the MA0-100 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed MA0-100 successfully. It was a game-changer for my career in IT!


