
- Home
- Huawei Certifications
- H12-711 HCNA-Security-CBSN (Huawei Certified Network Associate - Constructing Basic Security Network) Dumps
Pass Huawei H12-711 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!


H12-711 Premium File
- Premium File 52 Questions & Answers. Last Update: Nov 10, 2026
Whats Included:
- Latest Questions
- 100% Accurate Answers
- Fast Exam Updates
Last Week Results!
 83% students found the test questions almost same
Huawei H12-711: Legacy HCNA Security Foundations and the Move to HCIA-Security
Huawei H12-711 is an exam code with a long security lineage. Older material identifies it with HCNA-Security-CBSN, or Constructing Basic Security Network, while Huawei later used the H12-711 code for HCIA-Security versions. That history makes version context essential: a candidate should not assume an old H12-711 study source describes the security curriculum currently offered by Huawei.
The historical HCNA-era page is best treated as a legacy security foundation. Current candidates should look toward HCIA-Security V4.0 and the wider Huawei certifications. Many underlying ideas—firewall policy, network segmentation, authentication, VPNs, cryptography, and secure operations—remain useful, but products, versions, attack techniques, and recommended controls continue to evolve.
The strongest way to study a legacy security exam is to separate durable principles from historical implementation details. Ask what threat a feature was intended to reduce, where enforcement occurs, what information the control relies on, how it can fail, and how an operator can verify that it is working.
Security architecture begins with trust boundaries and explicit policy
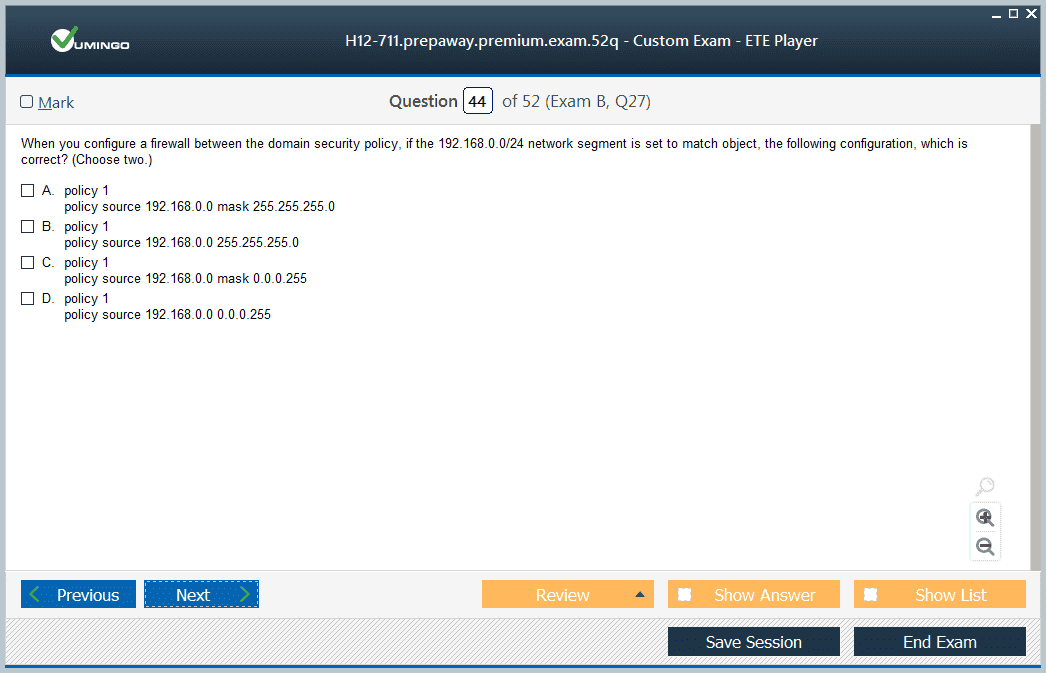
Network security controls are easier to reason about when the network is divided into zones with defined trust relationships. A firewall can then apply policy based on source, destination, service, user, application, or other context. The purpose is to make allowed communication intentional rather than letting every reachable system communicate freely.
Zone design should follow business and risk boundaries, not just interface count. User networks, servers, management systems, Internet connections, partner links, and guest access often require different rules. A clear policy also improves troubleshooting because engineers can ask which boundary a flow crosses and which rule is expected to permit or deny it.
Firewall policy must be precise enough to protect services and simple enough to operate
Firewall rules accumulate over time as applications change. Broad temporary rules can become permanent, duplicate policies can hide intent, and object groups can drift away from the systems they are supposed to represent. Good firewall administration therefore includes rule ownership, review, logging, change control, and removal of obsolete access.
Operators should test both the intended allowed path and important denied paths. A rule that permits the application is only half the requirement; the firewall should continue blocking unrelated traffic. Logs are useful when they are tied to policy intent rather than collected without a process for review.
NAT changes addresses, but it does not replace a security policy
Network Address Translation can hide internal addressing or map services between address spaces, but translation and authorization are different functions. A translated flow may still need an explicit security rule, and an allowed security policy can still fail if the translation is wrong. Troubleshooting should examine both.
NAT design also affects logging and incident analysis. Teams need to be able to map an observed translated address and port back to the original system when investigating an event. Time synchronization and retained logs become important because large pools can reuse the same public addresses across many internal sessions.
VPNs protect traffic across untrusted networks through cryptographic negotiation
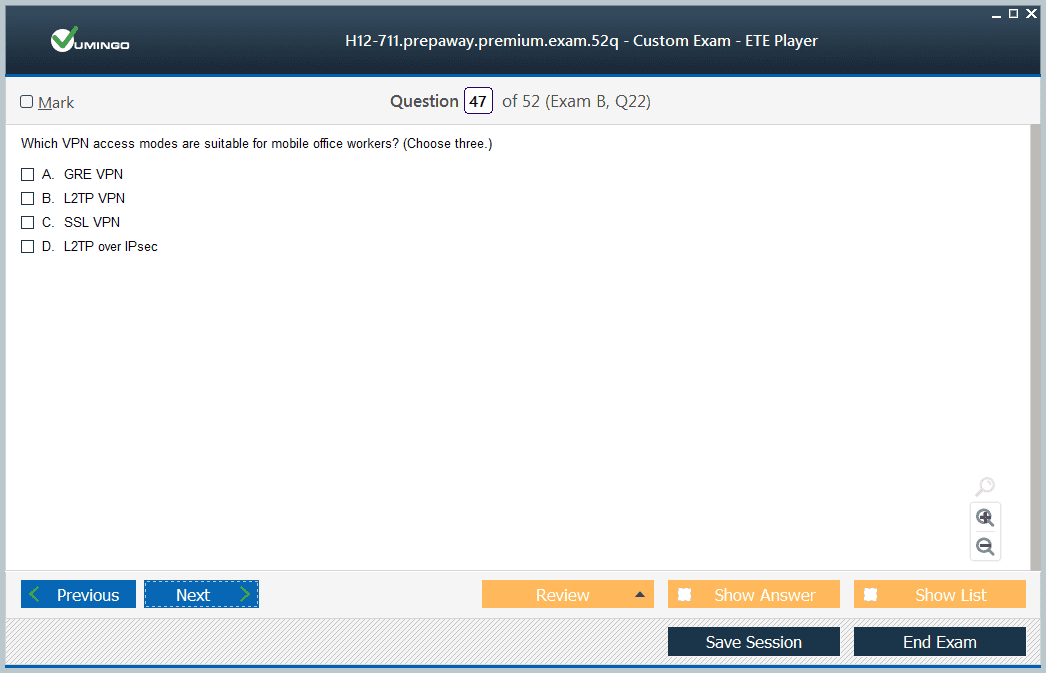
IPsec VPNs use security associations, authentication, encryption, integrity protection, and key exchange to create protected communication between peers. Engineers should understand why the peers must agree on compatible parameters and why successful tunnel establishment does not automatically guarantee that the desired traffic is routed and permitted through the tunnel.
Troubleshooting benefits from separating phases. First confirm peer reachability and negotiation, then verify security associations, interesting traffic or policy matching, routes, NAT interactions, and return paths. A tunnel can be “up” while application traffic still fails because the protected networks are defined incorrectly.
Authentication links network access to a user or device identity
Security systems commonly integrate local accounts, directory services, AAA platforms, certificates, or other identity sources. Authentication proves an identity, while authorization determines what that identity may do. Keeping those functions distinct makes policy easier to design and audit.
Single sign-on and centralized identity can improve user experience and policy consistency, but they also create dependencies. If the directory, time service, certificate chain, or communication path fails, security devices may lose identity context. Operators should know the fallback behavior before an outage occurs.
Cryptography and PKI depend on correct key, certificate, and trust management
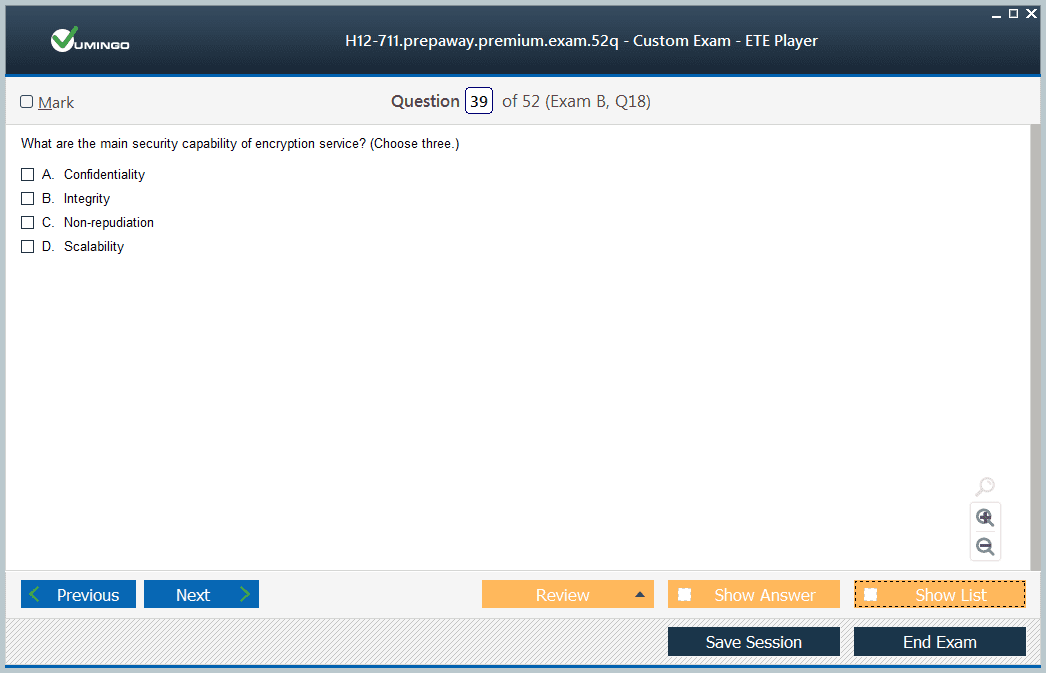
Encryption protects confidentiality, hashing supports integrity checks, and asymmetric cryptography enables functions such as digital signatures and key establishment. Public key infrastructure adds certificates and trust chains so systems can validate identities at scale. The algorithms matter, but operational management is often where real failures occur.
Expired certificates, incorrect names, untrusted issuers, weak private-key protection, and unsynchronized clocks can break secure services unexpectedly. Security engineers should track certificate lifecycles and know which systems depend on each trust chain. Replacing a certificate without understanding those dependencies can interrupt VPNs, portals, or management services.
Intrusion prevention and attack defense require context, tuning, and evidence
Network security devices can inspect traffic for known attack patterns or abnormal behavior, but detection systems operate with imperfect information. Aggressive signatures may block legitimate traffic, while loose policies may allow attacks through. Tuning should be based on observed environment, application criticality, and the organization’s tolerance for false positives.
Alerts also need an investigation workflow. Operators should correlate source, destination, time, session information, endpoint evidence, and application context before concluding what happened. A security device can identify suspicious behavior, but incident response still requires validation and containment across multiple systems.
Secure operations include logging, monitoring, backups, and controlled administration
Security appliances are themselves critical infrastructure. Administrative access should be restricted, configuration changes logged, backups protected, and software maintained. Monitoring should include system health as well as security events because a saturated CPU, full log partition, or failed interface can reduce protection without producing an obvious attack alert.
Operational teams also need a recovery path. Document how to regain access after a bad policy change, how to restore configuration, and how to isolate a compromised device. Change windows and peer review are especially valuable for security infrastructure because one incorrect rule can affect a large portion of the network.
Legacy H12-711 concepts remain useful when mapped to the current HCIA-Security model
The old HCNA-Security-CBSN material introduced the foundations of secure network construction. Huawei later expanded the associate security curriculum to cover broader information-security concepts, host security, network security, cryptography, and security operations. The modern H12-711_V4.0 page is therefore the better reference for current exam planning. Learners moving beyond the associate layer can also place that foundation in the professional progression represented by HCIP-Security V4.0.
The transition also reflects how the role has changed. A modern network security engineer is expected to understand identity, endpoint and host context, encrypted traffic, monitoring, incident response, and evolving threats in addition to classic firewall and VPN configuration.
Migration from the legacy HCNA-Security era should be handled as a mapping exercise rather than a direct blueprint substitution. Firewall policy logic, VPN fundamentals, authentication, cryptography, attack defense, logging, and secure administration remain useful concepts, but current products and threats require updated implementation guidance. Candidates can keep the conceptual model while replacing old command examples and exam-process assumptions with current HCIA-Security material.
Security troubleshooting should preserve evidence before configuration is changed. Session tables, logs, policy-match information, authentication records, VPN negotiation state, routing, and packet captures can show whether a connection was denied, misrouted, untranslated, or cryptographically rejected. Randomly loosening rules may restore connectivity while hiding the actual problem and creating a larger security exposure.
Policy review is another durable skill. Rules should have an identifiable business purpose, specific sources and destinations where practical, appropriate services, logging where needed, and an owner or lifecycle process. Over time, temporary exceptions can become permanent and broad rules can accumulate. Even when the exam version changes, the ability to reason about least privilege, rule order, dependencies, and controlled change remains central to secure network operations.
Segmentation gives security policy a structure that is easier to reason about than a flat network with many exceptions. User, server, management, guest, and other trust zones can have different allowed flows, and those flows can be reviewed against business purpose. The important point is not the number of zones but the clarity of the boundaries. A security engineer should be able to explain why traffic crosses a boundary, which control authorizes it, what evidence is logged, and how the path changes during a failure or maintenance event.
Administrative access deserves the same discipline as user traffic. Device management should use trusted paths, strong authentication, appropriate privilege separation, and logging that makes changes attributable. Backup and recovery procedures should also be tested so that a security device can be restored without reintroducing obsolete policy or credentials. These operational controls may appear less dramatic than attack-defense features, but they determine whether the security infrastructure itself can be managed safely during routine work and during an incident.
Rule changes should be validated from both security and service perspectives. A policy can restore application connectivity while unintentionally permitting more traffic than intended, or it can appear restrictive while a different path bypasses the control. Engineers should test the exact allowed flow, representative denied flows, logging, and return traffic after a change. This develops a habit that remains relevant across firewall generations: success is not simply “the application works,” but “the required application works through the intended policy while unrelated access remains constrained and observable.”
Study the H12-711 legacy page as history, but verify every current control against modern guidance
Historical labs can still teach packet flow, zone policy, NAT, VPN negotiation, authentication, and troubleshooting. Those are durable skills. The risk comes from assuming that old default settings, cryptographic choices, software behavior, or exam objectives remain appropriate years later.
A sensible workflow is to use legacy scenarios to practice reasoning, then confirm current configuration and security recommendations in Huawei’s latest documentation and certification materials. That preserves the educational value of H12-711 without presenting an older HCNA-era exam as the certification path candidates should follow now.
Why customers love us?
What do our customers say?
The resources provided for the Huawei certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the H12-711 test and passed with ease.
Studying for the Huawei certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the H12-711 exam on my first try!
I was impressed with the quality of the H12-711 preparation materials for the Huawei certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The H12-711 materials for the Huawei certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the H12-711 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my Huawei certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for H12-711. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the H12-711 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my H12-711 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my Huawei certification without these amazing tools!
The materials provided for the H12-711 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed H12-711 successfully. It was a game-changer for my career in IT!


