CBDE Certification Exam: Current Ethereum Developer Skills and BTA Exam Format
The Certified Blockchain Developer - Ethereum (CBDE) is a current Blockchain Training Alliance credential for developers who build and deploy applications on Ethereum. BTA currently lists the exam as 70 questions in 90 minutes, delivered online through the BTA student portal, with a 70% passing score. The exam is aimed at software engineers, programmers, developers, and application architects, and its published skills emphasize production-ready Ethereum applications, Solidity smart contracts, testing, deployment, gas costs, Web3 tooling, and development-node workflows.
CBDE belongs to the broader Blockchain Training Alliance certification portfolio. Candidates who need business fundamentals before coding can build context with Certified Blockchain Business Foundations, while architecture-focused professionals can compare their responsibilities with the Certified Blockchain Solutions Architect path. The developer exam should be studied as an implementation credential, not as a generic cryptocurrency quiz.
Ethereum development begins with state, transactions, and execution
An Ethereum application ultimately changes blockchain state through transactions. Externally owned accounts sign transactions with private keys, while smart-contract accounts execute code when invoked. Transactions consume gas, can succeed or revert, and are ordered into blocks by the network. Candidates should understand the difference between reading state and submitting a state-changing transaction because the security, latency, and cost implications are different.
Study examples should follow a transaction from the user interface through a provider to the network, then into contract execution and an updated state. This exposes practical questions: which account signs, what data is encoded, how gas is estimated, what happens if the call reverts, and how the application learns that the transaction was included. Memorizing Solidity syntax without this lifecycle leaves a gap between code and production behavior.
Solidity fundamentals need to be connected to contract design
CBDE preparation should cover Solidity data types, functions, visibility, state variables, mappings, arrays, structs, events, modifiers, inheritance, interfaces, and error-handling patterns at the level needed to read and reason about contract code. The important skill is not recalling every keyword from memory. It is recognizing how storage choices, access rules, function behavior, and external calls affect correctness and security.
Developers should be able to explain why state writes cost more than local computation, why events are useful for off-chain consumers, why visibility and authorization are different concerns, and why a function that compiles can still violate the intended business rules. Short code-review exercises are useful: identify who can call a function, what state can change, what assumptions it makes, and how failure is communicated.
Smart-contract security is part of application design, not a final audit step
Ethereum contracts can control assets or irreversible state, so security mistakes are unusually expensive. Preparation should include reentrancy, incorrect authorization, unsafe external calls, unchecked assumptions about caller or value, arithmetic and precision concerns, denial-of-service conditions, transaction-ordering effects, and misuse of block or timestamp data. Some historical Solidity hazards have changed as the language evolved, but the broader lesson remains: contract behavior must be designed defensively.
Secure development also depends on minimizing privileged powers, documenting trust assumptions, using tested libraries where appropriate, protecting administrative keys, and creating upgrade or pause mechanisms only when governance justifies them. A contract that is technically immutable but operationally impossible to recover can be as risky as one with excessive administrator control. Candidates should reason about the tradeoff rather than assuming that decentralization removes governance.
Gas costs influence both code and user experience
Ethereum charges gas for computation and state changes. Users ultimately care about the total transaction cost and whether the transaction is likely to be included, while developers care about how contract design changes gas consumption. Loops over unbounded data, unnecessary storage writes, oversized transaction payloads, and inefficient state structures can make a design expensive or even impractical.
Preparation should include estimating the operational effect of gas rather than memorizing isolated opcode costs. Ask how often a function will run, who pays, whether work can be moved off chain, what data must remain verifiable, and whether batching or alternative data structures make sense. A production-ready application treats gas as an architectural constraint that affects usability and business feasibility.
Web3 integration connects user applications to the blockchain
BTA’s published CBDE skills include Web3 tooling. In practice, decentralized applications need a provider or node connection, contract addresses and ABIs, account or wallet integration, transaction signing, event handling, and error management. Libraries change over time, so candidates should focus on the enduring interaction model: encode calls correctly, distinguish local reads from signed writes, track transaction status, and avoid exposing private keys in application code.
Front-end and service code must also handle asynchronous blockchain behavior. A submitted transaction is not the same as a confirmed transaction, and a successful submission can later fail during execution. Applications should present pending states clearly, handle replacement or rejection, and reconcile on-chain events with local application data. These are implementation concerns that separate a demo from a reliable system.
Testing should cover contract logic, failure paths, and integration assumptions
Smart-contract tests need more than happy-path examples. Unit tests should exercise authorization failures, boundary values, repeated calls, state transitions, reverts, event emission, and interactions between contracts. Integration tests should run against a representative development or test network and confirm that deployment scripts, account handling, providers, and front-end calls behave as expected.
Developers should also understand why deterministic tests are easier to trust than manual clicking. Automated test suites allow repeated validation after contract or dependency changes. For high-value systems, additional techniques such as static analysis, fuzzing, invariant testing, and independent review can expose classes of problems that ordinary unit cases miss. CBDE preparation benefits from writing small contracts and deliberately breaking them to observe failure behavior.
Deployment is a controlled release process, not just a command
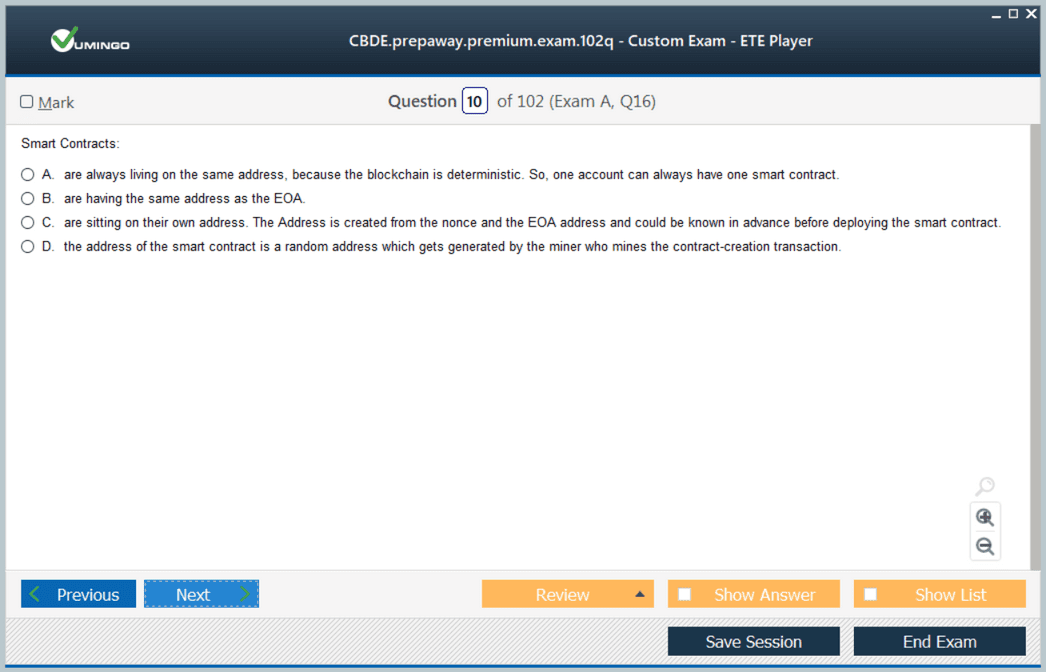
Deploying a contract fixes an address and often establishes long-lived state. A disciplined release process therefore records compiler settings, constructor parameters, library addresses, network IDs, deployment accounts, transaction hashes, and verification data. Teams should know which keys have deployment or administrative authority and whether those permissions need to be transferred to a multisignature or governance mechanism after release.
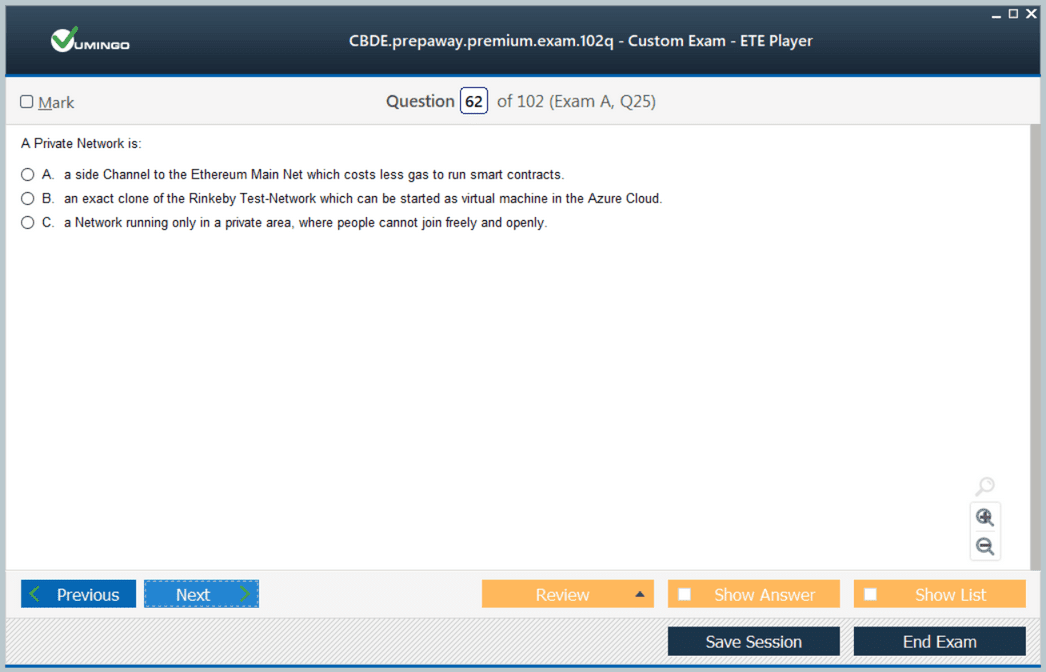
Test-network deployment is valuable because it exercises the same external interfaces without exposing production assets. It can reveal RPC differences, gas-estimation issues, event-handling bugs, or assumptions about network timing. Candidates should understand the role of local development chains, public test networks, and the live network rather than treating deployment as a single environment.
Private keys and wallet flows are application security boundaries
A private key should be treated as authorization to act, not as a user identifier. Exposing it in source code, browser storage, logs, support tickets, or build systems can compromise funds and contract privileges. Applications commonly use wallets or signing services so that keys remain outside the application’s direct control. Server-side automation may use managed key stores or hardware-backed protection with strict access policies.
Developers should also anticipate human recovery and operational mistakes. Users can sign the wrong transaction, lose credentials, connect to the wrong network, or interact with an incorrect contract address. Clear transaction previews, network checks, allowance management, role separation, and defensive interface design reduce the chance that a secure contract is undermined by an unsafe surrounding application.
Ethereum changes over time, so distinguish current tooling from enduring concepts
The Ethereum ecosystem evolves quickly. Libraries change APIs, developer frameworks rise and fall, network upgrades modify behavior, and common deployment practices mature. Some older BTA materials may mention tools that were central at the time they were written. Candidates should use the current official CBDE objectives as the authority and understand the concepts behind the tools so that an outdated name does not become a permanent study dependency.
The same caution applies to the historical Certified Blockchain Developer - Hyperledger credential. It illustrates a permissioned enterprise-development path that BTA promoted earlier, but BTA’s current certification catalog no longer lists CBDH. CBDE remains listed as a live certification, so a 2026 study plan should not assume the two developer tracks have identical status.
Preparation should be hands-on and blueprint-driven
BTA provides a CBDE study guide and Ethereum developer training. A practical study plan should turn each objective into a build task: create a contract, compile it, deploy locally, write tests, connect through a Web3 library, submit transactions, observe events, estimate gas, and diagnose an intentional failure. Short projects force concepts to interact and expose gaps that passive reading can hide.
The online exam provides immediate pass/fail reporting through BTA, and BTA states that a failed attempt requires a new voucher and at least a 48-hour wait. Candidates who pass cannot retake the same exam version within 12 months. That policy makes targeted preparation worthwhile. The best readiness check is whether the candidate can explain and debug a complete Ethereum application path—from key and transaction through Solidity execution to testing, deployment, monitoring, and user-facing behavior—without relying on memorized buzzwords.
Developers should also understand contract interfaces and dependency risk. A decentralized application may call external contracts, libraries, price feeds, token standards, or infrastructure providers maintained by other teams. Before relying on a dependency, identify what can change, whether the address or interface is upgradeable, how failure is surfaced, and what assumptions the calling contract makes about return data or side effects. Production readiness includes reducing hidden dependencies and monitoring the ones that cannot be removed.
Finally, practice reading transactions and receipts rather than treating the blockchain as a black box. Logs, event topics, revert data, gas usage, sender, recipient, value, and block information can explain what happened when an application behaves unexpectedly. A developer who can interpret this evidence can distinguish a front-end problem from an RPC failure, rejected signature, reverted contract call, or confirmation delay. That diagnostic skill makes hands-on preparation much more durable than rehearsing one framework’s commands.







 83% students found the test questions almost same




