
- Home
- Checkpoint Certifications
- 156-215.80 Check Point Certified Security Administrator (CCSA R80) Dumps
Pass Checkpoint 156-215.80 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!


156-215.80 Premium Bundle
- Premium File 536 Questions & Answers. Last update: Oct 30, 2026
- Training Course 48 Video Lectures




Last Week Results!
 83% students found the test questions almost same

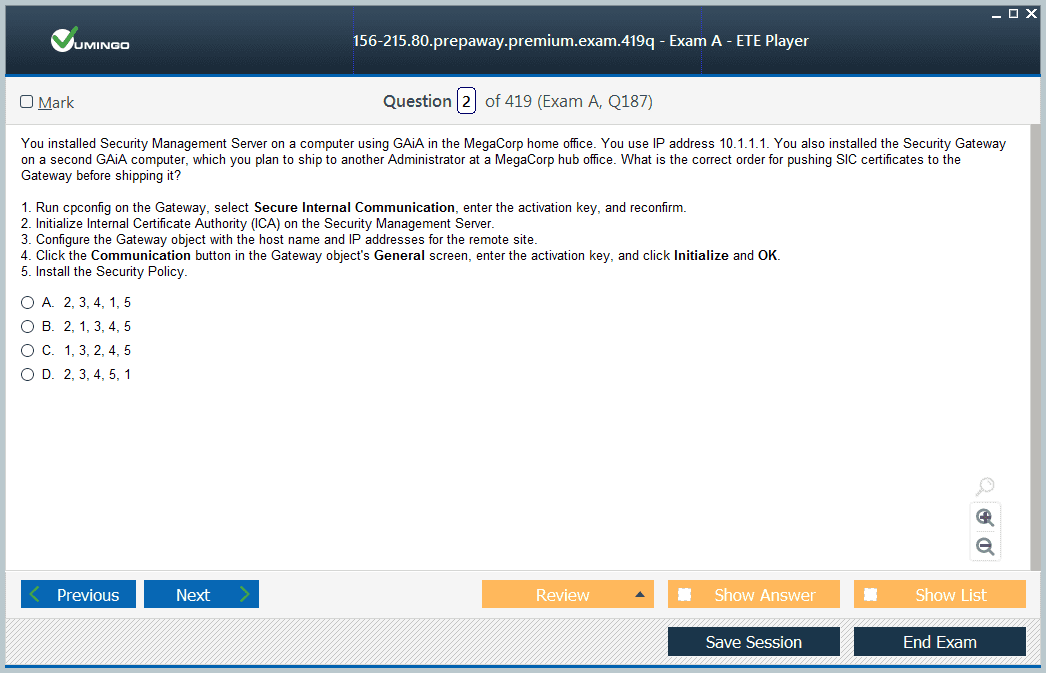
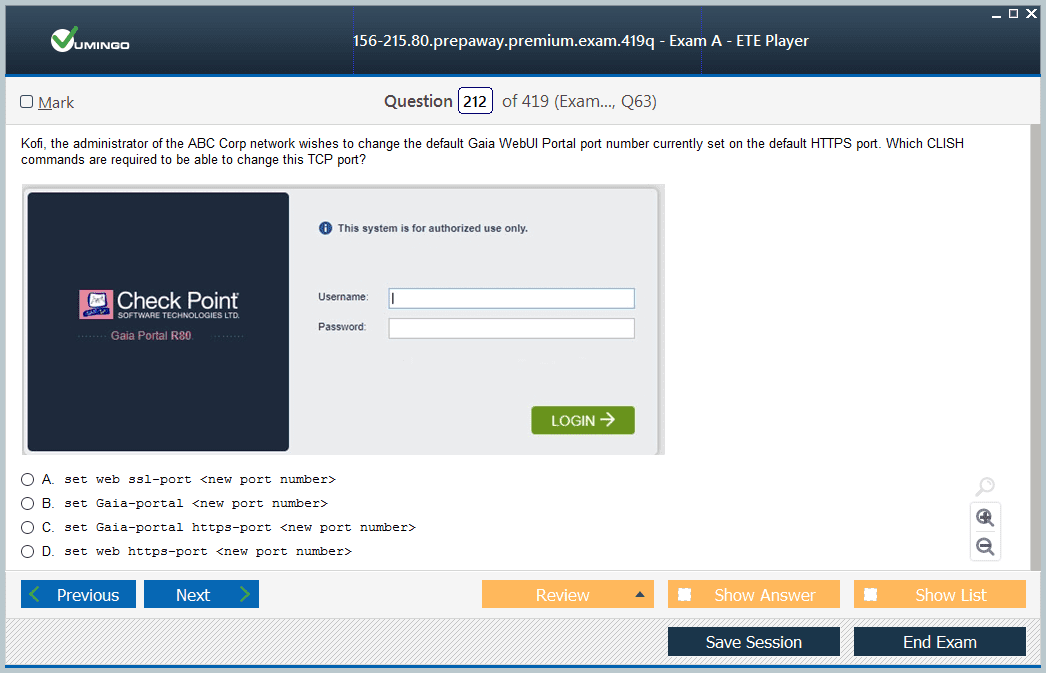
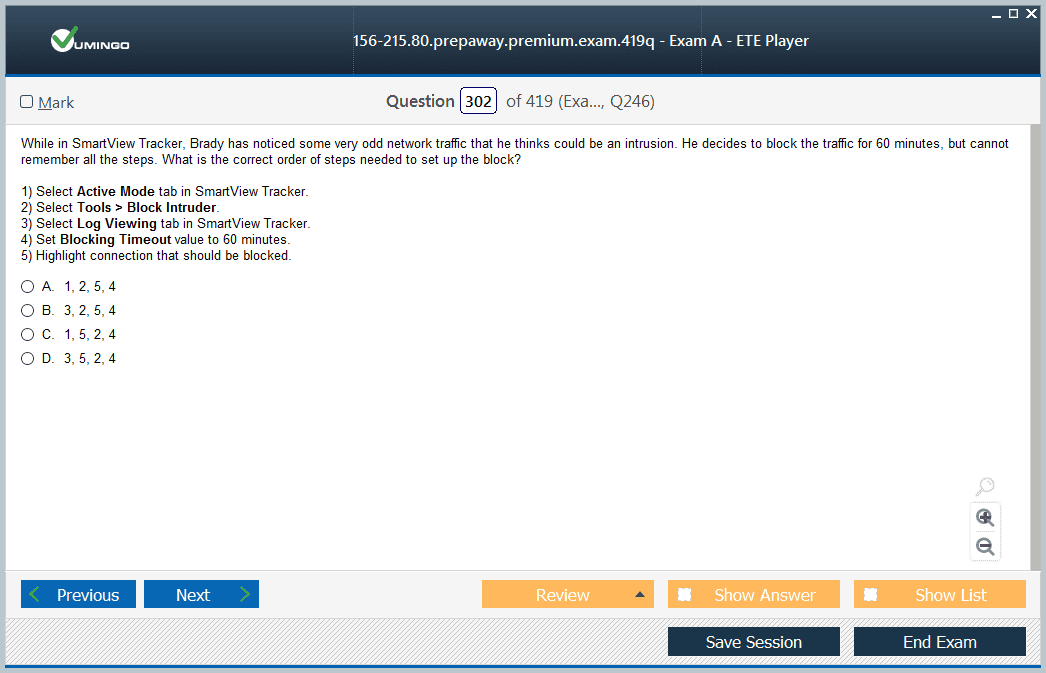
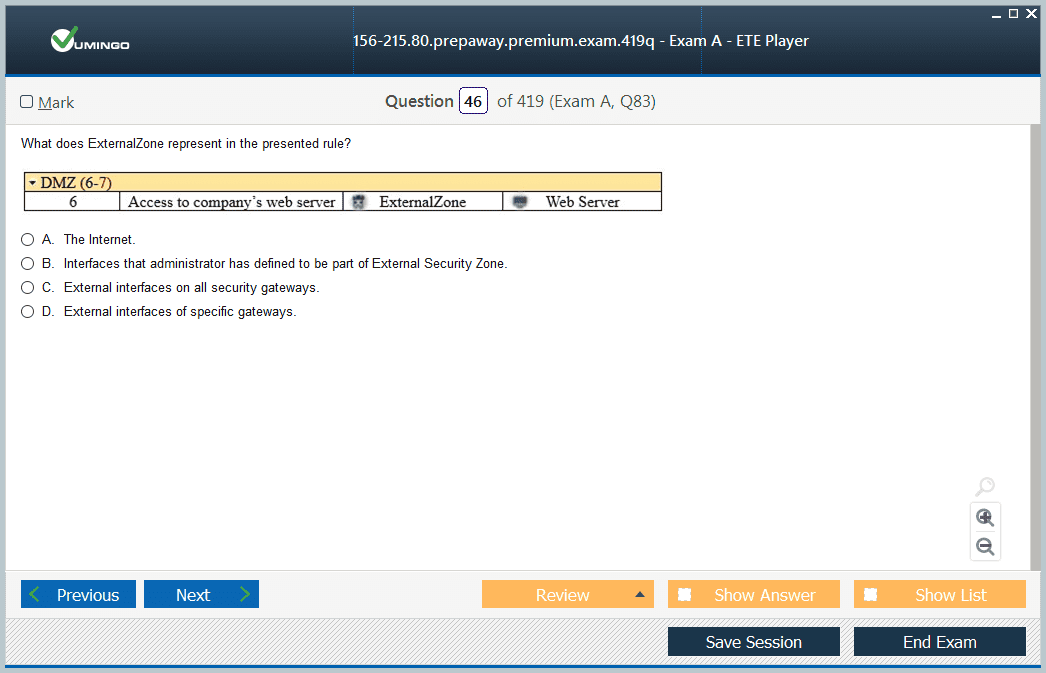
Includes question types found on the actual exam such as drag and drop, simulation, type-in and fill-in-the-blank.

Based on real-life scenarios similar to those encountered in the exam, allowing you to learn by working with real equipment.
156-215.80 CCSA R80: Legacy Administration Skills and the Road to R82
156-215.80 is the legacy Check Point Certified Security Administrator R80 exam. R80 was a major generation in the Check Point management platform, and the exam validated day-to-day administration skills for Security Gateways and management software in that era. The exam is no longer the current CCSA target. Check Point’s 2026 certification materials identify 156-215.82 as the live R82 administrator exam, so candidates finding an old R80 requirement or study guide should distinguish historical platform knowledge from current certification preparation.
The R80 material still explains concepts that persist in modern environments: centralized object management, policy layers, administrator sessions, Gaia system administration, NAT, VPN context, logging, and the relationship between management and enforcement. The CCSA R80 certification page is useful historical context, while the broader Check Point certifications inventory shows that the vendor’s current core path has advanced to R82.
R80 moved administration toward unified SmartConsole management
One of the defining operational shifts in the R80 family was a more unified management experience. SmartConsole brought objects, policies, logs, events, and administrative workflows together around the Security Management Server. Candidates needed to understand that configuration was not simply edited on a firewall device. Administrators changed a managed policy and object database, published those changes, and installed policy to enforcement points.
That workflow introduced important collaboration concepts. Multiple administrators could work concurrently, but sessions, changes, publication, and policy installation still required discipline. A team needed to know which changes were private to a session, which had been published, and which policy package was actually installed on a gateway. The same operational principle remains valuable today: configuration state in a management interface is not useful until you understand when and where it becomes effective.
Gaia administration and management architecture underpin daily operations
Check Point gateways and management servers rely on Gaia, so administrators need a working model of interfaces, routing, DNS, time, administrator access, backups, software state, and basic command-line versus web-portal responsibilities. R80-era preparation also required knowing the difference between the Security Management Server, managed gateways, logging functions, and SmartConsole clients. Troubleshooting starts by identifying which component owns the failed function.
System hygiene matters because policy behavior depends on healthy infrastructure. Incorrect routing can look like a firewall rule problem. Time drift can damage logging and authentication. A full filesystem can affect management services. An administrator who understands only the rule base may miss the actual cause. Build study scenarios that include both policy and platform state so the security product is treated as an operating system plus management architecture, not a static access-control list.
Operational discipline matters as much as navigation. Before installing a hotfix, changing routing, or altering an interface, an administrator should capture the current state, confirm a viable backup or snapshot, understand the maintenance impact, and define a validation plan. After the change, check gateway health, management connectivity, policy installation, logging, and representative business flows. These habits are version-independent even though the exact tools and menus have changed since R80.
Object design determines whether policy remains understandable
Objects represent hosts, networks, groups, services, gateways, users, and other logical entities used by policy. Good object design reduces duplication and makes intent visible. Poor design creates overlapping groups, misleading names, and brittle rules that are difficult to review. Candidates should understand how an object’s properties affect matching and why changing a widely reused object can alter behavior in many policy locations at once.
The key administrative skill is translating business requirements into reusable objects. If several offices need the same service set, model that relationship clearly instead of copying many address-and-port combinations. If a group mixes resources with different risk levels, separate them before exceptions accumulate. Policy maintenance is easier when objects tell the story of the network rather than merely satisfying the syntax of one rule.
Access Control policy layers changed how rules were organized
R80 emphasized a layered Access Control model. Administrators had to understand rule order, matching, cleanup behavior, and the distinction between layer structures such as ordered layers and inline layers. A connection can be accepted by one part of a policy and still require evaluation in another layer depending on the design. That makes policy reasoning more sophisticated than scanning a flat list from top to bottom.
Preparation should include tracing representative traffic. Write source, destination, service, identity or application context, and expected action, then walk through the relevant layers in sequence. Ask which rule should match and what log entry should be produced. This method is more reliable than memorizing screenshots because it tests the actual decision model. It also prepares candidates to diagnose shadowed rules, overly broad exceptions, and cleanup rules that hide missing requirements.
R80 also made change governance more visible because an administrator could work inside a management session, review changes, publish them, and then install policy. That sequence should encourage deliberate peer review rather than rapid editing in production. A good policy request names the business owner, source, destination, service or application, time requirement, logging expectation, and planned review or expiration. Rules created without that context become difficult to defend months later.
Anti-spoofing and interface topology should be reviewed alongside policy because a rule can look correct while the gateway still rejects traffic based on where an address appears. When troubleshooting, do not assume every drop is caused by the rulebase. Confirm routing, interface topology, NAT, anti-spoofing, and the policy layer that actually matched. R80 study is most useful when it builds this packet-path habit rather than memorizing where a particular checkbox used to appear.
NAT and network topology shape packet processing
Network Address Translation is not merely a cosmetic address change. Static, hide, and manual translation choices interact with routing, anti-spoofing, service exposure, and troubleshooting. Candidates should be able to explain why translation is required, which side of a connection sees which address, and how return traffic finds the correct path. Proxy ARP and manual NAT scenarios are especially useful because they expose hidden assumptions about layer-2 reachability and gateway ownership.
Topology awareness is equally important. A gateway must know which interfaces are internal, external, or connected to specific networks so anti-spoofing and VPN behavior make sense. When traffic fails, draw the packet path and note the address at each stage. This keeps troubleshooting grounded in observable transformations instead of repeatedly changing rules in the hope that one change will work.
Identity Awareness joins users to traffic and policy
IP addresses do not always provide enough context for access decisions. Identity Awareness lets policy incorporate users and access roles so that the same network location can receive different treatment depending on who is authenticated. Administrators need to understand the purpose of identity sources, user-to-IP association, and role-based policy, as well as the operational risk when identity information is stale or unavailable.
A useful study exercise is to compare an address-only rule with an identity-aware rule. Ask how the gateway learns the user, how long the association lasts, what happens with shared devices, and how logs support investigation. The important principle is that adding identity improves context but also adds dependencies. Authentication infrastructure, collectors, and user-directory data become part of the policy path.
Logging, monitoring, and troubleshooting turn rules into operations
A policy is not proven merely because it installs without error. Administrators need logs and status information to confirm that expected traffic is allowed, unwanted traffic is blocked, and gateway resources remain healthy. Learn to filter logs by source, destination, service, action, blade, and time, then correlate the result with the rule that should have matched. Unexpected silence is a clue too: if a connection produces no expected record, traffic may not have reached the intended gateway or logging may be misconfigured.
Troubleshooting should move from broad to specific. Confirm link and routing state, confirm policy installation, reproduce the traffic, examine logs, verify NAT and topology, and only then consider deeper packet or kernel analysis. This order reduces unnecessary changes. The same operational discipline applies to modern R82 even though interfaces, features, and best practices have evolved since R80.
VPN and threat-prevention context complete the administrator picture
CCSA administrators also need enough VPN and threat-prevention context to understand how gateway policy affects encrypted or inspected traffic. Site-to-site VPN uses gateway identities, VPN domains, IKE negotiation, and IPsec to create encrypted communication between protected networks. Threat-prevention blades add another inspection decision after basic connectivity has been allowed. The administrator must therefore distinguish “the firewall permits the flow†from “the complete security stack permits the flow.â€
Study these features through dependencies. VPN troubleshooting begins with reachability, certificates or authentication, domain definitions, proposals, and logs. Threat-prevention troubleshooting requires knowing which profile or policy is applied, whether inspection is enabled, and what the logs say about the detected object. Keeping the layers separate makes complex behavior easier to reason about.
Study R80 historically, but use R82 for current certification decisions
If you are maintaining an R80-era environment, the 156-215.80 topics can still help you understand the architecture you inherited. If you are pursuing a certification now, however, do not study R80 as though it were the active exam. The later 156-215.81.20 CCSA R81.20 exam has itself retired, and Check Point now publishes R82 course and exam-prep material.
The current 156-215.82 CCSA R82 exam validates the same broad administrator mission against the current platform, including R82-era object and policy management, Identity Awareness, HTTPS Inspection, application and URL control, Autonomous Threat Prevention, and monitoring. Use R80 knowledge to understand continuity, but base booking decisions, labs, and final review on the live exam code and current documentation.
Purchase Checkpoint 156-215.80 Exam Training Products Individually
Why customers love us?
What do our customers say?
The resources provided for the Checkpoint certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the 156-215.80 test and passed with ease.
Studying for the Checkpoint certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the 156-215.80 exam on my first try!
I was impressed with the quality of the 156-215.80 preparation materials for the Checkpoint certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The 156-215.80 materials for the Checkpoint certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the 156-215.80 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my Checkpoint certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for 156-215.80. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the 156-215.80 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my 156-215.80 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my Checkpoint certification without these amazing tools!
The materials provided for the 156-215.80 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed 156-215.80 successfully. It was a game-changer for my career in IT!


