Pass ISC-CCSP Certification Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!
CCSP Premium Bundle
- Premium File 512 Questions & Answers. Last update: Oct 30, 2026
- Training Course 43 Video Lectures
- Study Guide 571 Pages
CCSP Premium Bundle
- Premium File 512 Questions & Answers
Last update: Oct 30, 2026 - Training Course 43 Video Lectures
- Study Guide 571 Pages
Purchase Individually

Premium File
Training Course
Study Guide
CCSP Exam - Certified Cloud Security Professional (CCSP)
| Download Free CCSP Exam Questions |
|---|
ISC ISC-CCSP Certification Practice Test Questions and Answers, ISC ISC-CCSP Certification Exam Dumps
All ISC ISC-CCSP certification exam dumps, study guide, training courses are prepared by industry experts. ISC ISC-CCSP certification practice test questions and answers, exam dumps, study guide and training courses help candidates to study and pass hassle-free!
ISC2 CCSP in 2026: New August Exam Outline, Cloud Security Domains, and Experience Requirements
The ISC2 Certified Cloud Security Professional (CCSP) validates advanced knowledge of cloud architecture, data security, infrastructure security, application security, operations, and legal/risk/compliance requirements. A new CCSP exam outline took effect on August 1, 2026, so candidates preparing now should retire older domain-weight assumptions and align every resource to the current version.
The current CCSP exam uses Computerized Adaptive Testing, runs three hours, and contains 100–150 multiple-choice and advanced item types. The passing grade remains 700 out of 1000. The broader ISC2 certifications family includes CISSP, but CCSP goes deeper into cloud-specific responsibility, architecture, data, platform, application, operations, and regulatory considerations.
Use the New August 2026 Domain Weighting
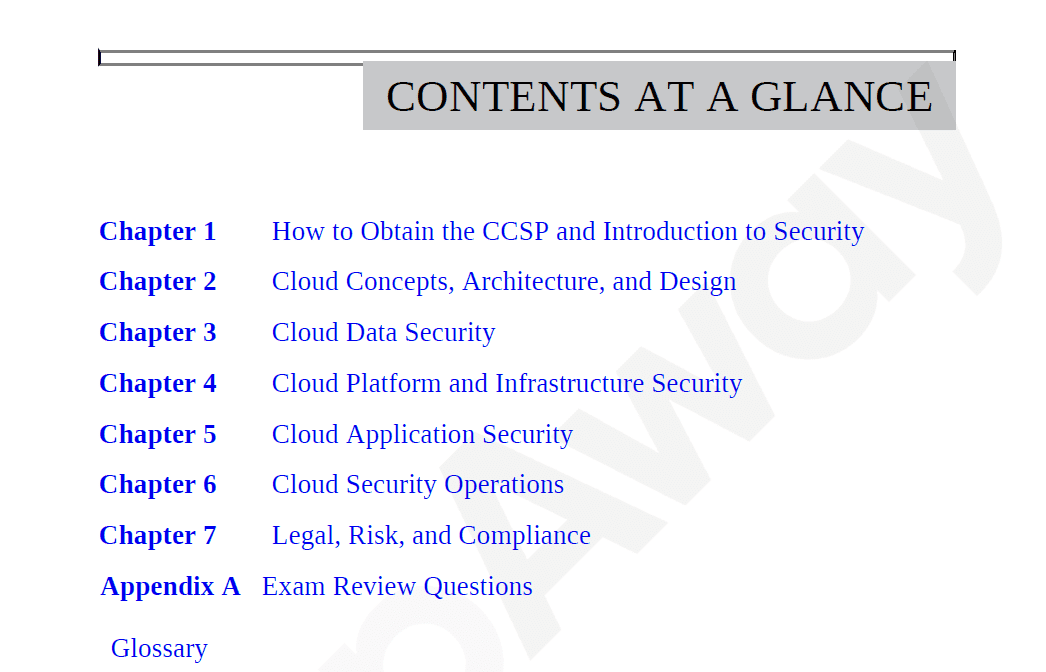
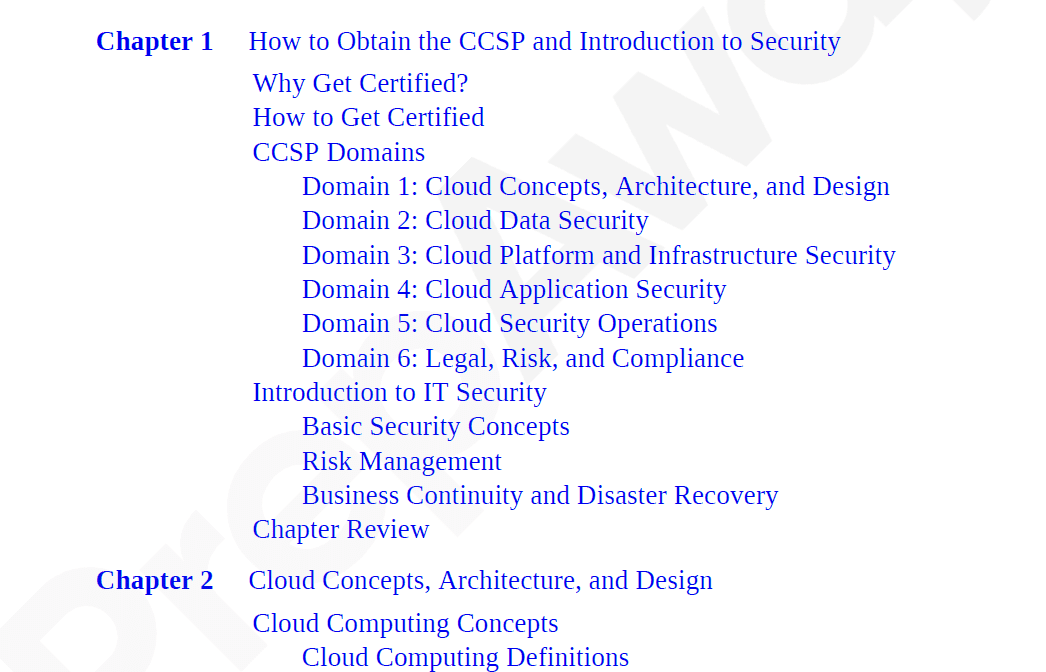
The current CCSP outline uses six domains: Cloud Concepts, Architecture and Design (17%); Cloud Data Security (20%); Cloud Platform and Infrastructure Security (17%); Cloud Application Security (16%); Cloud Security Operations (17%); and Legal, Risk and Compliance (13%).
Data security is now the largest single domain, but the exam remains deliberately balanced. A cloud security professional needs to understand how data, identity, networks, applications, providers, operations, and law interact across service models.
Shared Responsibility Is the Starting Point
Cloud security decisions depend on which party controls physical infrastructure, virtualization, operating systems, applications, identity, data, configuration, and monitoring. Responsibility shifts across IaaS, PaaS, SaaS, and managed services.
Practise mapping responsibilities for a real workload. Avoid vague statements such as “the provider handles security.†The provider secures some layers, while the customer usually retains important identity, configuration, data, and usage responsibilities.
Architecture Should Make Trust Boundaries Explicit
Cloud architecture includes service models, deployment models, virtualization, containers, networks, identity, resilience, management planes, and secure design. The PrepAway path on CCSP cloud security can help organize the breadth.
Draw data flows between users, APIs, workloads, storage, providers, and third parties. Mark where encryption, authentication, authorization, inspection, logging, and administrative access occur. Trust boundaries become much easier to evaluate when they are visible.
Cloud Data Security Requires Lifecycle Thinking
The current weighting emphasizes data security. Understand classification, ownership, discovery, storage, access, encryption, key management, retention, deletion, privacy, backup, and data-loss prevention across cloud services.
The PrepAway article on cloud data security can reinforce these relationships. Remember that copies, snapshots, logs, exports, caches, and test environments can expose the same sensitive data as the primary production store.
Platform and Infrastructure Security Include Cloud-Native Controls
Review compute, virtual networks, segmentation, security groups or equivalent controls, management interfaces, containers, infrastructure as code, vulnerability management, and workload hardening. Cloud platforms are highly automated, which makes both good and bad configuration scale quickly.
Protect machine identities and automation credentials as carefully as administrator passwords. A compromised service principal with broad permissions can have a much larger blast radius than one user account.
Cloud Application Security Connects Development and Operations
Cloud applications rely on APIs, CI/CD, secrets, dependencies, containers, managed runtimes, serverless services, and third-party components. Security should be included in design, development, testing, deployment, and monitoring rather than added after release.
Practise evaluating common design issues such as exposed storage, insecure APIs, excessive application permissions, unreviewed dependencies, and hard-coded secrets. The cloud provider may secure the runtime while the customer still owns vulnerable application logic.
Operations Require Visibility and Recoverability
Cloud security operations include monitoring, logging, configuration, incident management, forensic readiness, continuity, recovery, infrastructure maintenance, and change control. The PrepAway career path on cloud security operations provides context for day-to-day responsibilities.
Plan evidence collection before incidents occur. Cloud resources can be ephemeral, and provider logs may have limited retention unless configured. Recovery also needs testing: backups, multi-region strategies, and infrastructure templates should be proven rather than assumed.
Legal, Risk, and Compliance Depend on Provider and Data Context
Cloud contracts, data location, privacy, audit rights, service-level agreements, eDiscovery, certifications, and third-party risk all affect cloud security. The customer remains responsible for understanding which assurances the provider offers and which requirements remain unaddressed.
The PrepAway overview of cloud security auditing can help connect provider assurance with customer responsibilities. Compliance evidence should be interpreted in the context of the exact service and configuration being used.
ISC2 currently requires five years of cumulative full-time IT experience, including three years in cybersecurity and one year in one or more CCSP domains. A qualifying degree or CCSK can substitute for one year under the current rules, while an active CISSP can substitute for the full CCSP experience requirement.
Candidates who pass the exam without the required experience may become an Associate of ISC2 and have six years to accumulate the experience. Verify current experience rules before applying because the certification process is separate from passing the exam.
Identity is one of the most important cloud control planes. Federation, MFA, service accounts, workload identity, privileged access, API credentials, and entitlement reviews should be designed across cloud providers and SaaS platforms. Avoid long-lived static credentials where stronger managed identity options exist.
Infrastructure as code changes the security workflow. Network rules, identities, storage, compute, and policy may be deployed through code, which creates opportunities for review and repeatability but also lets one mistake propagate rapidly. Protect repositories, pipelines, secrets, approvals, and state files.
Cloud-native logging should include control-plane events, identity activity, workload logs, network telemetry, security findings, and provider service logs. Centralize enough evidence for investigation while controlling retention cost and sensitive log content. Forensics become difficult when logs disappear before an incident is detected.
Container and serverless environments shift security responsibilities. Teams still need secure images, dependencies, runtime permissions, network controls, secrets, vulnerability management, and logging even when the provider manages more of the underlying infrastructure.
Exit strategy is a cloud-security concern. Organizations should understand how data can be exported, securely deleted, keys revoked, identities removed, integrations dismantled, and regulatory obligations met if a provider changes terms or the organization migrates away.
For final practice, take one SaaS, one PaaS, and one IaaS workload and map the six CCSP domains across each. The contrast makes shared responsibility, data control, platform security, application ownership, operations, and compliance much easier to internalize.
Cloud encryption choices should include who controls keys, how keys are rotated, what services can use them, and what happens during recovery or provider migration. Customer-managed keys may increase control but also increase operational responsibility. Key loss can make securely encrypted data permanently unavailable.
Service-level agreements and contracts should be read alongside technical architecture. Availability commitments, data ownership, incident notification, audit rights, sub-processors, support, and exit terms affect risk. A technically resilient architecture can still create unacceptable business exposure if contractual protections are weak.
For final preparation, design one multi-account or multi-project cloud environment with central identity, logging, networking, data controls, application deployment, incident response, and recovery. Then map every design choice to one or more CCSP domains. This helps prevent the exam from feeling like six unrelated topic lists.
Multi-cloud and hybrid environments add consistency challenges. Security teams need to compare identity, logging, network, key management, configuration, and incident workflows across providers without assuming controls with similar names behave identically. Standard policy should produce equivalent outcomes even when implementation differs.
Before booking, make sure your materials explicitly reference the August 1, 2026 CCSP outline. The change is recent enough that older courses and practice banks may still use the prior weighting and omit updated emphasis.
Cloud governance should also define approved regions, services, account structures, baseline configurations, logging, and exception handling. Guardrails reduce configuration drift while still allowing product teams to move quickly.
Use one final architecture exercise that includes SaaS, PaaS, IaaS, sensitive data, external users, CI/CD, and a third-party provider. Map responsibility, controls, evidence, recovery, and legal obligations across the six current domains.
Cloud cost and security can reinforce one another. Removing unused public resources, stale identities, unattached storage, unnecessary data copies, and overprivileged test environments can reduce both spend and attack surface. Operational reviews should therefore consider security posture and resource efficiency together.
Before the exam, compare one workload deployed as IaaS, PaaS, and SaaS and write how responsibility changes for patching, identity, network, application code, data, logging, backup, incident response, and compliance. This single exercise reinforces the cloud-specific reasoning that separates CCSP from a general security exam.
Review the current ISC2 cloud terminology and August 2026 outline immediately before scheduling so your practice remains aligned to the live exam.
Confirm the live ISC2 exam page before booking.
Keep the August 2026 domain weights visible during final review.
Final Readiness Check
- Use the CCSP exam outline effective August 1, 2026.
- Practise shared responsibility, architecture, data security, platform security, application security, operations, and compliance together.
- Trace cloud data and identities through the full lifecycle and across provider boundaries.
- Design logging, recovery, and incident response before a failure occurs.
- Confirm the current experience pathway, including CISSP and one-year waiver options.
CCSP is most valuable when it turns cloud security from a product checklist into a responsibility model. A strong candidate can explain who owns each control, where the data and trust boundaries are, what evidence proves security is working, and how the environment recovers when something fails.
ISC-CCSP certification practice test questions and answers, training course, study guide are uploaded in ETE files format by real users. Study and pass ISC ISC-CCSP certification exam dumps & practice test questions and answers are the best available resource to help students pass at the first attempt.