
- Home
- ISC Certifications
- CISSP-ISSMP Information Systems Security Management Professional Dumps
Pass ISC CISSP-ISSMP Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!


CISSP-ISSMP Premium File
- Premium File 218 Questions & Answers. Last Update: Nov 13, 2026
Whats Included:
- Latest Questions
- 100% Accurate Answers
- Fast Exam Updates
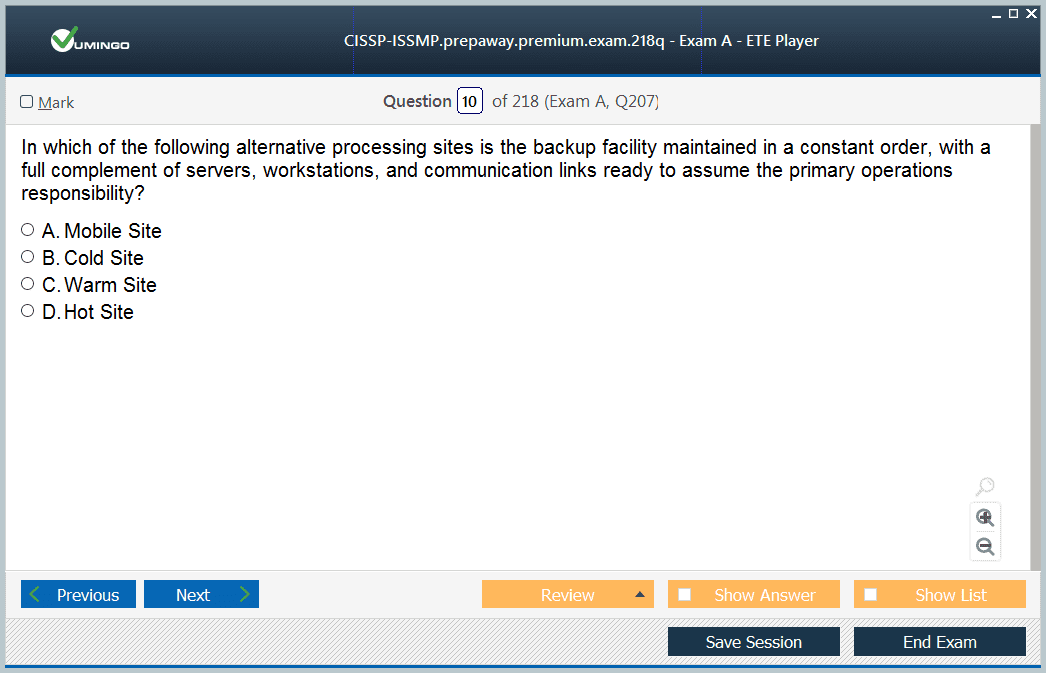
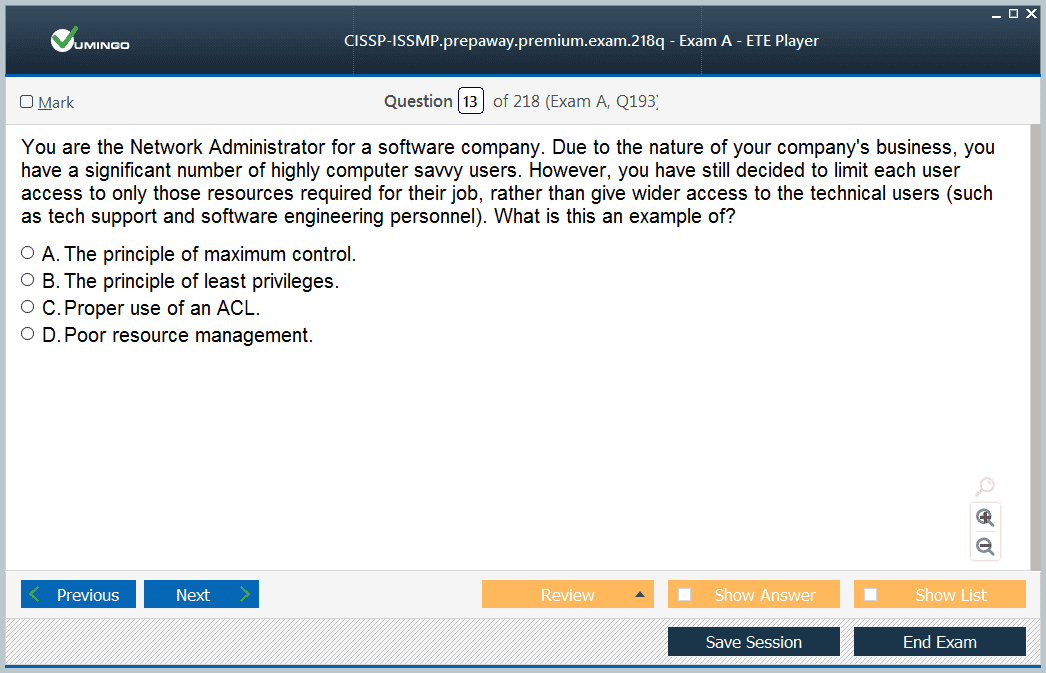
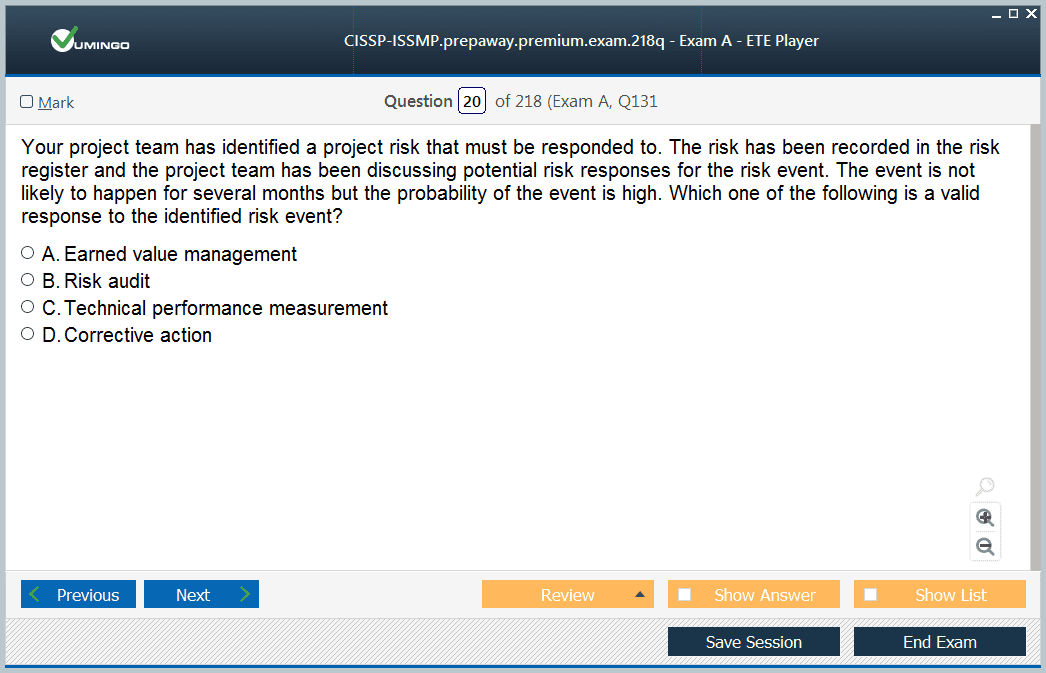
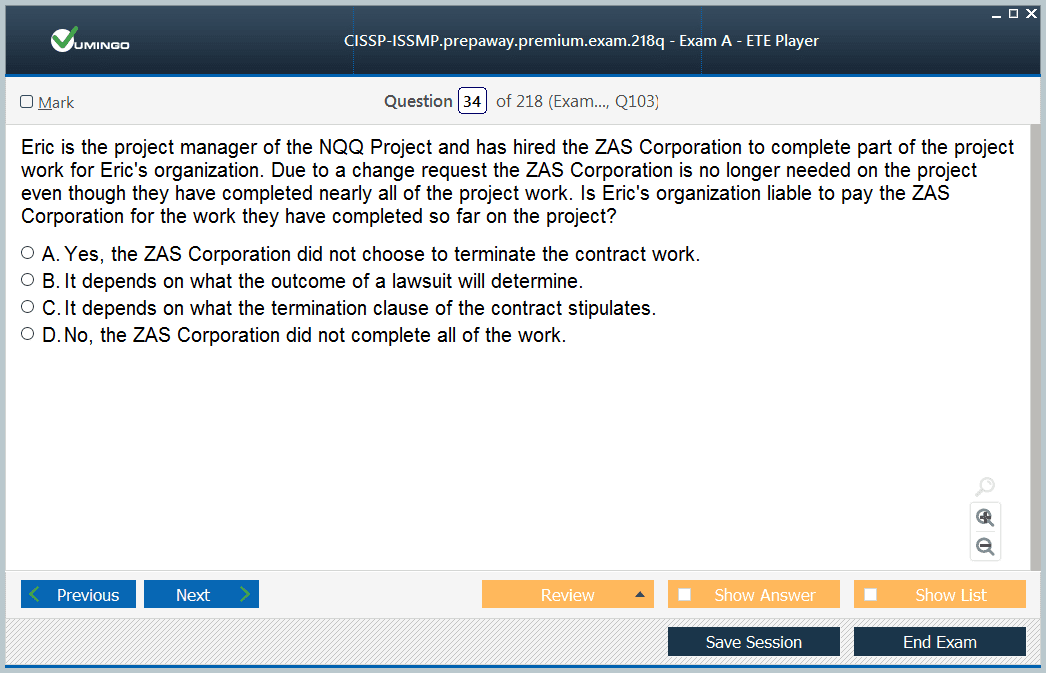
Last Week Results!
 83% students found the test questions almost same
CISSP-ISSMP: Governing Security Programs, Risk, Operations, and Resilience
ISC2’s Information Systems Security Management Professional (ISSMP) is a current advanced credential for professionals who lead information security programs and align them with organizational strategy, risk tolerance, operations, and compliance. The current exam outline took effect on August 1, 2025. The exam contains 125 items, lasts three hours, and requires 700 out of 1000 points. Its six domains are Leadership and Organizational Management at 21 percent, Systems Lifecycle Management at 15 percent, Risk Management at 20 percent, Security Operations at 18 percent, Contingency Management at 12 percent, and Law, Ethics and Security Compliance Management at 14 percent.
ISSMP sits inside ISC2 certifications and the advanced CISSP certification family. Candidates can qualify through an active CISSP plus two years of relevant experience or through ISC2’s alternate seven-year experience route. The credential is aimed at leaders who must make security understandable and governable across business units, technology teams, suppliers, executives, and regulators rather than managing security as an isolated technical function.
Security strategy must connect organizational goals to a defensible risk position
A security program should be able to explain why it exists in business terms. ISSMP candidates need to connect mission, strategy, stakeholder expectations, critical services, data, legal obligations, and risk appetite to security priorities. That means distinguishing objectives from controls. ‘Deploy a new security platform’ is not a strategy; protecting a critical revenue process against a defined class of disruption may be, with technology selected as one part of the treatment.
Leaders also need a governance structure that makes authority visible. Decision rights, escalation paths, risk ownership, policy ownership, funding responsibility, and accountability for exceptions should not depend on informal relationships. Security becomes more sustainable when executives know which decisions require their involvement and operational teams know which decisions they are empowered to make without waiting for crisis approval.
Leadership is measured through influence, communication, and organizational behavior
ISSMP leadership is not limited to managing a security department. Security leaders must build relationships across legal, privacy, finance, audit, engineering, operations, human resources, procurement, and product teams. They often need to persuade rather than command because many controls are implemented by people who do not report to the security organization. The practical distinction between management and leadership matters when a policy is technically correct but organizationally impossible to adopt.
The broader principles in management and leadership apply directly: managers create repeatable processes, while leaders also shape priorities and behavior under uncertainty. Security leaders should tailor communication to the audience, using risk scenarios, operational impact, financial consequence, regulatory exposure, and measurable outcomes instead of relying on technical severity labels alone.
Security metrics should drive decisions rather than create dashboards for their own sake
The current outline expects leaders to define, measure, and report security metrics. Useful metrics are tied to decisions. A vulnerability count may be less useful than the age of high-risk vulnerabilities on critical assets, the percentage of privileged access reviewed on time, recovery tests that meet objectives, or control failures that repeatedly produce incidents. Metrics need context, thresholds, ownership, and trend interpretation.
Key risk indicators and key performance indicators serve different purposes. A performance indicator may show whether a process is operating as designed, while a risk indicator may show that exposure is increasing even when the process is being followed. Mature reporting also explains uncertainty. Security data is often incomplete, so leaders should avoid presenting a precise number as proof of safety when the underlying evidence has significant gaps.
Risk management links enterprise priorities to security treatment choices
Risk management receives 20 percent of the current outline because ISSMP decisions should reflect the organization’s risk context. Leaders need to establish scope, identify assets and dependencies, analyze threats and vulnerabilities, compare treatment options, obtain acceptance where appropriate, and monitor how exposure changes over time. The goal is not to eliminate risk but to make it visible, owned, and consistent with organizational tolerance.
Risk management principles are especially useful when security risk must be integrated with broader enterprise risk. The security function should not maintain a parallel universe of ratings that executives cannot compare with operational, financial, legal, or strategic risks. Common language improves prioritization and helps management understand why one remediation deserves funding ahead of another.
Third-party and supply-chain risk needs continuing governance
Organizations increasingly depend on cloud providers, software vendors, managed services, contractors, processors, and specialized suppliers. Initial due diligence is only the beginning. ISSMP candidates should understand how to define supplier security requirements, evaluate risk before onboarding, include obligations in contracts, monitor meaningful changes, validate critical controls, and plan for termination or provider failure.
The work associated with a vendor risk manager illustrates why supplier risk is an operating discipline rather than a questionnaire. A provider can pass an annual review and still introduce new sub-processors, suffer a breach, change architecture, or stop supporting a critical product. Monitoring should focus on dependencies that can materially affect the organization.
Security operations requires governance of detection, vulnerability, and incident response
ISSMP does not turn a program leader into a SOC analyst, but the leader must ensure operational capabilities have clear objectives, staffing, escalation, tooling, evidence, and connection to risk. Vulnerability management should prioritize based on exposure and business context rather than raw scanner counts. Threat intelligence should become actionable requirements or detection improvements. Security testing should have defined follow-up so findings do not disappear into a backlog.
Incident management needs the same governance discipline. A strong program establishes classification criteria, response roles, legal and communications interfaces, evidence handling, decision authority, and lessons-learned processes before an incident. Operational teams can then act quickly without improvising organizational policy under pressure. Significant incidents should feed back into risk assessments, architecture standards, training, supplier controls, and resilience plans.
Contingency management turns resilience from documentation into tested capability
Business continuity, disaster recovery, crisis communication, and security succession planning all appear in the ISSMP outline because availability and organizational survival are security concerns. A plan is only credible when recovery priorities match business impact, dependencies are understood, responsibilities are assigned, resources are available, and exercises demonstrate that the sequence works. Disaster recovery planning is therefore an evidence problem as much as a documentation problem.
Leaders should also distinguish technical restoration from business recovery. A server may be online while critical data is stale, identities are unavailable, suppliers are unreachable, or downstream processes cannot operate. Scenario exercises expose those hidden dependencies and help teams rehearse the decisions that occur during extended disruption. The objective is not perfect prediction; it is reducing uncertainty and delay when normal assumptions fail.
Law, ethics, privacy, and compliance constrain how the program operates
Security programs operate inside legal jurisdictions, contractual commitments, industry standards, privacy obligations, employment rules, intellectual-property constraints, and professional ethical expectations. ISSMP candidates need to recognize when an issue requires specialist legal advice and how compliance obligations become security requirements. Compliance evidence should demonstrate that controls are operating, not merely that policies exist.
Ethics matters because senior security roles involve privileged information and asymmetric power. Leaders may see employee activity, confidential investigations, vulnerabilities, incident details, and strategic weaknesses. Decisions about monitoring, disclosure, escalation, and evidence handling must respect professional obligations and organizational policy. A technically effective action can still be inappropriate if it ignores legal authority, privacy, proportionality, or due process.
ISSMP is the management concentration, distinct from architecture and engineering
The broader CISSP validates knowledge across eight domains, while the three concentrations emphasize senior specialization. ISSAP focuses on architecture and ISSEP on systems security engineering. ISSMP centers on governance, leadership, risk, lifecycle oversight, operations, resilience, and compliance. The differences are useful because a senior title alone does not reveal where a professional actually spends most of the workday.
Preparation should practice management judgment. Build scenarios where budget is constrained, stakeholders disagree, a supplier creates risk, an incident competes with business priorities, or a compliance requirement conflicts with an existing process. Then decide which stakeholder owns the decision, what evidence is needed, how risk should be communicated, and which action improves the program rather than simply solving the immediate technical symptom.
Budget management is another expression of program strategy. A security leader should be able to distinguish mandatory operating cost from discretionary improvement, identify which capabilities are constrained by staffing rather than tools, and explain what risk changes when funding is reduced. Buying technology because a peer organization uses it is not a defensible investment case. Funding should connect to a capability gap, control objective, operational weakness, regulatory need, or material risk treatment.
Security culture also depends on incentives. If teams are rewarded only for delivery speed, they may treat security reviews as obstacles; if the security team is rewarded only for finding problems, it may have little incentive to make secure delivery easier. ISSMP leaders should look for ways to align objectives, service levels, engineering standards, and exception processes so that responsible security behavior supports rather than competes with business performance.
Program maturity is visible in how the organization handles exceptions. Mature programs do not pretend every standard can be followed in every situation. They require an explicit reason, compensating controls where needed, an accountable risk owner, and a review date. Temporary exceptions that never expire can become permanent hidden architecture, so leaders need a process that makes accumulated exceptions visible and prioritizes the most consequential ones for remediation.
Executive communication is strongest when it distinguishes exposure, action, and decision. A board or senior leader may not need packet-level details from an incident, but they do need to understand business impact, whether the organization is operating within tolerance, what management decision is required, and what uncertainty remains. ISSMP-level reporting should therefore translate technical evidence without hiding material risk. The leader’s credibility depends on being able to say both when a problem is urgent and when a dramatic technical finding does not justify an equally dramatic business response.
Why customers love us?
What do our customers say?
The resources provided for the ISC certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the CISSP-ISSMP test and passed with ease.
Studying for the ISC certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the CISSP-ISSMP exam on my first try!
I was impressed with the quality of the CISSP-ISSMP preparation materials for the ISC certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The CISSP-ISSMP materials for the ISC certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the CISSP-ISSMP exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my ISC certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for CISSP-ISSMP. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the CISSP-ISSMP stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my CISSP-ISSMP certification exam. The support and guidance provided were top-notch. I couldn't have obtained my ISC certification without these amazing tools!
The materials provided for the CISSP-ISSMP were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed CISSP-ISSMP successfully. It was a game-changer for my career in IT!


