Salesforce Sharing and Visibility Designer: Understanding the Legacy Name and Today’s Architect Credential
Salesforce Certified Sharing and Visibility Designer is a legacy credential name. Salesforce announced in December 2021 that Sharing and Visibility Designer was being renamed to Sharing and Visibility Architect as part of a broader effort to distinguish architect credentials from the newer designer role; Salesforce also stated that the exam content was unchanged by that rename. Candidates who encounter this older title should therefore map it to the current Platform Sharing and Visibility Architect credential rather than treat it as a separate modern certification.
The historical name still matters because older study materials, résumés, training references, and archived exam pages continue to use Designer terminology. A candidate can easily mistake that wording for a retired body of knowledge. In reality, the enduring subject is Salesforce security architecture: object and field permissions, record visibility, organization-wide defaults, hierarchy, sharing rules, programmatic sharing, external access, large data volumes, and the trade-offs that connect those controls.
A useful way to study legacy exam material is to preserve the historical context while using current platform language. The objective is not to erase the old name, nor to pretend that every old screenshot remains current. It is to understand which principles survived the rename and then validate product-specific details against today’s Salesforce documentation and certification materials.
The 2021 rename changed the label, not the architectural problem
The older Designer title described professionals who could design secure and scalable sharing models. The modern Architect title makes that responsibility clearer, especially alongside other architecture credentials such as Platform Identity and Access Management Architect and Platform Data Architect. The core skill is still to assess requirements, recommend an appropriate security model, and communicate the operational consequences to technical and business stakeholders.
This continuity is important when using historical study content. Concepts such as private organization-wide defaults, role hierarchy, criteria-based sharing, account teams, territories, Apex sharing, and external-user access remain recognizable. What changes over time are product capabilities, limits, interfaces, naming, and recommended practices. Candidates should keep the conceptual model while refusing to memorize an old user interface as if it were the current exam.
A secure design begins with explicit data sensitivity and actor definitions
Before selecting a Salesforce feature, identify the records and fields that carry business, privacy, financial, or regulated sensitivity. Then define who needs access, for what purpose, and for how long. This is the practical foundation of least privilege. A vague requirement such as “managers need access” is incomplete until the design defines which managers, which records, whether read or edit is required, and what should happen when reporting relationships change.
Legacy scenarios often become easier when rewritten as an access matrix. Place personas on one axis and data categories on the other, then mark object permission, field visibility, and record scope independently. This prevents one broad permission from being used to solve three different requirements. It also reveals where the business has not actually decided its policy, which is a governance problem rather than a configuration problem.
Object relationships and ownership influence every downstream sharing choice
Security design cannot be isolated from the object model. Master-detail relationships, lookup relationships, ownership, parent access, and the way records move through a business process all affect what sharing mechanisms make sense. The principles in data modeling are therefore part of the security conversation. An awkward data model can force equally awkward sharing rules because the system lacks a stable relationship that represents the business meaning of access.
Candidates should ask whether ownership is being used because it reflects responsibility or merely because a sharing rule needs something to key off. If the latter, the model may create reassignment churn and confusing reporting. Good architecture uses durable relationships for durable access, explicit exception mechanisms for exceptions, and clear ownership semantics that other teams can understand without reverse-engineering the security configuration.
Record visibility is not a substitute for permission governance
Sharing rules grant record access; they do not replace object permissions or field-level security. The same separation appears in mature access management: a person’s broad capability to use an object should be governed independently from the subset of records that person needs for a particular role or assignment. Over time, this distinction makes permission sets easier to reason about and record-sharing rules easier to test.
Older materials may emphasize profiles more heavily than current practice. Candidates should translate the enduring idea—users need appropriate object, field, and system permissions—into the contemporary permission model instead of copying an old implementation pattern. The exam rewards understanding the security layers and their interaction, not loyalty to a historical configuration style.
External sharing requires a different set of assumptions
Partner users, customers, and guests do not simply behave like internal employees with fewer permissions. Their license capabilities, account relationships, and available sharing mechanisms can change the design. Experience Cloud work therefore provides useful context; the Experience Cloud Consultant domain shows how identity, customer or partner relationships, sharing sets, roles, and content exposure intersect.
A strong external-access design also considers secondary paths to information. Files, reports, dashboards, search, related records, and automation can disclose information even if the primary record appears protected. Candidates should practice tracing a user journey from login through each surface that reveals data, then verify that the sharing model remains consistent at every step.
Programmatic sharing should have a complete lifecycle
Apex-managed sharing can express relationships that standard sharing rules cannot, but custom code creates responsibilities for testing, removal, error handling, and long-term ownership. Candidates with development experience from the Platform Developer domain should resist treating code as automatically superior. The question is whether programmatic logic represents the business relationship more reliably than declarative mechanisms and whether the organization can support it.
A useful exam-prep test is to describe the full lifecycle of a share: what event creates it, what evidence proves it is correct, what change invalidates it, who or what removes it, and what happens when the process fails midway. If the design only explains creation, it is incomplete. Access that cannot be predictably revoked is a security defect even when the initial grant was legitimate.
Scale changes which sharing patterns remain safe to operate
Large data volumes amplify ownership skew, recalculation cost, locking risk, and the impact of group membership changes. A security model should therefore be reviewed alongside performance and data-growth assumptions. The idea behind row-level security as a data-modeling decision is relevant because access predicates and data structure are connected: a model that requires broad dynamic exceptions can become expensive as records and users multiply.
When evaluating an answer, estimate the frequency of change as well as the number of records. A large but stable sharing pattern may be easier to operate than a smaller model that recalculates constantly. Architects should aim for controls whose behavior can be predicted during acquisitions, reorganizations, territory changes, bulk imports, and other events that put stress on ownership and sharing.
Use old materials for principles and current materials for decisions
The legacy Designer name is useful historical context, but current candidates should organize their final preparation around the active Salesforce certifications and present-day product behavior. Build scenarios that require you to distinguish identity from authorization, object and field permission from record sharing, internal from external access, and declarative from programmatic controls.
For each scenario, defend the option you choose and state why the alternatives are weaker. Explain how the solution is tested, how access is removed, what happens at scale, and what an administrator would need to operate it safely. That reasoning preserves the enduring value of the old Sharing and Visibility Designer material while aligning the study process with the current architect role.
Older certification material can also be valuable for learning the vocabulary of architectural trade-offs. Terms such as implicit sharing, owner-based access, role hierarchy, public groups, territories, and Apex-managed sharing still describe real ideas, even if screenshots and adjacent product names have moved on. When reviewing an old explanation, separate the enduring rule from the historical implementation detail and mark anything that depends on a specific release for verification.
Another useful exercise is to compare two designs that both satisfy the access requirement on day one. Estimate how each behaves when the user population doubles, when ownership changes in bulk, and when a new external audience is introduced. The better architecture is often the one with fewer hidden recalculations and clearer governance, not the one with the shortest setup instructions. This is where the legacy Designer material becomes genuine architect preparation.
Because the credential name changed without a new body of exam content at the time, résumés and historical records may legitimately show either title depending on when the credential was earned. Candidates should avoid presenting the two names as separate achievements. In current study and professional communication, use the active Platform Sharing and Visibility Architect terminology while recognizing Designer references as historical naming for the same security architecture discipline.
Security scenarios also benefit from explicit negative requirements. Write down not only who should gain access, but which users must remain excluded and which indirect routes could undermine that boundary. This changes testing from a confirmation exercise into an attempt to disprove the design. A model that passes only expected-path tests has not yet demonstrated that it protects data under unusual ownership, hierarchy, or sharing conditions.
When older documents use the word Designer, preserve the source context in historical discussion but use Architect for current recommendations. This small editorial discipline prevents readers from assuming a discontinued credential is still separately available. It also mirrors good technical documentation: historical terminology can be retained where it explains migrations, while the active vocabulary should govern new designs, study plans, and career descriptions.



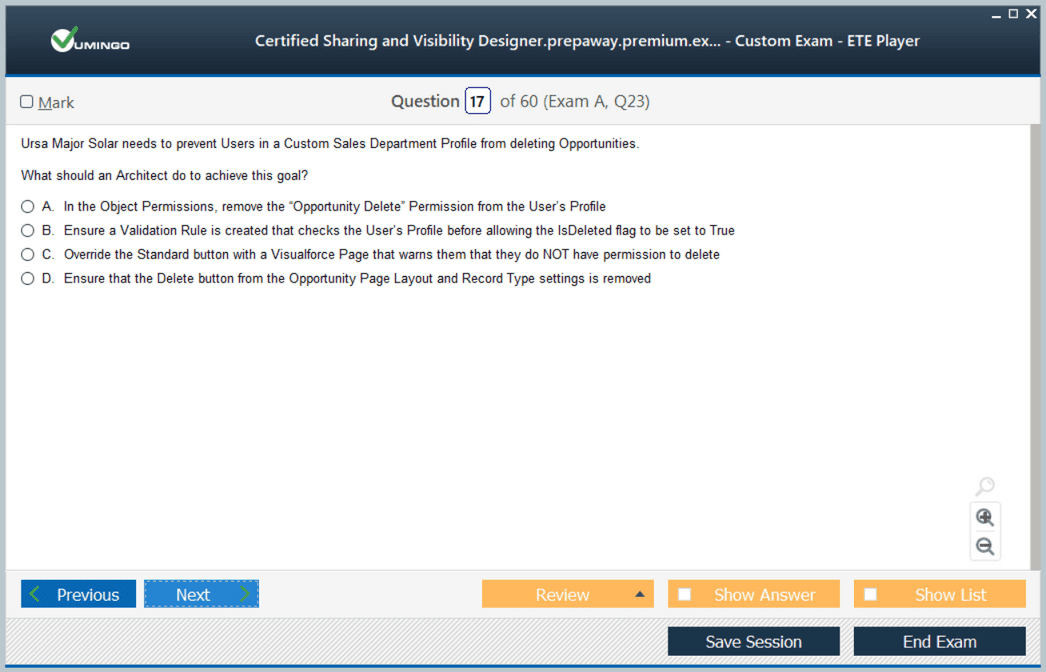
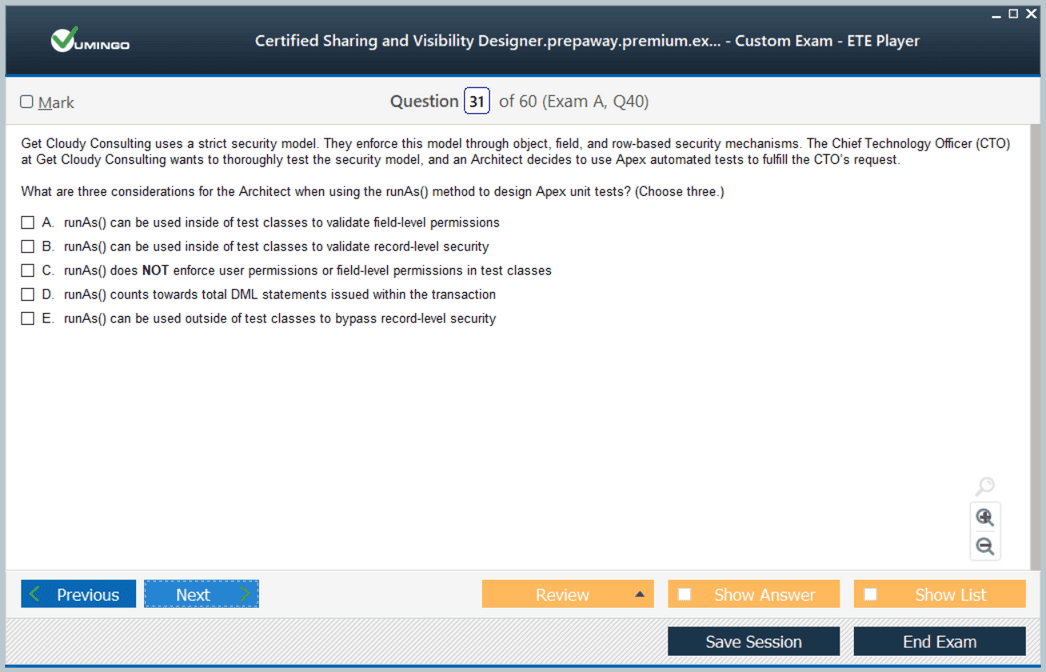
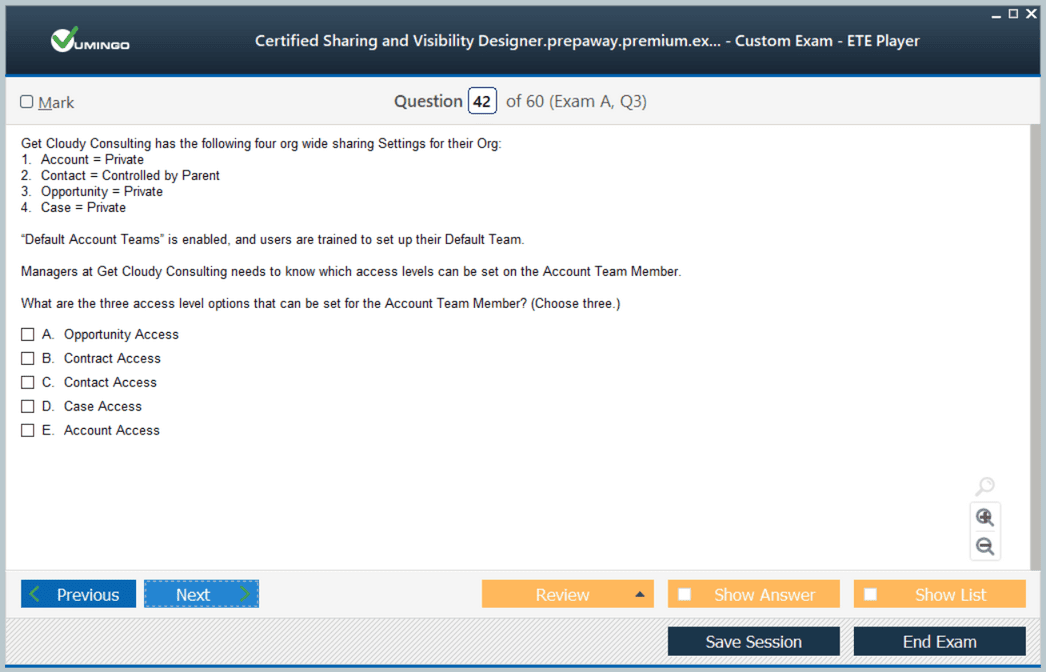
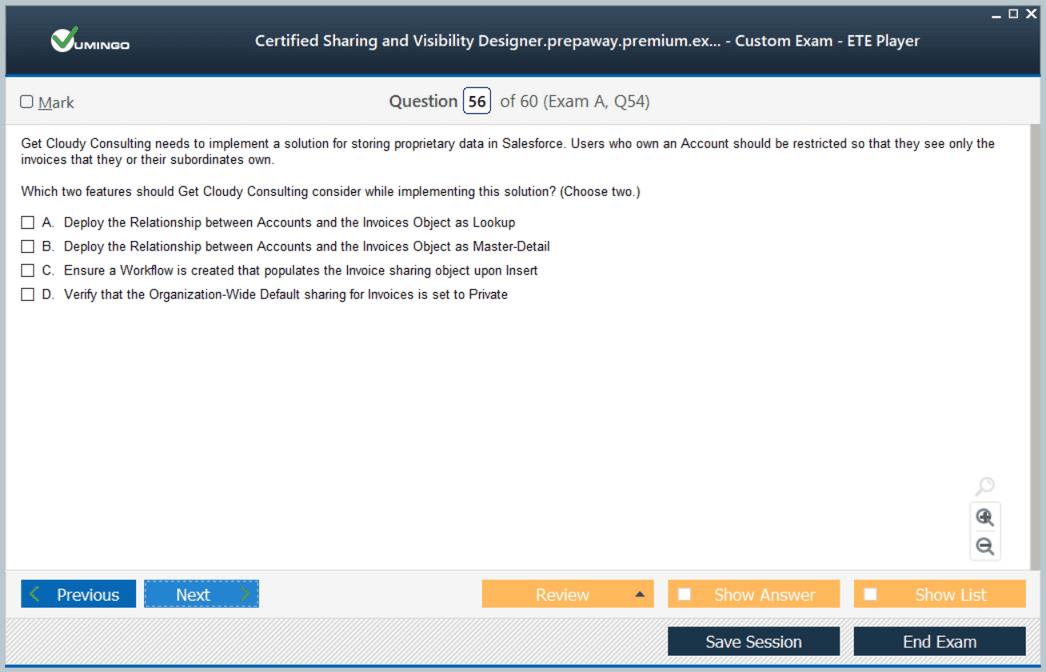




 83% students found the test questions almost same




