AZ-303 Azure Architect Technologies: Understanding the Retired Exam and the Modern AZ-305 Path
AZ-303, Microsoft Azure Architect Technologies, is a retired exam from the earlier Azure Solutions Architect Expert path. Microsoft retired AZ-303 and its companion AZ-304 on March 31, 2022. The exam can no longer be scheduled, but its subject matter remains historically useful because it represented the implementation side of Azure architecture: compute, networking, storage, identity, security, monitoring, and the technical decisions required to turn a design into a working environment.
The modern path is different. Today, Azure Solutions Architect Expert is centered on AZ-305, Designing Microsoft Azure Infrastructure Solutions, together with the Azure Administrator Associate prerequisite. That change matters for anyone who finds old AZ-303 courses or study plans. They can still teach durable Azure architecture concepts, but they should not be treated as a current certification roadmap or as an accurate representation of today’s product names and exam objectives.
The best way to use an AZ-303 page in 2026 is as a bridge between historical architecture skills and the current Azure Solutions Architect Expert credential. The Microsoft certifications program now places more explicit emphasis on design through AZ-305 while expecting candidates to bring operational Azure knowledge from administration. That split is logical: architects need both design judgment and enough implementation experience to know whether a proposed solution can actually be operated.
AZ-303 represented the implementation side of cloud architecture
The old exam was sometimes misunderstood as a catalog of Azure services. In practice, its value was the connection between architecture decisions and implementation mechanics. A solution architect cannot meaningfully recommend hub-and-spoke networking, private access, resilient compute, or identity boundaries without understanding how those patterns are configured and where they can fail.
That implementation orientation included virtual machines, platform services, storage, virtual networks, load balancing, identity, security, backup, monitoring, and automation. Candidates had to think across services because production systems rarely fail inside a neat exam-domain boundary. A network change can break storage access; an identity change can stop an application; a capacity choice can undermine disaster recovery.
Those relationships remain valuable even after the exam retired. What has changed is the certification mechanism and the platform detail around them. Old screenshots, service names, and objective weights should be treated as historical. The architectural reasoning—requirements, constraints, trade-offs, dependencies, failure modes, and verification—remains useful.
Identity and governance define who controls the platform
Azure architecture begins with boundaries. Tenants, management groups, subscriptions, resource groups, Azure role assignments, Microsoft Entra ID identities, policies, locks, and naming standards determine how teams divide responsibility. An architect should be able to design an environment where platform administrators, application teams, security teams, and automation identities have enough access to do their work without defaulting everyone to broad owner privileges.
Governance is not only security. Subscription and resource-group structure affects cost reporting, policy scope, deployment automation, quota management, and operational ownership. A design that mirrors the organization chart too literally can become rigid, while a completely flat structure can make controls difficult to apply. Good architecture uses the hierarchy to express stable control boundaries rather than temporary project convenience.
The current operational skills associated with AZ-104 are directly relevant here. Modern architects are expected to understand the administrative consequences of their designs, which is why current certification requirements connect Azure administration with architecture instead of relying on the retired AZ-303 implementation exam.
Network architecture must make every traffic path intentional
Virtual networks, subnets, peering, DNS, routes, firewalls, private endpoints, VPN gateways, ExpressRoute, load balancers, application gateways, and global routing services can create highly flexible topologies. The architect’s job is to reduce that flexibility to a design teams can understand and operate. Every important flow should have a known source, destination, name-resolution path, route, security boundary, and failure behavior.
Hub-and-spoke designs can centralize shared connectivity and controls, but they also create dependencies on routing and shared services. Private endpoints reduce public exposure but add DNS and network-management complexity. Peering simplifies connectivity but does not automatically create transitive routing. These details illustrate why implementation knowledge mattered in AZ-303: a diagram can look correct while a missing route or DNS zone makes the application unreachable.
Modern candidates who need deeper networking specialization can study AZ-700. For architects, the goal is not to become the person who operates every route table; it is to understand the design consequences well enough to choose an appropriate pattern and collaborate effectively with network engineers.
Compute design is a workload decision, not a preference for VMs or PaaS
Cloud architecture improves when teams choose the highest useful abstraction without ignoring application constraints. Virtual machines provide control but require operating-system management. App Service reduces infrastructure responsibility but imposes platform behavior. Containers improve packaging and consistency but still need orchestration, networking, security, and observability. Serverless functions work well for event-driven tasks but can create different execution and scaling considerations.
An architect should ask what the workload needs: statefulness, runtime control, scaling pattern, deployment frequency, operating-system dependencies, networking, compliance, latency, and recovery. The answer determines the hosting model. Choosing a service because the team already knows it can lock the application into unnecessary operational work or make future scale more difficult.
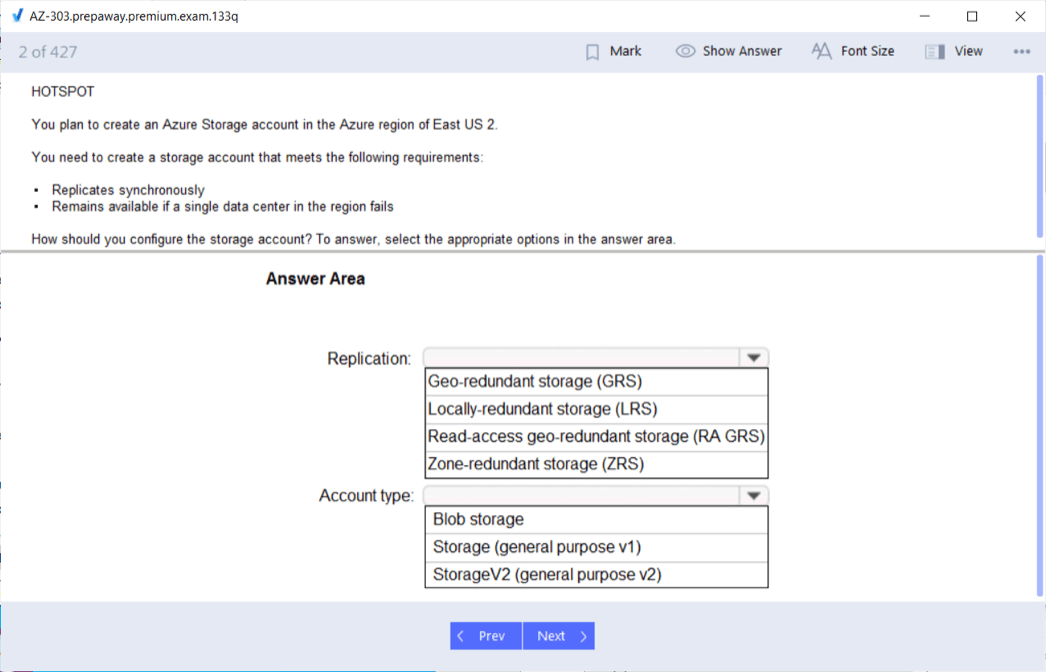
The same reasoning applies to availability. A single large VM with a backup may be recoverable but not highly available. A multi-instance platform deployment can tolerate instance failure but still depend on one database or one region. Architecture needs to trace the service as a whole.
Data architecture connects consistency, performance, availability, and cost
Azure provides relational databases, globally distributed NoSQL platforms, object storage, file services, managed disks, caches, analytics systems, and messaging services. The challenge is to match the data requirement to the service rather than force every dataset into a familiar technology. Transactional consistency, query patterns, latency, data volume, retention, replication, recovery, and integration all influence the decision.
Architecture also needs to include access and network controls. Data services may use Microsoft Entra authentication, managed identities, private endpoints, service firewalls, customer-managed keys, auditing, and backup policies. Security and recoverability are not add-ons after a database is selected; they are part of the service decision.
Cost can change dramatically with throughput, replicas, storage tier, backup retention, and data movement. A technically elegant global architecture can be financially inappropriate for an application used in one region. Architects should make resilience proportional to business requirements rather than defaulting every system to the maximum service tier.
Business continuity requires architecture across components
Recovery objectives should drive redundancy and failover. The application tier, database, storage, identity, network path, secrets, DNS, and external dependencies all contribute to service recovery. A design that protects only the database can still fail if the application configuration, certificate, route, or identity dependency is unavailable.
Region-pair assumptions and backup policies should be verified against the actual services being used. Some services support active-active patterns; others rely on active-passive failover or restore. Testing is essential. The practical discipline discussed in disaster-recovery planning applies directly: recovery steps, ownership, validation, and return-to-normal procedures must be exercised before a real incident.
Availability choices should also reflect failure probability and business impact. Engineering every internal tool for zero regional downtime can waste budget and complexity. Failing to protect a revenue-critical system can be far more expensive. Architecture is the process of making that trade-off explicit.
Monitoring closes the loop between design intent and real behavior
Architecture documents describe how a system should behave; monitoring reveals how it actually behaves. Azure Monitor, logs, metrics, traces, alerts, health signals, and application telemetry allow teams to detect saturation, failures, abnormal access, dependency latency, and deployment regressions. Good monitoring is designed with the system rather than bolted on after launch.
Architects should define which signals prove a service-level objective, which conditions require immediate action, and which trends indicate future capacity or reliability problems. Log retention, data volume, and privacy need to be balanced against diagnostic value. A design that emits every possible log but no actionable alert is not operationally mature.
Observability also supports governance. Resource inventory, configuration compliance, cost anomalies, and security posture can be monitored across subscriptions. The architect’s responsibility is to ensure the platform exposes enough evidence for operations teams to manage it safely.
Move from old AZ-303 material to current AZ-305 deliberately
Candidates who encounter AZ-303 training should first identify the architectural concept being taught, then verify the modern implementation in current Microsoft documentation. Virtual-network principles may still apply even if portal screens changed. Availability design remains relevant even if a service gained new features. Old command syntax, retirement dates, and certification requirements should not be trusted without current verification.
Modern Azure architecture, including the role of AZ-305 for Azure architects, emphasizes translating requirements into identity, governance, data, business-continuity, and infrastructure designs. AZ-303 knowledge can support that work, but the current exam is AZ-305, not a resurrected version of the old two-exam path.
Historical architecture material is especially useful for learning dependency thinking. Candidates can take an old reference design, identify every identity, network, compute, data, and monitoring dependency, and then redesign it with current Azure services. That exercise exposes which parts of cloud architecture are durable principles and which parts were tied to a specific generation of the platform.
The transition also reinforces an important professional habit: architecture documentation should record assumptions and decision rationale. When services or certification paths change, teams can revisit why a choice was made instead of treating an old diagram as permanent truth. That mindset is as useful in production governance as it is in exam preparation.
The useful legacy of AZ-303 is therefore practical architectural literacy. It encouraged candidates to understand how Azure services fit together at implementation depth. In 2026, that literacy should be carried forward into current administration and AZ-305 design work while the retired exam code is treated accurately as history.







 83% students found the test questions almost same





