
- Home
- Microsoft Certifications
- 98-368 Mobility and Devices Fundamentals Dumps
Pass Microsoft 98-368 Exam in First Attempt Guaranteed!
Get 100% Latest Exam Questions, Accurate & Verified Answers to Pass the Actual Exam!
30 Days Free Updates, Instant Download!


98-368 Premium File
- Premium File 66 Questions & Answers. Last Update: Nov 13, 2026
Whats Included:
- Latest Questions
- 100% Accurate Answers
- Fast Exam Updates
Last Week Results!
 83% students found the test questions almost same
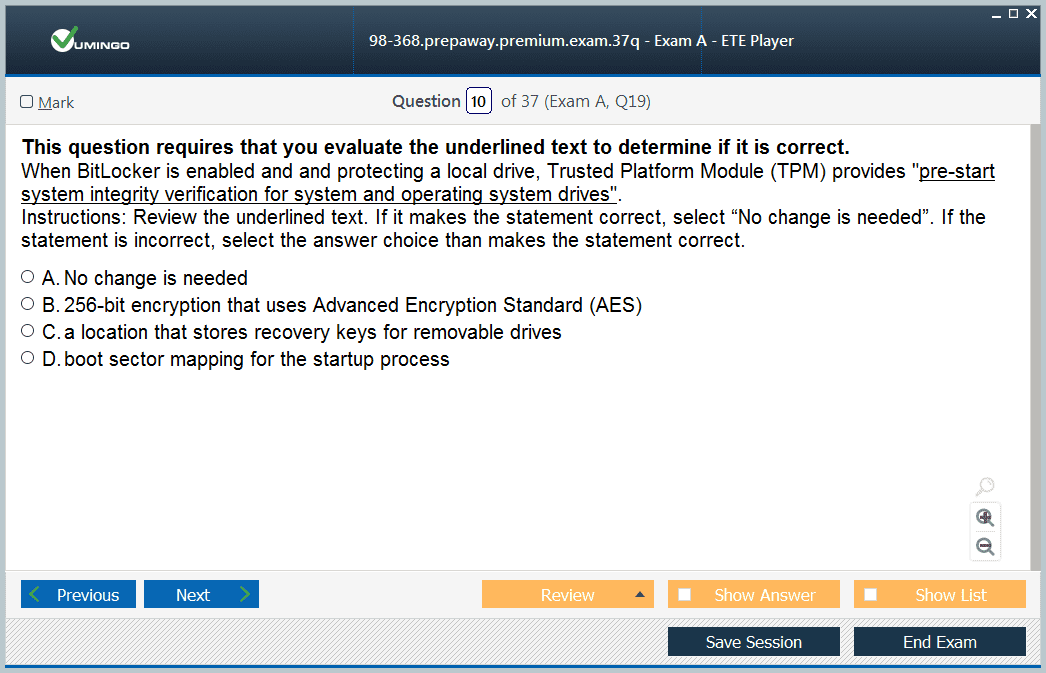
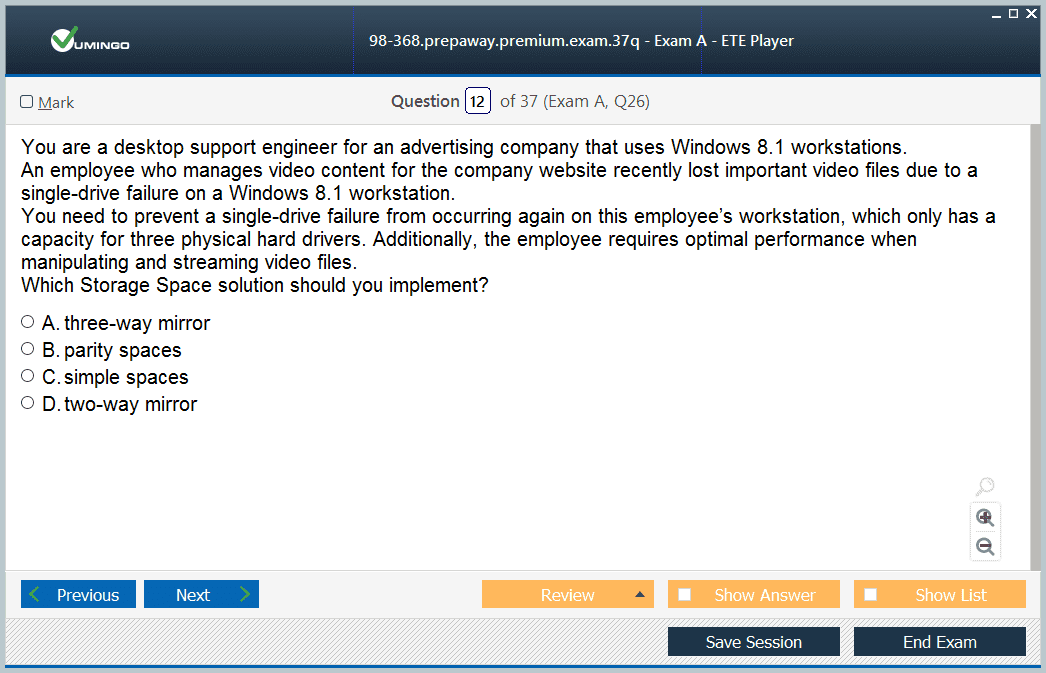
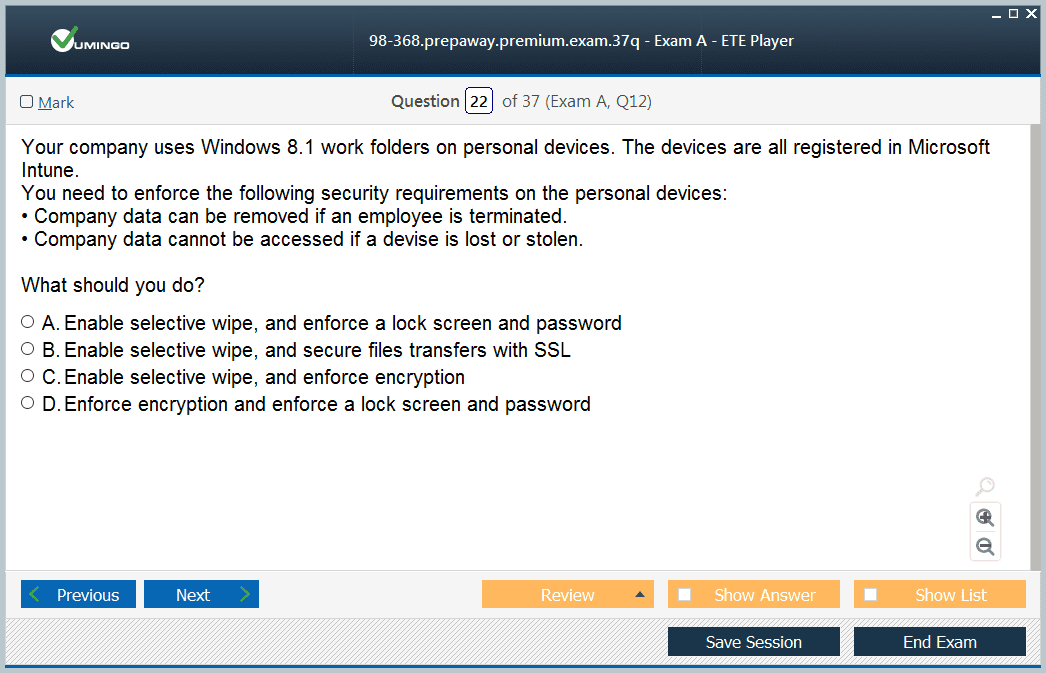
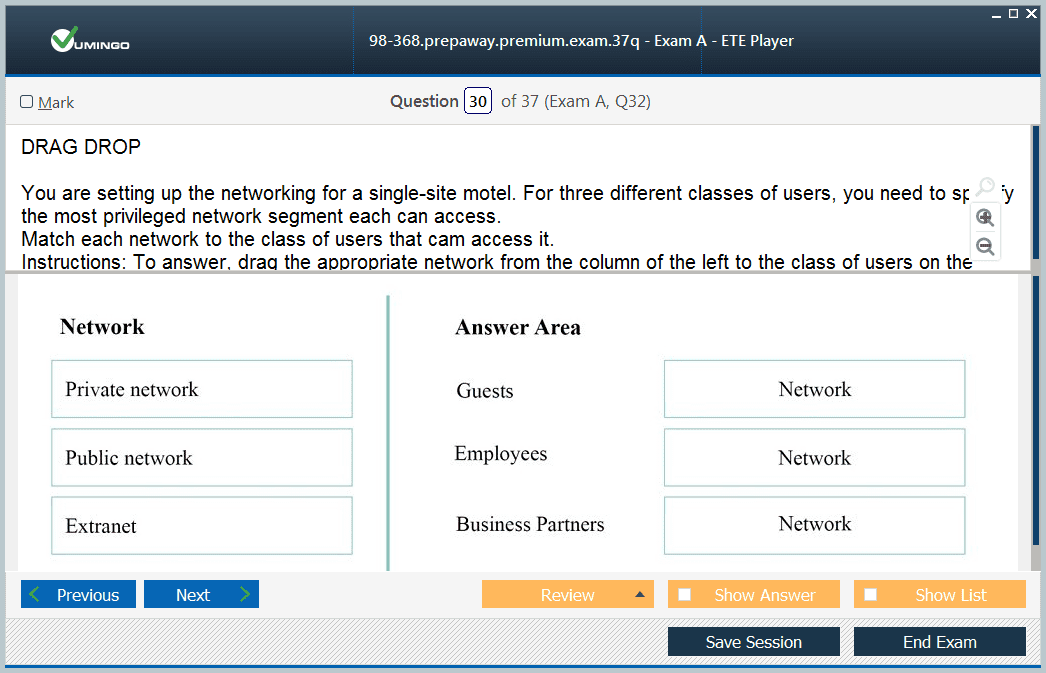
Exam 98-368, Mobility and Devices Fundamentals, was an MTA exam for foundational Windows device and mobility concepts. Microsoft retired the MTA program and this exam on June 30, 2022. Its historical objectives covered device configurations, data access and management, cloud services, device security, and enterprise mobility—an early view of the problems that later became central to modern endpoint management. Today, MD-102 Microsoft Endpoint Administrator addresses modern endpoint deployment and management through Microsoft Intune and related services, while the Microsoft 365 Endpoint Administrator certification defines a current role-based path. These are broader and more operational than the retired MTA exam, so the relationship is progression in subject matter rather than direct replacement. The 98-368 objective set expected candidates to understand how Windows devices are configured for real users. Account types, profiles, desktop settings, system options, application settings, and update behavior all shape the experience of a laptop or tablet. Configuration decisions should be repeatable so that devices do not become unique snowflakes that support teams cannot maintain. Updates keep the operating system and applications current, but update management also involves timing, compatibility, restart behavior, and recovery. A mobile worker may be affected differently from a desktop user if a large update requires bandwidth or downtime while traveling. Drive encryption protects data if a device is lost or stolen. The important distinction is that encryption addresses data at rest; it does not replace authentication, antimalware, or network security. Device configuration is strongest when those controls are planned together rather than enabled independently. Mobile users may work with local disks, removable storage, network shares, and cloud storage. Each location has different availability, synchronization, permission, and protection characteristics. A file stored only on one laptop is vulnerable to device loss, while cloud synchronization can improve availability but introduces identity and sharing considerations. File systems such as NTFS provide permissions and features that differ from simpler removable-media formats. Storage pools and related local storage concepts help administrators understand how capacity and resilience can be assembled. Candidates needed to recognize the appropriate location and protection method for business data. File and print sharing introduce network access controls. A resource may be available locally but inaccessible remotely because of permissions, network discovery, firewall rules, or identity. Troubleshooting should isolate storage, sharing, and authentication rather than changing all three at once. The MTA exam appeared during a transition from device-centered computing toward cloud-connected productivity. OneDrive, Office 365-era services, and Azure concepts allowed users to access data and applications beyond a single local machine. The exam therefore treated cloud services as part of device mobility rather than as a separate data-center topic. Cloud service models differ in how much responsibility remains with the customer. Even at a fundamentals level, learners should recognize that consuming a hosted application is different from managing virtual infrastructure. Identity, network access, data protection, and service availability still need clear ownership. Microsoft 365 core concepts help connect that early cloud transition to today’s integrated productivity environment. Those concepts should be read as current context, since the retired 98-368 exam used older product names and capabilities. Organizations need to decide which users and devices may access business data, what configuration is required, and how personal devices are handled. Bring Your Own Device can improve flexibility but creates questions about ownership, privacy, support, data separation, and what happens when an employee leaves. Enterprise mobility therefore combines identity, device state, applications, and data access. A managed corporate laptop can be configured more strictly than a personal phone, but both may need to reach the same business service. Policies should express the required security outcome without assuming every device is identical. Modern endpoint tools automate many of these decisions through enrollment, compliance policies, application protection, and conditional access. The historical exam introduced the conceptual problem: business data is mobile because users and devices move, so access controls cannot depend only on being inside an office network. Authentication proves who is using the device, while permissions determine what that identity can access. Strong device security also includes encryption, updates, antimalware, firewalls, and secure network use. Losing one layer should not automatically expose every resource. The retired 98-367 Security Fundamentals exam overlapped naturally with this domain because mobility increases the number of environments in which a device operates. A laptop may move between corporate, home, hotel, and public networks, each with different trust characteristics. Users should understand that an intranet, extranet, and public Internet connection are not equivalent trust zones. Modern zero-trust designs go further, but the fundamentals remain useful: verify identity, protect traffic, restrict access, and assume that network location alone is not enough proof of safety. Mobility becomes manageable when users can authenticate consistently and administrators can control access centrally. Traditional Active Directory, Microsoft account concepts, and cloud identity services represented different identity contexts in the MTA era. Candidates needed to understand why the account used to sign in influences which resources and settings become available. Single sign-on reduces repeated prompts by allowing one trusted authentication event to be reused across services, but it also increases the importance of protecting the identity. Multifactor authentication, device registration, and conditional policies later became common ways to strengthen that trust relationship. Identity synchronization and federation solve organizational problems where users need access across systems or clouds. The exam did not require today’s full Microsoft Entra administration, but it introduced the idea that mobility depends on identity traveling with the user rather than on one permanently trusted workstation. A single-device checklist is insufficient when an organization manages hundreds or thousands of endpoints. Administrators need standardized enrollment, configuration policies, application deployment, update controls, security baselines, inventory, remote actions, and reporting. Modern management platforms apply those controls centrally. Modern Microsoft 365 device and endpoint management illustrates the present-day operating model. Compared with 98-368, the scope includes much deeper service administration and security integration, but the historical domains of configuration, data, cloud access, and mobility are still visible underneath. Fleet management also changes troubleshooting. An issue affecting one device may be local, while an issue affecting an entire group may come from a policy, application deployment, identity setting, or service outage. Administrators need to compare scope before deciding where to investigate. A useful 98-368 lab can include a Windows client, multiple user accounts, local and cloud storage, encrypted volumes, shared folders, different network profiles, and deliberate policy changes. Move data between locations, change permissions, test offline behavior, and document what happens when the device is disconnected or a user changes. Because the exam retired in 2022, current learners should not study obsolete interface details solely for certification. Instead, use the historical objective groups to understand the problem space, then map each problem to the modern tools used in the environment they support. The broader Microsoft certifications portfolio now separates endpoint, identity, security, administration, and cloud roles. That specialization reflects how much enterprise mobility expanded. 98-368 remains useful as a foundation because it shows the common thread connecting those roles: secure access to organizational data from devices that are no longer fixed to one place or one network. Enterprise mobility is not only about connecting a device to data. Users also need applications that are installed, updated, configured, and licensed appropriately across corporate and personal endpoints. An unmanaged application can copy business data into an uncontrolled location even when the device itself meets basic security requirements. Modern management platforms can assign applications to users or devices, enforce required versions, remove software, and apply application-protection policies. Those capabilities go beyond the historical MTA objective depth, but they grow directly from the same mobility problem: work follows the user across devices, so organizations need consistent controls over both data and the software that handles it. Application troubleshooting at fleet scale also requires scope awareness. If one user cannot launch an app, the issue may be local installation or permissions. If an entire device group fails after a deployment, the administrator should inspect assignment rules, package detection, network access, and policy status. Mobility operations become manageable when configuration, identity, applications, and data are treated as connected systems. Remote access also changes the trust model. Virtual private networks, remote desktop services, browser-based applications, and cloud services each create different paths from a mobile device to organizational resources. Administrators must decide how the user authenticates, how traffic is protected, whether the device meets security requirements, and what data can be copied locally. The specific technologies evolve, but those questions remain central to enterprise mobility. Enrollment and compliance policies show how modern mobility management turns individual device settings into fleet-wide decisions. Administrators need a repeatable way to establish device ownership, apply configuration, require security baselines, distribute applications, and respond when a device falls out of compliance. A useful lab therefore includes both the user experience and the administrative view: enroll a test endpoint, apply a policy, observe the resulting state, and document what happens when the requirement is removed or violated. That exercise preserves the central 98-368 idea—controlled access from mobile devices—while expressing it in the management model used by current environments. The same policy model helps distinguish device configuration from access decisions, a distinction that remains central to modern endpoint administration.98-368 Mobility and Devices Fundamentals: Windows Device, Cloud, and Enterprise Mobility Foundations
Device configuration begins with users, settings, updates, and encryption
Data access spans local storage, file systems, sharing, and cloud services
Cloud services changed what mobility meant for Windows users
Enterprise mobility is a policy problem as much as a device problem
Device security depends on authentication, permissions, malware defense, and network context
Identity services connect users to resources across devices
Modern endpoint management operates at fleet scale
Use the retired exam to build a mobility lab with explicit trust decisions
Application management is part of mobility because users need controlled software everywhere
Why customers love us?
What do our customers say?
The resources provided for the Microsoft certification exam were exceptional. The exam dumps and video courses offered clear and concise explanations of each topic. I felt thoroughly prepared for the 98-368 test and passed with ease.
Studying for the Microsoft certification exam was a breeze with the comprehensive materials from this site. The detailed study guides and accurate exam dumps helped me understand every concept. I aced the 98-368 exam on my first try!
I was impressed with the quality of the 98-368 preparation materials for the Microsoft certification exam. The video courses were engaging, and the study guides covered all the essential topics. These resources made a significant difference in my study routine and overall performance. I went into the exam feeling confident and well-prepared.
The 98-368 materials for the Microsoft certification exam were invaluable. They provided detailed, concise explanations for each topic, helping me grasp the entire syllabus. After studying with these resources, I was able to tackle the final test questions confidently and successfully.
Thanks to the comprehensive study guides and video courses, I aced the 98-368 exam. The exam dumps were spot on and helped me understand the types of questions to expect. The certification exam was much less intimidating thanks to their excellent prep materials. So, I highly recommend their services for anyone preparing for this certification exam.
Achieving my Microsoft certification was a seamless experience. The detailed study guide and practice questions ensured I was fully prepared for 98-368. The customer support was responsive and helpful throughout my journey. Highly recommend their services for anyone preparing for their certification test.
I couldn't be happier with my certification results! The study materials were comprehensive and easy to understand, making my preparation for the 98-368 stress-free. Using these resources, I was able to pass my exam on the first attempt. They are a must-have for anyone serious about advancing their career.
The practice exams were incredibly helpful in familiarizing me with the actual test format. I felt confident and well-prepared going into my 98-368 certification exam. The support and guidance provided were top-notch. I couldn't have obtained my Microsoft certification without these amazing tools!
The materials provided for the 98-368 were comprehensive and very well-structured. The practice tests were particularly useful in building my confidence and understanding the exam format. After using these materials, I felt well-prepared and was able to solve all the questions on the final test with ease. Passing the certification exam was a huge relief! I feel much more competent in my role. Thank you!
The certification prep was excellent. The content was up-to-date and aligned perfectly with the exam requirements. I appreciated the clear explanations and real-world examples that made complex topics easier to grasp. I passed 98-368 successfully. It was a game-changer for my career in IT!


