98-349 Windows Operating System Fundamentals: What the Retired MTA Exam Covered
Exam 98-349, Windows Operating System Fundamentals, was part of Microsoft Technology Associate. Microsoft retired the MTA program and this exam on June 30, 2022, so 98-349 is no longer a current certification target. Its objective structure remains a useful historical foundation for understanding client operating systems: configuration, installation and upgrades, applications, files and folders, devices, and routine operating-system maintenance.
The modern Microsoft certification model is role-based and cloud-connected rather than organized around the old MTA fundamentals family. For endpoint work, MD-102 Microsoft Endpoint Administrator covers a much broader modern responsibility set involving Intune, Windows deployment, applications, security, and device management. That relationship is adjacent rather than a direct replacement. The broader Microsoft certifications context helps explain the change in credential architecture.
Operating system configuration begins with editions, settings, and user context
An operating system provides the environment in which applications, devices, files, users, and network connections operate. The 98-349 objective set expected candidates to recognize Windows editions and common configuration choices, then understand how settings affect the user experience and system behavior. This included desktop configuration, profiles, accessibility, power options, and administrative settings.
User profiles separate personal settings and data while allowing multiple people to share a device. Local and domain-oriented account concepts were important because authentication context determines access to files, applications, and system settings. A support technician needed to distinguish a user-specific problem from a machine-wide configuration problem before changing settings.
Administrative tools also matter at the fundamentals level. System information, Task Manager, management consoles, configuration utilities, and command-line tools expose different parts of the operating system. The goal is not memorizing every tool name; it is understanding which layer to inspect when a device is slow, a service is stopped, an application fails, or a setting affects all users.
Installation and upgrade decisions affect applications, data, and supportability
Installing Windows can mean a clean installation, an in-place upgrade, or a migration where user data and settings move to a new environment. Those paths have different consequences. A clean installation creates the most controlled baseline but requires applications and settings to be rebuilt. An upgrade can preserve more state but depends on compatibility and a supported source-to-target path.
Preparation should include checking hardware requirements, architecture, drivers, disk space, application compatibility, and backup readiness before installation. The choice between 32-bit and 64-bit systems was particularly relevant during the technologies represented by the MTA exam because application and driver compatibility could differ significantly.
An installation is not complete when the desktop first appears. Drivers, updates, activation, security software, user data, and recovery options must be verified. This operational perspective is still useful in modern endpoint deployment even though current organizations may use cloud provisioning and automated deployment tools.
Applications interact with services, permissions, and compatibility settings
Managing applications includes installation, removal, default associations, compatibility, background services, and troubleshooting. An application failure can be caused by missing permissions, an unavailable dependency, architecture mismatch, corrupted settings, or a service that is not running. Fundamentals preparation should teach candidates to isolate the layer causing the failure.
Processes and services are related but different. A process is a running instance of a program or component, while services often run in the background and can start independently of a user session. Task Manager and service-management tools help identify resource consumption and operational state, but stopping unknown services without understanding their role can create additional problems.
User Account Control and privilege boundaries are also part of application management. Applications that require administrative rights should be understood rather than permanently bypassing protections. A support workflow should determine why elevation is required and whether the application is appropriate for the device.
Files and folders combine storage, permissions, encryption, and recovery
File management is more than copying documents. Candidates needed to understand file systems, paths, attributes, permissions, compression, encryption, sharing, and the difference between local and network locations. NTFS permissions and ownership help determine who can read or modify data, while sharing permissions add another access layer in network scenarios.
Encryption protects data from unauthorized access in a different way from permissions. Permissions depend on the operating system enforcing user rights, while encryption changes how the data is stored. Backup and recovery address yet another risk: accidental deletion, hardware failure, corruption, or unwanted changes. These controls solve different problems and should not be treated as interchangeable.
Good troubleshooting begins by identifying whether a file problem is about existence, path, permissions, encryption, lock state, or application behavior. Repeatedly changing permissions until a file opens can create security exposure if the real cause was elsewhere.
Device management connects drivers, hardware resources, and troubleshooting
Windows depends on drivers to communicate with hardware such as storage, displays, printers, network adapters, and peripheral devices. Device Manager exposes status, driver versions, hardware identifiers, and conflicts. A device problem may require updating, rolling back, disabling, reinstalling, or replacing a driver rather than changing the application using the device.
Storage devices introduce additional concepts such as partitions, volumes, removable media, and disk health. Display and input devices have their own configuration layers. The historical exam emphasized the ability to recognize common device categories and use operating-system tools to determine whether Windows can communicate with them correctly.
Modern endpoint administration broadens this work into fleet management. The Microsoft 365 Endpoint Administrator certification includes policy, enrollment, application deployment, identity, and security across many devices. That scope is far beyond 98-349, but the troubleshooting habit of separating hardware, driver, operating system, and application layers remains valuable.
Maintenance is a cycle of updates, monitoring, recovery, and cleanup
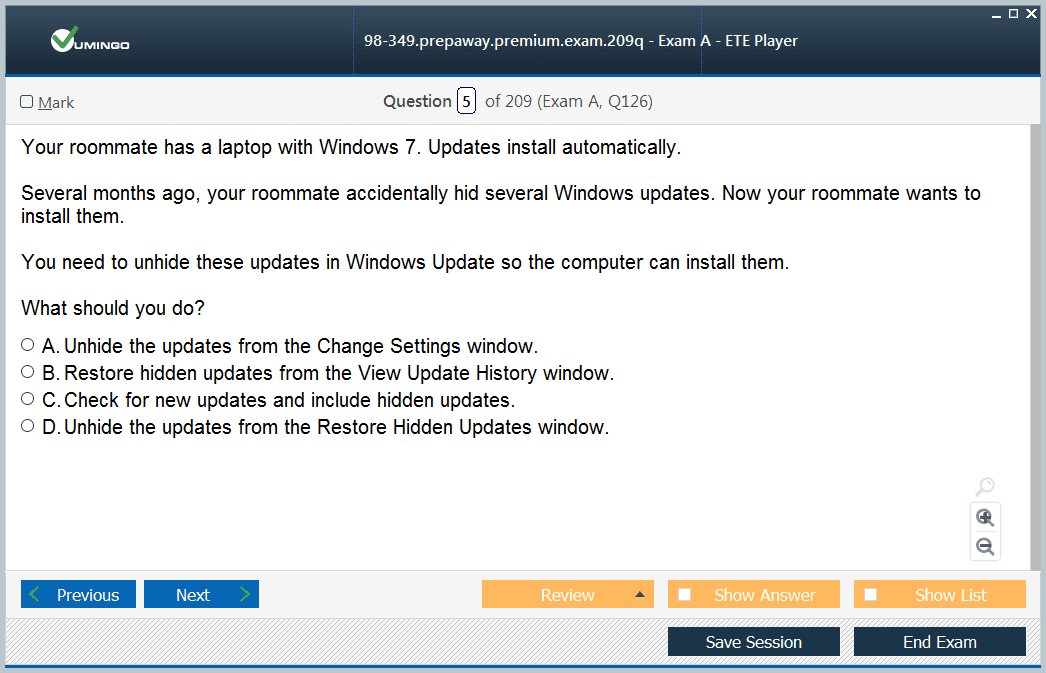
Operating systems require ongoing maintenance after installation. Updates address security and reliability, while monitoring tools help identify performance or resource problems. Disk cleanup, scheduled tasks, event information, restore points, recovery options, and system utilities support routine operation and repair.
Updates should be treated as controlled change. A device needs enough disk space, compatible drivers, and a recovery plan when an update has significant impact. In enterprise environments, testing and phased deployment reduce risk. The MTA exam dealt with a simpler client context, but the underlying reason for change control was already present.
Recovery options are most useful when prepared before failure. A restore point, recovery drive, backup, or known installation source can shorten downtime. Support technicians should understand which method restores system configuration, which restores personal data, and which effectively rebuilds the device.
Security fundamentals intersect with operating-system fundamentals
Client operating systems enforce authentication, authorization, software execution, updates, malware defenses, and local security settings. The retired 98-367 Security Fundamentals exam represented a companion MTA perspective on security layers, operating-system security, network security, and protective software. Linking the two historically makes sense because securing a device depends on understanding how the operating system is configured.
Antimalware, firewalls, account controls, patches, and encryption address different attack paths. Security weakens when users depend on only one control. A fully patched machine can still be compromised through stolen credentials, and strong passwords do not protect an unpatched vulnerable service. Defense requires multiple layers.
Modern Microsoft 365 device and endpoint management shows how those client-management concerns expanded into cloud-managed fleets. It should be read as modern operational context, not as material that the retired 98-349 exam tested.
Use 98-349 as a troubleshooting foundation, not a current exam plan
Because the exam retired in 2022, there is no reason for a new candidate to build a certification plan around scheduling 98-349. The better use is to take its domains as a structured checklist: install a client operating system in a lab, create users, configure settings, add devices, manage applications, set permissions, test recovery, and troubleshoot deliberate faults.
A lab should include consequences. Break a driver and recover it. Create a permissions problem and determine why access fails. Fill disk space, stop a noncritical service, misconfigure a startup application, or create a problematic user profile. Restoring the system teaches more than reading command descriptions.
The enduring MTA lesson is foundational reasoning. Current tools may use Intune, cloud identity, automated deployment, and security platforms, but an administrator still needs to understand what a client operating system is doing underneath those management layers. That foundation makes modern endpoint concepts easier to diagnose when automation does not behave as expected.
Command-line tools help reveal the system behind graphical utilities
Windows fundamentals also included command-line and management-console thinking. A graphical settings page may hide the details of processes, network configuration, file paths, or services, while command-line tools can expose concise diagnostic information and can be repeated consistently. Even entry-level technicians benefit from understanding that the same operating-system state can often be inspected through multiple interfaces.
PowerShell later became increasingly important for Windows administration because commands can be scripted and applied consistently across systems. The retired 98-349 exam did not represent today’s automation-heavy endpoint role, but learning to move between graphical tools and command-line evidence develops a useful troubleshooting habit: observe the actual system state, make one deliberate change, and verify the result.
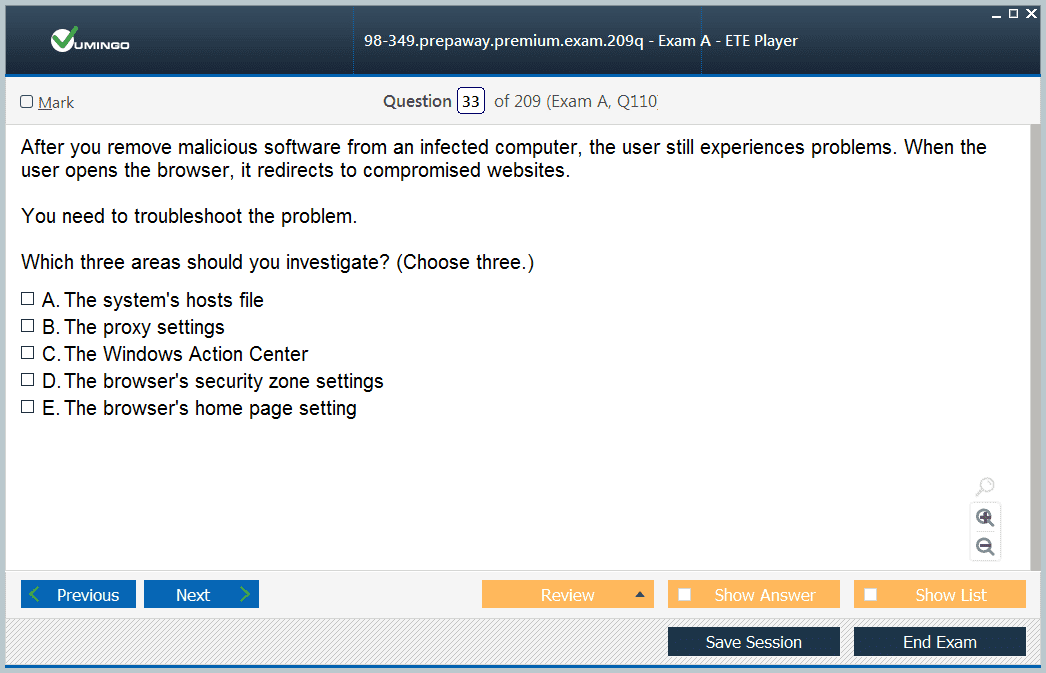
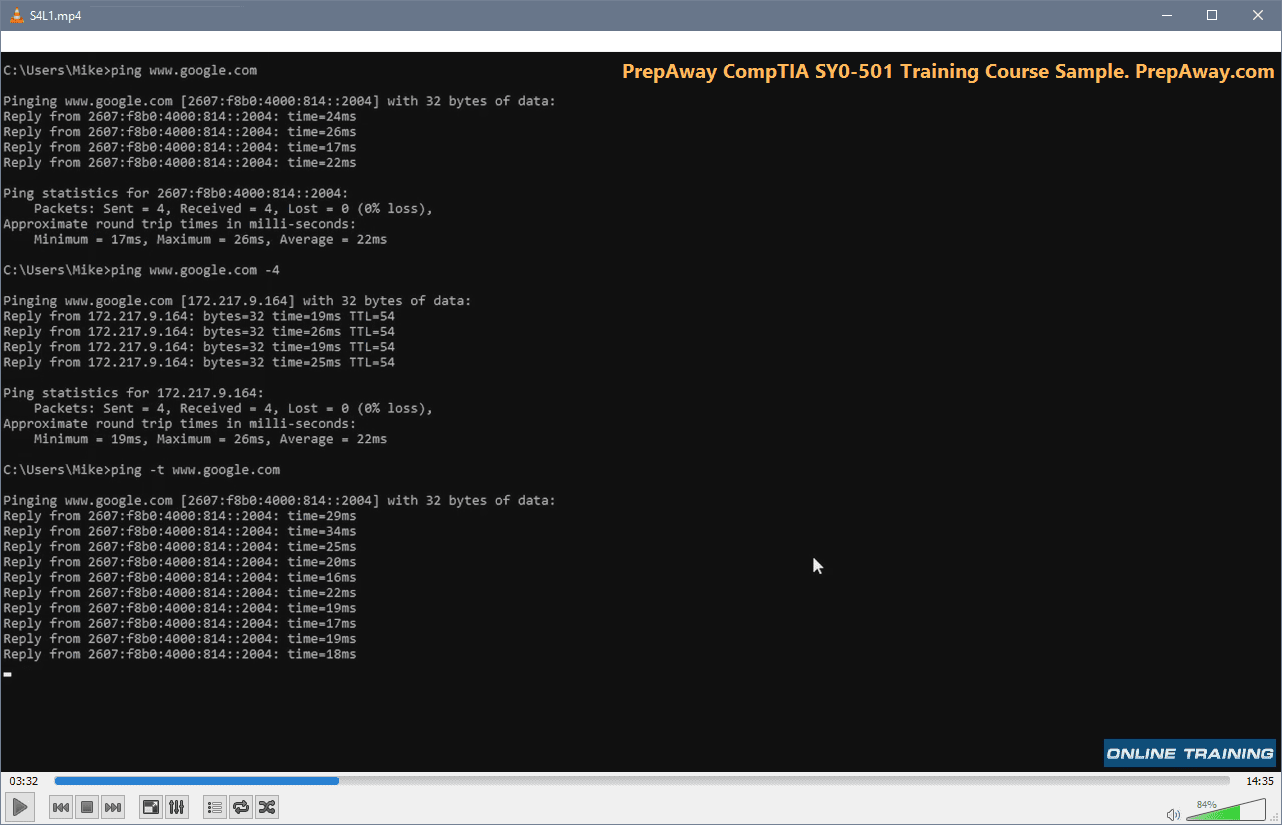
Network configuration is another useful bridge between client support and modern endpoint work. A device can be healthy yet unable to reach a service because DNS, addressing, gateway settings, proxy configuration, or firewall rules are wrong. Checking those layers in a consistent order prevents technicians from reinstalling applications or changing accounts when the real problem is basic connectivity.
Event logs and startup behavior add another layer to operating-system troubleshooting. A machine that boots slowly, loses a service, or fails after an update often leaves evidence in system logs before the user can describe the failure precisely. Reading timestamps, service states, update history, and device events helps narrow the problem before making changes. Learners revisiting 98-349 can build this habit by reproducing simple faults in a lab, observing the evidence Windows records, and then reversing the change. The goal is to connect symptoms to system state rather than rely on trial-and-error fixes.








 83% students found the test questions almost same





